
Is allegro.spspsp.shop safe?
http://allegro.spspsp.shop/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (59 of 93 engines answered): completed
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records · not available: did not fully complete
- web research: completed
Allegro-branded host on an unrelated .shop domain is flagged as phishing by the browser threat feed and seven security vendors
allegro.spspsp.shop borrows the Allegro name inside a hostname on the unrelated spspsp.shop domain, and the address itself is classified as social engineering by the browser threat feed and as phishing by 7 of 93 antivirus engines. The host serves no content of its own: it redirects the browser to the genuine Polish marketplace allegrolokalnie.pl, so the page a visitor sees is the real Allegro Lokalnie layout, not a storefront run by this operator. The combination of a brand-lookalike address, a decisive phishing verdict and an undisclosed operator puts this in the Dangerous band.
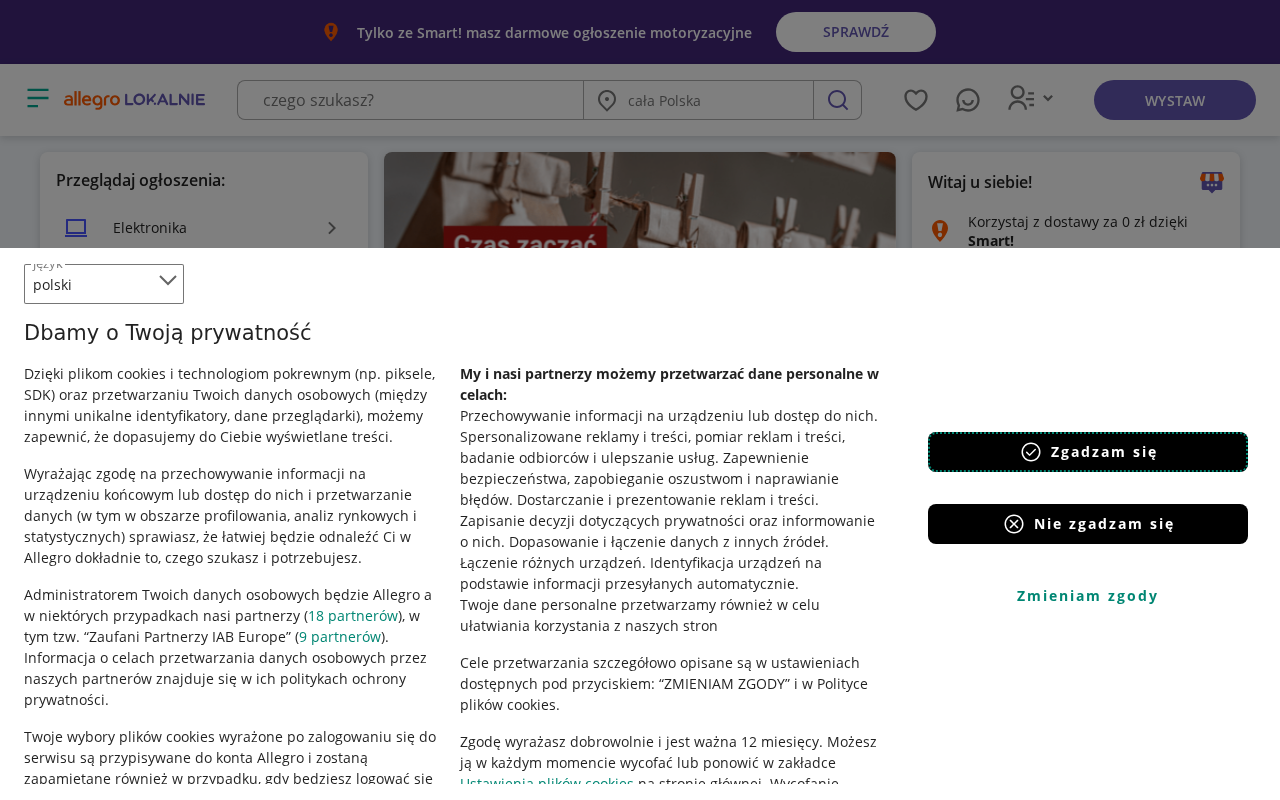 Saved site captureCaptured safely during this scan9 antivirus engines flagged this URLalphaMountain.ai, Forcepoint ThreatSeeker, G-Data, Google Safe Browsing, Kaspersky
At a glance
Saved with this scan; each value is explained in the sections below.
Domain age
Not available
Certificate
Valid
Expires Jan 16, 2027 (64d)Hosting
Poland (PL)
Allegro sp. z o.o.Popularity
Radar ranks spspsp.shop, not this subdomain
Antivirus
9/59
9 antivirus engines flagged this URLSafe Browsing
Flagged
This URL appears on threat listsCommunity
No reviews yet
Checked
Nov 13, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 12/100
Dangerous covers scores 1–20. 5 findings pulled the score down; 1 pushed it up.
What pulled the score down
- Decisive7 independent antivirus families reported an adverse result.
- DecisiveA browser-protection feed identifies this URL as malware or social engineering.
- Moderate3 independent sources carry complaints or warnings about this site, including: "Allegro 网络钓鱼与冒充"
- Moderate3 independent sources carry complaints or warnings about this site, including: "Nie prowadzi on do oficjalnej domeny Allegro, lecz do podejrzanej domeny allegro-poland.eu.cc"
What pushed the score up
- SupportsThe redirect destination sits on Allegro-owned infrastructure with an abuse score of 0 and a valid TLS certificate.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
Lost money or shared details on allegro.spspsp.shop? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on allegro.spspsp.shop, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 · Investigation Brief
Investigation Brief
allegro.spspsp.shop borrows the Allegro name inside a hostname on the unrelated spspsp.shop domain, and the address itself is classified as social engineering by the browser threat feed and as phishing by 7 of 93 antivirus engines. The host serves no content of its own: it redirects the browser to the genuine Polish marketplace allegrolokalnie.pl, so the page a visitor sees is the real Allegro Lokalnie layout, not a storefront run by this operator. The combination of a brand-lookalike address, a decisive phishing verdict and an undisclosed operator puts this in the Dangerous band.
Security vendors flag this exact address as phishing
The browser threat feed returns a SOCIAL_ENGINEERING threat for this URL, the category used for pages built to trick people into handing over credentials or payment details. The browser-protection feed behind that result identifies the address as malware or social engineering.
The multi-engine malware scan records 7 malicious and 2 suspicious detections across 93 engines, and the antivirus aggregate names seven independent families reporting an adverse result, including alphaMountain.ai, Forcepoint ThreatSeeker and G-Data. These are current results on the live address, not an old scan of a previous owner.
Independent reporting on Allegro impersonation describes look-alike Allegro domains that do not lead to the official site, and one brand-tracking source counts dozens of sites impersonating the Allegro brand. That context matches the naming pattern seen here.
A brand name on a foreign domain that forwards to the real marketplace
The hostname puts the Allegro brand in front of spspsp.shop, a domain unrelated to Allegro. Requesting the address returns a 302 redirect to https://allegrolokalnie.pl/, and the captured page is the genuine Allegro Lokalnie layout with its logo, search bar and category list.
The only commercial path observed is that redirect. The buttons on the landing page are Allegro Lokalnie's own category navigation and a Smart! promotion banner, not a checkout or payment step attributable to spspsp.shop, and no affiliate or tracking parameters appeared in the redirect chain.
Nothing about the operator of spspsp.shop is disclosed, and the contact details on the landing page belong to Allegro rather than to this host. Why a look-alike address forwards to the real site is unresolved: it may be a parked or abused subdomain, or the redirect may be conditional and serve different content to other visitors.
Clean encryption and a clean destination do not clear the address
The saved TLS check found a valid encrypted connection, and the IP the browser landed on belongs to Allegro with an abuse confidence score of 0 across no saved reports. Both describe the redirect destination, not the spspsp.shop host, and encryption only shows the connection is private.
No credential form, popup, download attempt or notification request was observed during the render, so the harm here is the deceptive brand-lookalike address and its phishing classification rather than an observed theft. The decisive vendor verdicts are what place the score in the Dangerous band.
Why the score is 12
02 · Security Evidence
Security evidence
Antivirus Engines
9/ 93
detectionsFresh result
9 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 7
- Suspicious
- 2
- Total
- 93
- Malicious7
- Suspicious2
- Clean50
- Undetected34
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | phishing |
| Forcepoint ThreatSeekerMalicious | phishing |
| G-DataMalicious | phishing |
| Google Safe BrowsingMalicious | phishing |
| KasperskyMalicious | phishing |
| SOCRadarMalicious | phishing |
| SophosMalicious | phishing |
| ESETSuspicious | suspicious |
| FortinetSuspicious | spam |
All 93 engine results
- alphaMountain.ai - phishing - Malicious
- Forcepoint ThreatSeeker - phishing - Malicious
- G-Data - phishing - Malicious
- Google Safe Browsing - phishing - Malicious
- Kaspersky - phishing - Malicious
- SOCRadar - phishing - Malicious
- Sophos - phishing - Malicious
- ESET - Suspicious
- Fortinet - spam - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Fortra - Unrated
- GCP Abuse Intelligence - Unrated
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- LevelBlue - Unrated
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiPhishing
- Forcepoint ThreatSeekerphishing and other frauds
- Sophosphishing and fraud
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Detected threat categories: SOCIAL_ENGINEERING.
What we observed
Visual context from the captured page
Screenshot shows the Allegro Lokalnie header with the 'allegro LOKALNIE' logo, search bar, 'WYSTAW' button and category list (Elektronika, Moda, Dom i Ogród...), i.e. the genuine Allegro Lokalnie layout reached after the redirect. A large Polish cookie-consent dialog ('Dbamy o Twoją prywatność') overlays the page with 'Zgadzam się' and 'Nie zgadzam się' buttons and mentions Allegro as data controller with 18 partners. Top banner reads 'Tylko ze Smart! masz darmowe ogłoszenie motoryzacyjne' with a 'SPRAWDŹ' button, matching the captured page block.
What the captured page showed
3 observations- 01
Screenshot shows the Allegro Lokalnie header with the 'allegro LOKALNIE' logo, search bar, 'WYSTAW' button and category list (Elektronika, Moda, Dom i Ogród...), i.e. the genuine Allegro Lokalnie layout reached after the redirect.
- 02
A large Polish cookie-consent dialog ('Dbamy o Twoją prywatność') overlays the page with 'Zgadzam się' and 'Nie zgadzam się' buttons and mentions Allegro as data controller with 18 partners.
- 03
Top banner reads 'Tylko ze Smart! masz darmowe ogłoszenie motoryzacyjne' with a 'SPRAWDŹ' button, matching the captured page block.
Browser behavior
What our isolated browser recorded while it loaded the page. Host names only: no full addresses are published.
- Pop-ups
- 0
- Download attempts
- 0
- Notification prompts
- 0
- Navigations
- 1
- Other hosts contacted
- 9
Where the page went
- First loadallegrolokalnie.plOther site
Hosts on our aggressive-advertising list
None contacted.
Test clicks
No test click was made on this page.
What the page says about itself
Quoted from the pages we read: the site's own words, not our findings.
- Page title
Allegro Lokalnie - Wystaw ogłoszenia za darmo i kupuj od osób z Twojej okolicy
- Meta description
Wystaw ogłoszenie za darmo na Allegro Lokalnie, sprzedawaj i kupuj bezpiecznie od osób z Twojej okolicy. Upoluj lokalne perełki w atrakcyjnych cenach!
Pages we read
- Main page/Read
03 · Investigation Story
Investigation story
What the site claims
Allegro Lokalnie - Wystaw ogłoszenia za darmo i kupuj od osób z Twojej okolicy
What we observed
Saved browser evidence recorded cross domain landing.
What independent research found
4 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Login Portal
Observed behavior
Evidence behind this classification
- 01No credential form, popup or download was observed during the render; the landing page's contacts belong to Allegro, not to this host.
- Also 8 listed above
Web research findings
Independent findings for allegro.spspsp.shop, including public complaints, named review sources, registration records, and look-alike-domain evidence.
- ScanMalware.comopen
"Allegro 网络钓鱼与冒充"
- ScanMalware.comopen
"Allegro phishing & impersonation E-commerceallegro.pl 62 Sites impersonating it"
- Thai PBS Verifyopen
"ชวนเปิดร้านบนแพลตฟอร์มที่ใช้ชื่อคล้าย Allegro ซึ่งเป็นเว็บอีคอมเมิร์ซของโปแลนด์ แต่สะกดชื่อโดเมนผิด"
- Telepolis.plopen
"Nie prowadzi on do oficjalnej domeny Allegro, lecz do podejrzanej domeny allegro-poland.eu.cc"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domainallegro.spspsp.shop
- Redirects toallegrolokalnie.pl
- Hosted byAllegro sp. z o.o.
- Referenceslokalnie-prod-assets.storage.googleapis.com · googletagmanager.comand 6 more
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
At the scan on Nov 13, 2026: 68% of the validity period had passed
This is the certificate of allegrolokalnie.pl, the site this URL lands on. Certificate issued for *.allegrolokalnie.pl.
This is the address of allegrolokalnie.pl, the site this URL lands on.
Analytics and ads
- Google Tag Manager
- Google Analytics
- Meta Pixel
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1302http://allegro.spspsp.shop/
- 2200https://allegrolokalnie.pl/cross-domain
Server Reputation
Sites linked to this one
- On the same server IP3 sites with a report: 3 Dangerous
3 linked sites with a report. Each dot takes that site's own rating; a shared detail is a lead, not proof.
Other sites we have reports for that share something checkable with this one. A shared detail is a lead to compare, not proof that the sites have the same owner or the same risk; each keeps its own rating.
On the same server IP
Also served from 5.134.215.224 (Allegro sp. z o.o.). Unrelated sites can share a server, so this is a lead, not proof.
- olx.spspsps.shopDangerous
- allegro.lokalna-482012.sbsDangerous
- allegrolokalnie.lokalna-067.sbsDangerous
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
Grouped by what each domain is for. in page: named in the page’s HTML. contacted: the browser loaded it while rendering the page. ad list: on our aggressive-advertising list.
Analytics & tracking4
- connect.facebook.netin page
- google-analytics.comin page
- googletagmanager.comin pagecontacted
- sentry.iocontacted
CDN & fonts3
- assets.allegrostatic.comcontacted
- lokalnie-prod-assets.storage.googleapis.comin pagecontacted
- storage.googleapis.comin pagecontacted
Other / unknown6
- a.allegroimg.comin pagecontacted
- allegrolokalnie.plcontacted
- cl.qualaroo.comin page
- googleoptimize.comin page
- ngacm.comcontacted
- ngastatic.comcontacted
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
maliciousMalware, phishing, credential theft and hostile infrastructure.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 9 of 93 engines flagged | Completed | Adverse | fresh · analysed Nov 13, 2026 |
| Browser protection | 1 browser threat category matched | Completed | Adverse | this scan · Nov 13, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 13, 2026 |
| Visual evidence | 3 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 13, 2026 |
| Independent research | 4 independent findings were saved | Completed | Adverse | this scan · Nov 13, 2026 |
- Antivirus
- Result9 of 93 engines flagged
- CompletionCompletedFindingAdverse
- Freshnessfresh · analysed Nov 13, 2026
- Browser protection
- Result1 browser threat category matched
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 13, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 13, 2026
- Visual evidence
- Result3 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 13, 2026
- Independent research
- Result4 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 13, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is allegro.spspsp.shop a scam or a legit website?
Is allegro.spspsp.shop safe to use?
I already paid or entered my details on allegro.spspsp.shop — what should I do?
Can I get my money back from allegro.spspsp.shop?
Did allegro.spspsp.shop steal my password or personal information?
How do I report allegro.spspsp.shop?
allegro.spspsp.shop looks professional — how can it still be a scam?
Has allegro.spspsp.shop been flagged by antivirus engines?
Is allegro.spspsp.shop on any phishing or malware blacklists?
Where is allegro.spspsp.shop hosted?
How often is the allegro.spspsp.shop report updated?
08 · Final Verdict
Final verdict
Allegro-branded host on an unrelated .shop domain is flagged as phishing by the browser threat feed and seven security vendors
allegro.spspsp.shop borrows the Allegro name inside a hostname on the unrelated spspsp.shop domain, and the address itself is classified as social engineering by the browser threat feed and as phishing by 7 of 93 antivirus engines. The host serves no content of its own: it redirects the browser to the genuine Polish marketplace allegrolokalnie.pl, so the page a visitor sees is the real Allegro Lokalnie layout, not a storefront run by this operator. The combination of a brand-lookalike address, a decisive phishing verdict and an undisclosed operator puts this in the Dangerous band.
09 · Community
Community
Are you the owner of allegro.spspsp.shop?Verify and reply