
Is auth.platorelay.com safe?
https://auth.platorelay.com/a?d=4AfZJcbAwsfTCfmKXGZcD8Ssp1zQp1PgnQ71zBG3t44QceGUlQWK3EXsZQTbQvDtqNqzvL8QIMC5t0VyDyHsovQy387Ks4w3towCVwm0vOzuKA2ZeI866Pq6iTld9Z2MtFJk8teF6xTZEq04aFpPGhw26EUbUaQTQK7vp8WFYdTtNwVuwRFTG7npHo1TSl2fc3RXjzQrfR8A5tdKEAX031AfF9SDlhwhgLcbvk1XPSaDuytrZRvZmdo4BtlwLEjNfBuBekgDLXVHevLD2DnBfyolBLYJP4PXdFoSPHefUeXFU8A8F47R285T5TLeTgmVvx6B9rCD5DT6FIVqQTnxSjZkHQiPcsjuFpUvRYMzXSTTcGcPKy1o203m89efX6DX0kmHmuE9KmbNQZeRTevGEW4KOZcs25CH7yknV6KDUF7Nm0CHWDl90CNzKuEXMV9CVROKfhY3TGpVWcZstzFyIqGj4BXDPgSUXcVXALyYWEBsbppfRVv
Coveragecomplete3 of 4 applicable core capabilities
Platoboost uses a keysystem-style page with a disruptive cross-domain redirect
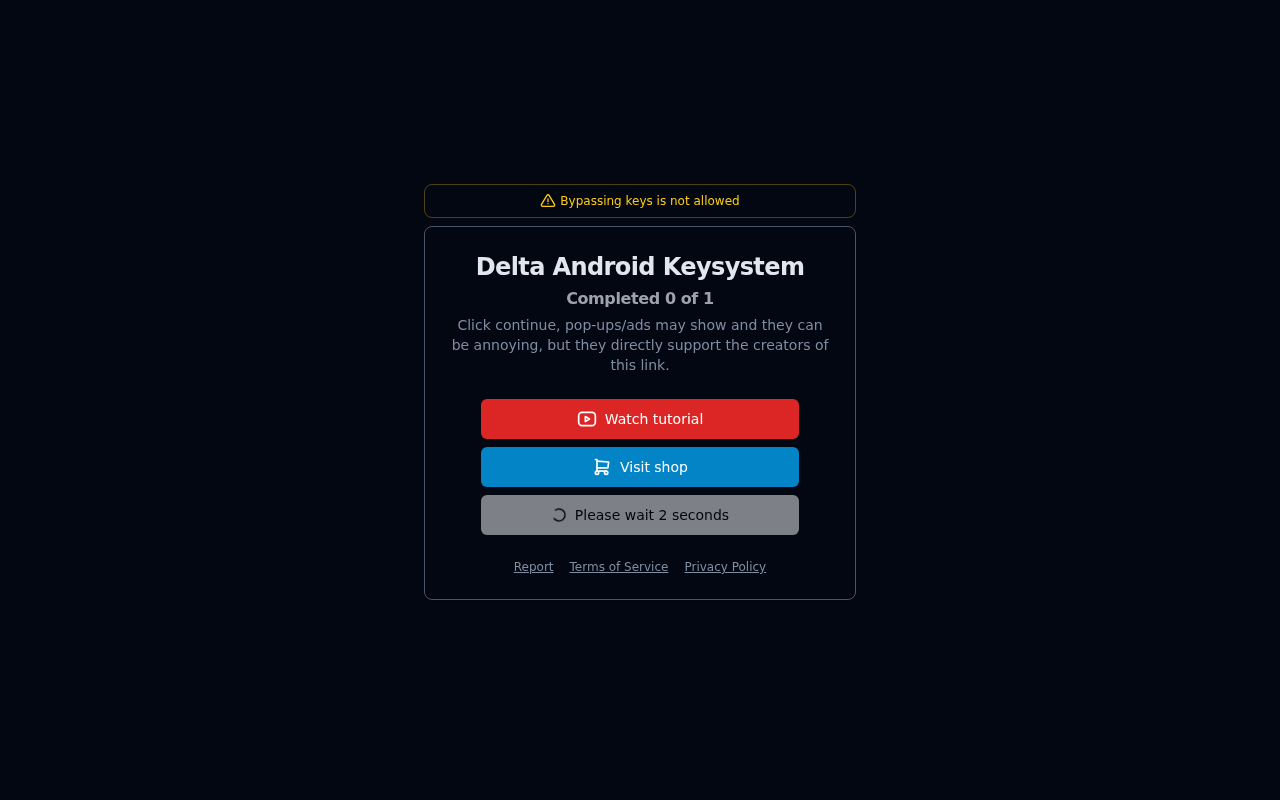
The page presents a “Delta Android Keysystem” with “Watch tutorial” and “Visit shop” controls, while a primary control was observed opening an unrelated external domain. Although saved reputation checks found no current threat warning or malicious detections for the target, the redirect behavior creates meaningful visitor risk and supports a Moderate Risk score.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
The page presents a “Delta Android Keysystem” with “Watch tutorial” and “Visit shop” controls, while a primary control was observed opening an unrelated external domain. Although saved reputation checks found no current threat warning or malicious detections for the target, the redirect behavior creates meaningful visitor risk and supports a Moderate Risk score.
The interface leads beyond the target domain
The visible interface includes “Watch tutorial” and “Visit shop” options on auth.platorelay.com.
Testing found that a primary play, convert, continue, or download control opened an unrelated destination on moonlighthathel.org. This cross-domain jump is the strongest concern because visitors may leave the assessed site when trying to proceed.
Clean checks reduce—but do not remove—the concern
The saved checks showed a valid encrypted connection, no threat warning, and zero malicious or suspicious detections across 92 engines.
Those checks support the absence of a detected technical threat at scan time, but they do not make the observed unrelated redirect safe or establish the safety of its destination.
Why the score is 58
A primary control opened an unrelated external destination on another domain. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
0/ 92
No detectionsFresh result
No detections across 92 engines
No antivirus engine in this saved scan raised an adverse result. This is one signal, not a guarantee.
- Malicious
- 0
- Suspicious
- 0
- Total
- 92
All 92 engine results
- 0xSI_f33d - unrated - Clean
- Abusix - clean - Clean
- Acronis - clean - Clean
- ADMINUSLabs - clean - Clean
- AILabs (MONITORAPP) - clean - Clean
- AlienVault - clean - Clean
- alphaMountain.ai - unrated - Clean
- AlphaSOC - unrated - Clean
- Antiy-AVL - clean - Clean
- ArcSight Threat Intelligence - unrated - Clean
- AutoShun - unrated - Clean
- Bfore.Ai PreCrime - unrated - Clean
- BitDefender - clean - Clean
- Bkav - unrated - Clean
- BlockList - clean - Clean
- Blueliv - clean - Clean
- Certego - clean - Clean
- ChainPatrol - unrated - Clean
- Chong Lua Dao - clean - Clean
- CINS Army - clean - Clean
- CRDF - clean - Clean
- Criminal IP - unrated - Clean
- CSIS Security Group - unrated - Clean
- CTX AI - clean - Clean
- Cyan - unrated - Clean
- Cyble - clean - Clean
- CyRadar - clean - Clean
- desenmascara.me - clean - Clean
- DNS8 - unrated - Clean
- Dr.Web - clean - Clean
- EmergingThreats - clean - Clean
- Emsisoft - clean - Clean
- Ermes - unrated - Clean
- ESET - clean - Clean
- ESTsecurity - clean - Clean
- Forcepoint ThreatSeeker - clean - Clean
- Fortinet - clean - Clean
- Fortra - unrated - Clean
- G-Data - clean - Clean
- GCP Abuse Intelligence - unrated - Clean
- Google Safe Browsing - clean - Clean
- GreenSnow - clean - Clean
- GreyNoise - unrated - Clean
- Gridinsoft - unrated - Clean
- Guardpot - unrated - Clean
- Heimdal Security - clean - Clean
- Hunt.io Intelligence - unrated - Clean
- IPsum - clean - Clean
- Juniper Networks - clean - Clean
- K7AntiVirus - unrated - Clean
- Kaspersky - clean - Clean
- LevelBlue - clean - Clean
- Lionic - clean - Clean
- Lumu - unrated - Clean
- Malwared - clean - Clean
- MalwarePatrol - clean - Clean
- MalwareURL - unrated - Clean
- Mimecast - unrated - Clean
- Netcraft - unrated - Clean
- OpenPhish - clean - Clean
- PhishFort - unrated - Clean
- Phishing Database - clean - Clean
- Phishtank - clean - Clean
- PREBYTES - clean - Clean
- PrecisionSec - unrated - Clean
- Quick Heal - clean - Clean
- Quttera - clean - Clean
- Rising - clean - Clean
- SafeToOpen - unrated - Clean
- Sangfor - clean - Clean
- Sansec eComscan - unrated - Clean
- Scantitan - clean - Clean
- SCUMWARE.org - clean - Clean
- Seclookup - clean - Clean
- Snort IP sample list - unrated - Clean
- SOCRadar - unrated - Clean
- Sophos - clean - Clean
- StopForumSpam - clean - Clean
- Sucuri SiteCheck - clean - Clean
- Synthient - unrated - Clean
- ThreatHive - clean - Clean
- URLhaus - clean - Clean
- URLQuery - clean - Clean
- Viettel Threat Intelligence - clean - Clean
- VIPRE - unrated - Clean
- ViriBack - clean - Clean
- VX Vault - clean - Clean
- Webroot - clean - Clean
- Xcitium Verdict Cloud - unrated - Clean
- Yandex Safebrowsing - clean - Clean
- ZeroCERT - clean - Clean
- ZeroFox - unrated - Clean
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
Delta Android Keysystem Watch tutorial Visit shop
What the captured page showed
3 observations- 01
Delta Android Keysystem
- 02
Watch tutorial
- 03
Visit shop
03 · Investigation Story
Investigation story
What the site claims
Platoboost
What we observed
Saved browser evidence recorded forced redirects, cross domain landing.
What independent research found
1 external finding were saved and compared with the page evidence.
What remains unverified
1 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Aggressive Ads & Malvertising
Service and business model
Content
Observed behavior
Evidence behind this classification
- 01A primary control opened an unrelated external destination on another domain.
- 02The page identifies itself as a “Delta Android Keysystem.”
- 03text Watch tutorial auth.platorelay.com
If this is a scam — what it means for you
Trying to proceed can expose visitors to another domain
When a visitor activates a primary control, the observed result is navigation to an unrelated external destination.
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
The recorded destination is on moonlighthathel.org rather than auth.platorelay.com, placing the visitor outside the target domain.
Avoid using the prominent controls unless you are prepared to leave the site. Close any unexpected destination, and do not download files, grant permissions, or enter personal or payment information there without independently verifying it.
Web research findings
Independent findings for auth.platorelay.com, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
No independently sourced scam reports or credibility records were found for auth.platorelay.com. That is common for new or low-traffic sites and does not clear the site.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainauth.platorelay.com
- Redirects toauth.platorelay.com
- Hosted byCloudflare, Inc.
- Referencesstatic.cloudflareinsights.com
Domain Timeline
- Jun 23, 2024Domain registered
First appeared in WHOIS records — 2.3 years old when this review was saved.
- Sep 26, 2026Saved security review — Flagged as suspicious
The completed checks from this saved scan are detailed above.
auth.platorelay.com is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No direct contact email found on the captured page.
Domain & Encryption
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
Additional evidence review · Additional evidence review
Operator / customer risk
unknownComplaints, withdrawals, business conduct and commercial traps.
Additional evidence review · Additional evidence review
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 0 of 92 engines flagged | Completed | No adverse finding | fresh · Sep 26, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | Not available |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | Not available |
| Visual evidence | 3 visible observations saved with the page capture | Completed | No adverse finding | Not available |
| Independent research | 1 independent finding were saved | Completed | No adverse finding | Not available |
- Antivirus
- Result0 of 92 engines flagged
- CompletionCompleted
- FindingNo adverse finding
- Freshnessfresh · Sep 26, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- FreshnessNot available
- Visual evidence
- Result3 visible observations saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Independent research
- Result1 independent finding were saved
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is auth.platorelay.com a scam or is it safe?
Is auth.platorelay.com safe to use?
Has auth.platorelay.com been flagged by antivirus engines?
Is auth.platorelay.com on any phishing or malware blacklists?
How old is the auth.platorelay.com domain?
Does auth.platorelay.com have a valid SSL certificate?
Where is auth.platorelay.com hosted?
How often is the auth.platorelay.com report updated?
08 · Final Verdict
Final verdict
Platoboost uses a keysystem-style page with a disruptive cross-domain redirect
The page presents a “Delta Android Keysystem” with “Watch tutorial” and “Visit shop” controls, while a primary control was observed opening an unrelated external domain. Although saved reputation checks found no current threat warning or malicious detections for the target, the redirect behavior creates meaningful visitor risk and supports a Moderate Risk score.
09 · Community