
Is bodelen.com safe?
http://bodelen.com/
Coveragepartial2 of 4 applicable core capabilities
Bodelen.com is a high-risk advertising redirect domain
The captured page resembles a sparse directory, but independent research identifies bodelen.com as an ad rotator used to display dubious content or redirect visitors to untrustworthy sites. Thirteen antivirus families also recorded adverse results. A current browser-screening check found no warning, but that does not outweigh the domain-specific redirect findings and broader detections.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
The captured page resembles a sparse directory, but independent research identifies bodelen.com as an ad rotator used to display dubious content or redirect visitors to untrustworthy sites. Thirteen antivirus families also recorded adverse results. A current browser-screening check found no warning, but that does not outweigh the domain-specific redirect findings and broader detections.
Strong evidence of an unsafe advertising operation
Published security research says bodelen.com was blocked because it operates as an ad rotator involved in fraud. Separate research describes its purpose as displaying dubious content or redirecting visitors to other untrustworthy sites.
Saved scanning evidence records adverse results from 13 antivirus families. Although the observation is stale and should not establish present behavior by itself, it materially reinforces the domain-specific research.
A clean browser check does not establish safety
The fresh browser-screening check returned no threat warning, but the saved TLS check did not validate the connection. Neither result counters the evidence that the domain has been used for dubious advertising redirects.
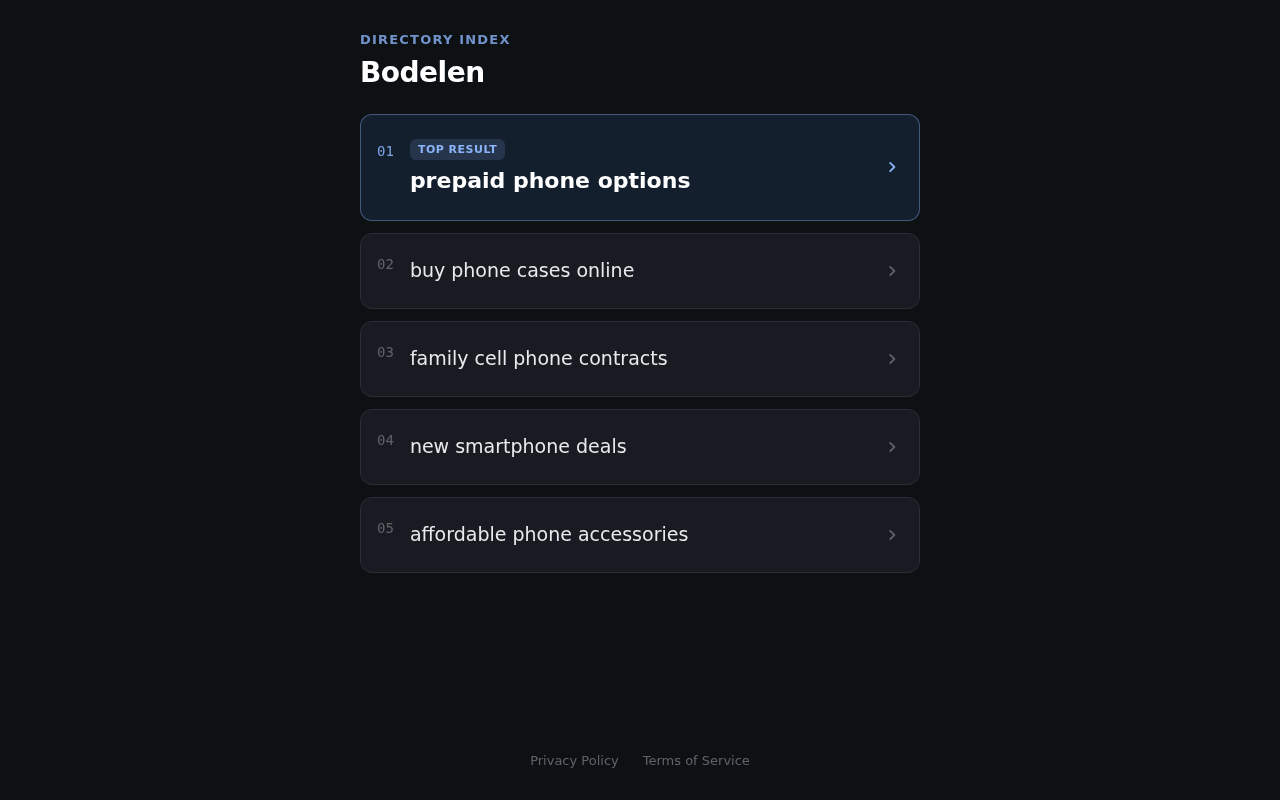
The captured page showed “DIRECTORY INDEX Bodelen” and a “prepaid phone options” link, while no direct contact email was found. These observations provide little reassurance about who operates the page or where its links lead.
Why the score is 24
13 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
16/ 92
detectionsSaved result - stale
16 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 14
- Suspicious
- 2
- Total
- 92
| Engine | Finding |
|---|---|
| ADMINUSLabsMalicious | malicious |
| alphaMountain.aiMalicious | malicious |
| Bfore.Ai PreCrimeMalicious | malicious |
| CyRadarMalicious | malicious |
| Dr.WebMalicious | malicious |
| ESETMalicious | malware |
| FortinetMalicious | malware |
| KasperskyMalicious | phishing |
| LionicMalicious | malicious |
| RisingMalicious | malicious |
| SafeToOpenMalicious | malicious |
| SophosMalicious | malware |
| VIPREMalicious | malware |
| WebrootMalicious | malicious |
| Forcepoint ThreatSeekerSuspicious | suspicious |
| GridinsoftSuspicious | suspicious |
All 92 engine results
- ADMINUSLabs - malicious - Malicious
- alphaMountain.ai - malicious - Malicious
- Bfore.Ai PreCrime - malicious - Malicious
- CyRadar - malicious - Malicious
- Dr.Web - malicious - Malicious
- ESET - malware - Malicious
- Fortinet - malware - Malicious
- Kaspersky - phishing - Malicious
- Lionic - malicious - Malicious
- Rising - malicious - Malicious
- SafeToOpen - malicious - Malicious
- Sophos - malware - Malicious
- VIPRE - malware - Malicious
- Webroot - malicious - Malicious
- Forcepoint ThreatSeeker - suspicious - Suspicious
- Gridinsoft - suspicious - Suspicious
- 0xSI_f33d - unrated - Clean
- Abusix - clean - Clean
- Acronis - clean - Clean
- AILabs (MONITORAPP) - clean - Clean
- AlienVault - clean - Clean
- AlphaSOC - unrated - Clean
- Antiy-AVL - clean - Clean
- ArcSight Threat Intelligence - unrated - Clean
- AutoShun - unrated - Clean
- BitDefender - clean - Clean
- Bkav - unrated - Clean
- BlockList - clean - Clean
- Blueliv - clean - Clean
- Certego - clean - Clean
- ChainPatrol - unrated - Clean
- Chong Lua Dao - clean - Clean
- CINS Army - clean - Clean
- CRDF - clean - Clean
- Criminal IP - unrated - Clean
- CSIS Security Group - unrated - Clean
- CTX AI - clean - Clean
- Cyan - unrated - Clean
- Cyble - clean - Clean
- desenmascara.me - clean - Clean
- DNS8 - unrated - Clean
- EmergingThreats - clean - Clean
- Emsisoft - clean - Clean
- Ermes - unrated - Clean
- ESTsecurity - clean - Clean
- Fortra - unrated - Clean
- G-Data - clean - Clean
- GCP Abuse Intelligence - unrated - Clean
- Google Safe Browsing - clean - Clean
- GreenSnow - clean - Clean
- GreyNoise - unrated - Clean
- Guardpot - unrated - Clean
- Heimdal Security - clean - Clean
- Hunt.io Intelligence - unrated - Clean
- IPsum - clean - Clean
- Juniper Networks - clean - Clean
- K7AntiVirus - unrated - Clean
- LevelBlue - clean - Clean
- Lumu - unrated - Clean
- Malwared - clean - Clean
- MalwarePatrol - clean - Clean
- MalwareURL - unrated - Clean
- Mimecast - unrated - Clean
- Netcraft - unrated - Clean
- OpenPhish - clean - Clean
- PhishFort - unrated - Clean
- Phishing Database - clean - Clean
- Phishtank - clean - Clean
- PREBYTES - clean - Clean
- PrecisionSec - unrated - Clean
- Quick Heal - clean - Clean
- Quttera - clean - Clean
- Sangfor - clean - Clean
- Sansec eComscan - unrated - Clean
- Scantitan - clean - Clean
- SCUMWARE.org - clean - Clean
- Seclookup - clean - Clean
- Snort IP sample list - unrated - Clean
- SOCRadar - unrated - Clean
- StopForumSpam - clean - Clean
- Sucuri SiteCheck - clean - Clean
- Synthient - unrated - Clean
- ThreatHive - clean - Clean
- URLhaus - clean - Clean
- URLQuery - unrated - Clean
- Viettel Threat Intelligence - clean - Clean
- ViriBack - clean - Clean
- VX Vault - clean - Clean
- Xcitium Verdict Cloud - unrated - Clean
- Yandex Safebrowsing - clean - Clean
- ZeroCERT - clean - Clean
- ZeroFox - unrated - Clean
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
DIRECTORY INDEX Bodelen prepaid phone options
What the captured page showed
2 observations- 01
DIRECTORY INDEX Bodelen
- 02
prepaid phone options
03 · Investigation Story
Investigation story
What the site claims
Loading...
What we observed
Saved browser evidence recorded forced redirects, cross domain landing.
What independent research found
2 external findings were saved and compared with the page evidence.
What remains unverified
2 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Aggressive Ads & Malvertising
Service and business model
Content
Observed behavior
Evidence behind this classification
- 0113 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- 02Domain-specific research identifies bodelen.com as an ad rotator involved in fraud.
- 03Research says the domain displays dubious content or redirects visitors to other untrustworthy sites.
If this is a scam — what it means for you
Following the directory links can lead away from Bodelen
A visitor is presented with a directory-style page containing links such as “prepaid phone options”; research on this exact domain says its purpose includes redirecting visitors to other untrustworthy sites.
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
Because those destinations may display dubious content, proceeding through the directory creates exposure to third-party pages that should not be trusted with downloads, permissions, credentials, or payment details.
Avoid interacting with bodelen.com or following its directory links. If it opens unexpectedly, close the page without granting permissions or downloading anything, and check the browser and device for unwanted extensions or software.
Web research findings
Independent findings for bodelen.com, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainbodelen.com
- Redirects toww547.bodelen.com
- Hosted byLeaseWeb USA, Inc. New York
Domain Timeline
- Dec 1, 2025Domain registered
First appeared in WHOIS records — 10 months old when this review was saved.
- Oct 6, 2026Saved security review — Flagged as suspicious
The completed checks from this saved scan are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No direct contact email found on the captured page.
Domain & Encryption
Redirect Chain
- 1302http://bodelen.com/
- 2200http://ww547.bodelen.com/
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
Additional evidence review · Additional evidence review
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
Additional evidence review · Additional evidence review
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 16 of 92 engines flagged | Limited | Adverse | stale fallback · Oct 6, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | Not available |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | Not available |
| Visual evidence | 2 visible observations saved with the page capture | Completed | No adverse finding | Not available |
| Independent research | 2 independent findings were saved | Completed | Adverse | Not available |
- Antivirus
- Result16 of 92 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · Oct 6, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- FreshnessNot available
- Visual evidence
- Result2 visible observations saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Independent research
- Result2 independent findings were saved
- CompletionCompleted
- FindingAdverse
- FreshnessNot available
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is bodelen.com a scam or a legit site?
Is bodelen.com safe to use?
What is the risk from the ads and redirects on bodelen.com?
Why does bodelen.com open unrelated pages or pop-ups?
How do I stop the pop-ups or notifications from bodelen.com?
Has bodelen.com been flagged by antivirus engines?
Is bodelen.com on any phishing or malware blacklists?
How old is the bodelen.com domain?
Does bodelen.com have a valid SSL certificate?
Where is bodelen.com hosted?
How often is the bodelen.com report updated?
08 · Final Verdict
Final verdict
Bodelen.com is a high-risk advertising redirect domain
The captured page resembles a sparse directory, but independent research identifies bodelen.com as an ad rotator used to display dubious content or redirect visitors to untrustworthy sites. Thirteen antivirus families also recorded adverse results. A current browser-screening check found no warning, but that does not outweigh the domain-specific redirect findings and broader detections.
09 · Community