

Is discord-api.domiyoung.com safe?
http://discord-api.domiyoung.com/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (59 of 93 engines answered): completed
- Google Safe Browsing: completed
- page reading · not available: did not fully complete
- page capture · limited: did not fully complete
- domain records: completed
- web research: completed
Discord-impersonating subdomain flagged as phishing by seven antivirus engines and multiple threat feeds
discord-api.domiyoung.com is a subdomain that impersonates Discord's API infrastructure. Seven independent antivirus engines and three threat-intelligence feeds (OpenPhish, PhishPin, PhishTank) identify it as a phishing site. The site's own pages could not be reviewed because it returned HTTP 403 to every request, so the exact credential-harvesting flow was not observed, but the external evidence is decisive. This is a dangerous phishing host, not a legitimate service.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 8/100
Dangerous covers scores 1–20. 5 findings pulled the score down; 2 pushed it up.
What pulled the score down
- Decisive7 independent antivirus families reported an adverse result.
- Moderate3 independent sources carry complaints or warnings about this site, including: "discord-api.domiyoung.com,OpenPhish: discord-api.domiyoung.com,website,high,0,2026-11-03T00:15:02.630Z,2026-11-03T00:15:02.630Z"
- Moderate3 independent sources carry complaints or warnings about this site, including: "discord-api[.]domiyoung[.]com | subdomain trick | 2 feeds | 2"
- Moderate3 independent sources carry complaints or warnings about this site, including: "https://discord-api.domiyoung.com/ added on Nov 2nd 2026 10:49 PM | by zzxcvapppp | Unknown | ONLINE"
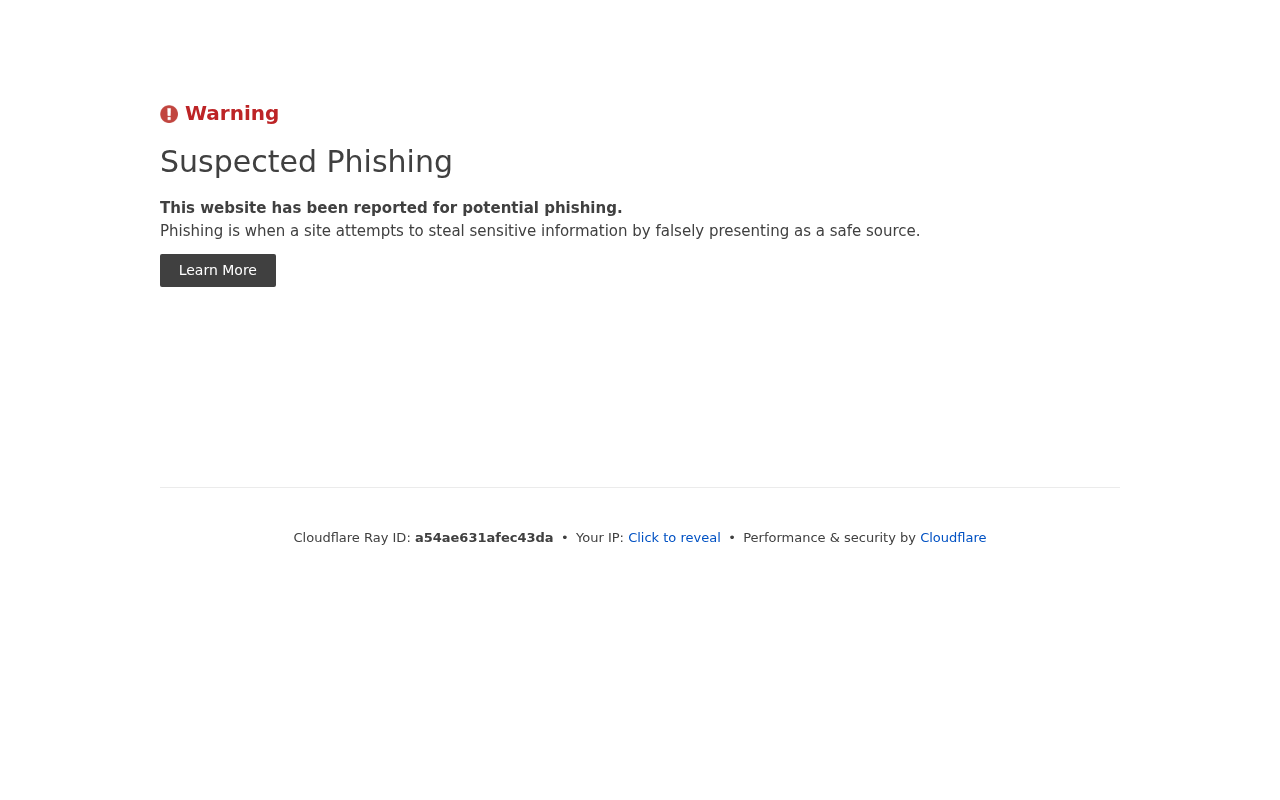
- ModerateWarning Suspected Phishing This website has been reported for potential phishing.
What pushed the score up
- SupportsThe browser threat feed returned no threat warning for this host.
- SupportsThe registrable domain is 558 days old (domiyoung.com, the parent domain of this subdomain host; it does not show how long the subdomain itself has existed)
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor). Community reviews never change the Safety Score.
Lost money or shared details on discord-api.domiyoung.com? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on discord-api.domiyoung.com, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Report the domain to its registrar
Alibaba Cloud Computing Ltd. d/b/a HiChina (www.net.cn) takes abuse reports at domainabuse@service.aliyun.com (+86.95187). Include the address and what happened.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 · Investigation Brief
Investigation Brief
discord-api.domiyoung.com is a subdomain that impersonates Discord's API infrastructure. Seven independent antivirus engines and three threat-intelligence feeds (OpenPhish, PhishPin, PhishTank) identify it as a phishing site. The site's own pages could not be reviewed because it returned HTTP 403 to every request, so the exact credential-harvesting flow was not observed, but the external evidence is decisive. This is a dangerous phishing host, not a legitimate service.
Multiple independent sources identify this host as phishing
Seven antivirus engines, including Emsisoft, ESET, Fortinet and Kaspersky, returned malicious or suspicious verdicts for this host, with one additional engine marking it suspicious. That is a decisive technical signal that the site is being used for phishing.
Independent threat-intelligence feeds corroborate the antivirus findings. OpenPhish lists the domain as a high-severity phishing site, PhishPin records it as a subdomain trick with two feeds, and PhishTank shows it was submitted as an online phishing URL. These are external reports about this specific host, not generic warnings.
Technical checks are mixed, but the operator risk is severe
The browser threat feed returned no warning and a valid TLS certificate exists for the host, but the scanned address was served over plain HTTP with no redirect to HTTPS, so any connection to it is unencrypted. These technical details do not outweigh the phishing verdicts from multiple security vendors.
The site's own pages could not be reviewed because it returned HTTP 403 to every request, so the exact phishing mechanism was not observed. The parent domain is 558 days old, but that does not make this subdomain legitimate; the subdomain itself may be newer and is the host being flagged.
Why the score is 8
7 independent antivirus families reported an adverse result. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
8/ 93
detectionsFresh result
8 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 7
- Suspicious
- 1
- Total
- 93
| Engine | Finding |
|---|---|
| EmsisoftMalicious | phishing |
| ESETMalicious | phishing |
| FortinetMalicious | phishing |
| KasperskyMalicious | phishing |
| NetcraftMalicious | malicious |
| OpenPhishMalicious | phishing |
| WebrootMalicious | malicious |
| DNS8Suspicious | suspicious |
All 93 engine results
- Emsisoft - phishing - Malicious
- ESET - phishing - Malicious
- Fortinet - phishing - Malicious
- Kaspersky - phishing - Malicious
- Netcraft - Malicious
- OpenPhish - phishing - Malicious
- Webroot - Malicious
- DNS8 - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Unrated
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- Dr.Web - Clean
- EmergingThreats - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- WebrootPhishing and Other Frauds
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual warning signs were identified
Warning Suspected Phishing This website has been reported for potential phishing.
What the captured page showed
1 observation- 01
Warning Suspected Phishing This website has been reported for potential phishing.
03 · Investigation Story
Investigation story
What the site claims
Independent evidence classifies the site as login portal, but the page's own claim could not be captured.
What we observed
The page itself could not be fully inspected, so the report relies on the other saved checks.
What independent research found
3 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Login Portal
Observed behavior
Evidence behind this classification
- 01Seven antivirus engines flagged the host as malicious or suspicious, including Emsisoft, ESET, Fortinet and Kaspersky.
- 027 independent antivirus families reported an adverse result.
- 033 independent sources carry complaints or warnings about this site, including: "discord-api.domiyoung.com,OpenPhish: discord-api.domiyoung.com,website,high,0,2026-11-03T00:15:02.630Z,2026-11-03T00:15:02.630Z"
What this means for you
What a visitor would experience
A visitor reaching this host would be interacting with a page that security vendors and threat feeds have identified as a phishing site impersonating Discord. The subdomain name 'discord-api' is designed to look like Discord's own API infrastructure, which is a common trick to make the URL appear trustworthy.
How the observed mechanism works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
A screenshot review shows a warning banner stating 'Suspected Phishing' and 'This website has been reported for potential phishing.' This confirms that the site is being actively flagged to visitors by security tooling.
Do not visit this site. If you have already entered your Discord credentials on this or a similar page, change your Discord password immediately and enable two-factor authentication. Treat any messages or links pointing to discord-api.domiyoung.com as malicious.
Web research findings
Independent findings for discord-api.domiyoung.com, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- GACSopen
"discord-api.domiyoung.com,OpenPhish: discord-api.domiyoung.com,website,high,0,2026-11-03T00:15:02.630Z,2026-11-03T00:15:02.630Z"
- PhishPinopen
"discord-api[.]domiyoung[.]com | subdomain trick | 2 feeds | 2"
- PhishTankopen
"https://discord-api.domiyoung.com/ added on Nov 2nd 2026 10:49 PM | by zzxcvapppp | Unknown | ONLINE"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domaindiscord-api.domiyoung.com
- Redirects todiscord-api.domiyoung.com
- Hosted byCloudflare, Inc.
Domain Timeline
- Apr 23, 2025Domain registered
First appeared in WHOIS records — 1.5 years old when this review was saved.
- Nov 3, 2026Saved security review — Rated Dangerous
The completed checks from this saved scan are detailed above.
Domain & Encryption
Cloudflare DNS is used by legitimate and scam sites alike, so it does not identify who runs the site.
Report this domain to its registrar: send the address and what happened to this contact.
Certificate issued for domiyoung.com.
A shared Cloudflare address answers for many sites, so it is not the site's own server and says nothing about who runs it.
Redirect Chain
The site refused our redirect check, so this chain may be incomplete.
- 1403http://discord-api.domiyoung.com/
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentunavailable
- Analysiscomplete
- Visual evidencepartial
The conclusion is supported by the evidence saved with this report.
Technical threat
maliciousMalware, phishing, credential theft and hostile infrastructure.
7 independent antivirus families reported an adverse result. · Warning Suspected Phishing This website has been reported for potential phishing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
3 independent sources carry complaints or warnings about this site, including: "discord-api.domiyoung.com,OpenPhish: discord-api.domiyoung.com,website,high,0,2026-11-03T00:15:02.630Z,2026-11-03T00:15:02.630Z" · 3 independent sources carry complaints or warnings about this site, including: "discord-api[.]domiyoung[.]com | subdomain trick | 2 feeds | 2"
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 8 of 93 engines flagged | Completed | Adverse | fresh · analysed Nov 3, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 3, 2026 |
| Page content | Page content was not available for semantic review | Unavailable | No saved finding | Not available |
| Visual evidence | The site showed a challenge page instead of its content; 1 visible observation saved | Limited | Adverse | this scan · Nov 3, 2026 |
| Independent research | 3 independent findings were saved | Completed | Adverse | this scan · Nov 3, 2026 |
- Antivirus
- Result8 of 93 engines flagged
- CompletionCompletedFindingAdverse
- Freshnessfresh · analysed Nov 3, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 3, 2026
- Page content
- ResultPage content was not available for semantic review
- CompletionUnavailableFindingNo saved finding
- FreshnessNot available
- Visual evidence
- ResultThe site showed a challenge page instead of its content; 1 visible observation saved
- CompletionLimitedFindingAdverse
- Freshnessthis scan · Nov 3, 2026
- Independent research
- Result3 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 3, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is discord-api.domiyoung.com a scam or a legit website?
Is discord-api.domiyoung.com safe to use?
I already paid or entered my details on discord-api.domiyoung.com — what should I do?
Can I get my money back from discord-api.domiyoung.com?
Did discord-api.domiyoung.com steal my password or personal information?
How do I report discord-api.domiyoung.com?
discord-api.domiyoung.com looks professional — how can it still be a scam?
Has discord-api.domiyoung.com been flagged by antivirus engines?
Is discord-api.domiyoung.com on any phishing or malware blacklists?
How old is the discord-api.domiyoung.com domain?
Where is discord-api.domiyoung.com hosted?
How often is the discord-api.domiyoung.com report updated?
08 · Final Verdict
Final verdict
Discord-impersonating subdomain flagged as phishing by seven antivirus engines and multiple threat feeds
discord-api.domiyoung.com is a subdomain that impersonates Discord's API infrastructure. Seven independent antivirus engines and three threat-intelligence feeds (OpenPhish, PhishPin, PhishTank) identify it as a phishing site. The site's own pages could not be reviewed because it returned HTTP 403 to every request, so the exact credential-harvesting flow was not observed, but the external evidence is decisive. This is a dangerous phishing host, not a legitimate service.
09 · Community
Community
Are you the owner of discord-api.domiyoung.com?Verify and reply