
Is dk-brobizzweb.wasmer.app safe?
http://dk-brobizzweb.wasmer.app/
Coveragepartial2 of 4 applicable core capabilities
Transient Wasmer subdomain impersonating Denmark's Brobizz toll service auto-redirects visitors through an external PHP gate
dk-brobizzweb.wasmer.app is a throwaway subdomain on the Wasmer hosting platform that borrows the name of Brobizz, the legitimate Danish toll and road-pricing service. When the page loads, the browser is automatically sent off-domain to a PHP gate at dkapp-production.up.railway.app/gate.php and then on to Google. Independent research links the Brobizz name to a separate Wasmer-hosted PHP page, consistent with a campaign that uses free, disposable hosting to stand up brand-impersonation pages. The site's own contact and policy text was never read, so nothing on the page itself vouches for the operator. A clean Safe Browsing result and a valid TLS certificate only mean no detection was recorded at scan time; they do not make an impersonation redirect safe. The combination of brand impersonation, transient third-party hosting, and an automatic cross-domain handoff to an external script places this in the Dangerous band.
Be the first to review dk-brobizzweb.wasmer.app
Lost money to dk-brobizzweb.wasmer.app? Warn others
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
dk-brobizzweb.wasmer.app is a throwaway subdomain on the Wasmer hosting platform that borrows the name of Brobizz, the legitimate Danish toll and road-pricing service. When the page loads, the browser is automatically sent off-domain to a PHP gate at dkapp-production.up.railway.app/gate.php and then on to Google. Independent research links the Brobizz name to a separate Wasmer-hosted PHP page, consistent with a campaign that uses free, disposable hosting to stand up brand-impersonation pages. The site's own contact and policy text was never read, so nothing on the page itself vouches for the operator. A clean Safe Browsing result and a valid TLS certificate only mean no detection was recorded at scan time; they do not make an impersonation redirect safe. The combination of brand impersonation, transient third-party hosting, and an automatic cross-domain handoff to an external script places this in the Dangerous band.
Brand impersonation with an automatic off-domain handoff
The hostname dk-brobizzweb.wasmer.app is built to look like a Brobizz-branded web property, but it sits on Wasmer, a free application-hosting platform, not on Brobizz's own infrastructure. Independent research surfaced a related Wasmer-hosted PHP page using the Brobizz name, which is consistent with a pattern of disposable brand-impersonation pages rather than an official service.
On load, the page automatically sent the browser to an unrelated external site: first to dkapp-production.up.railway.app/gate.php, a PHP gate hosted on a separate free platform, and then on to Google. That cross-domain handoff to an external script is the core mechanism here — the visitor never sees a legitimate Brobizz page, and any interaction happens on infrastructure the operator controls only transiently.
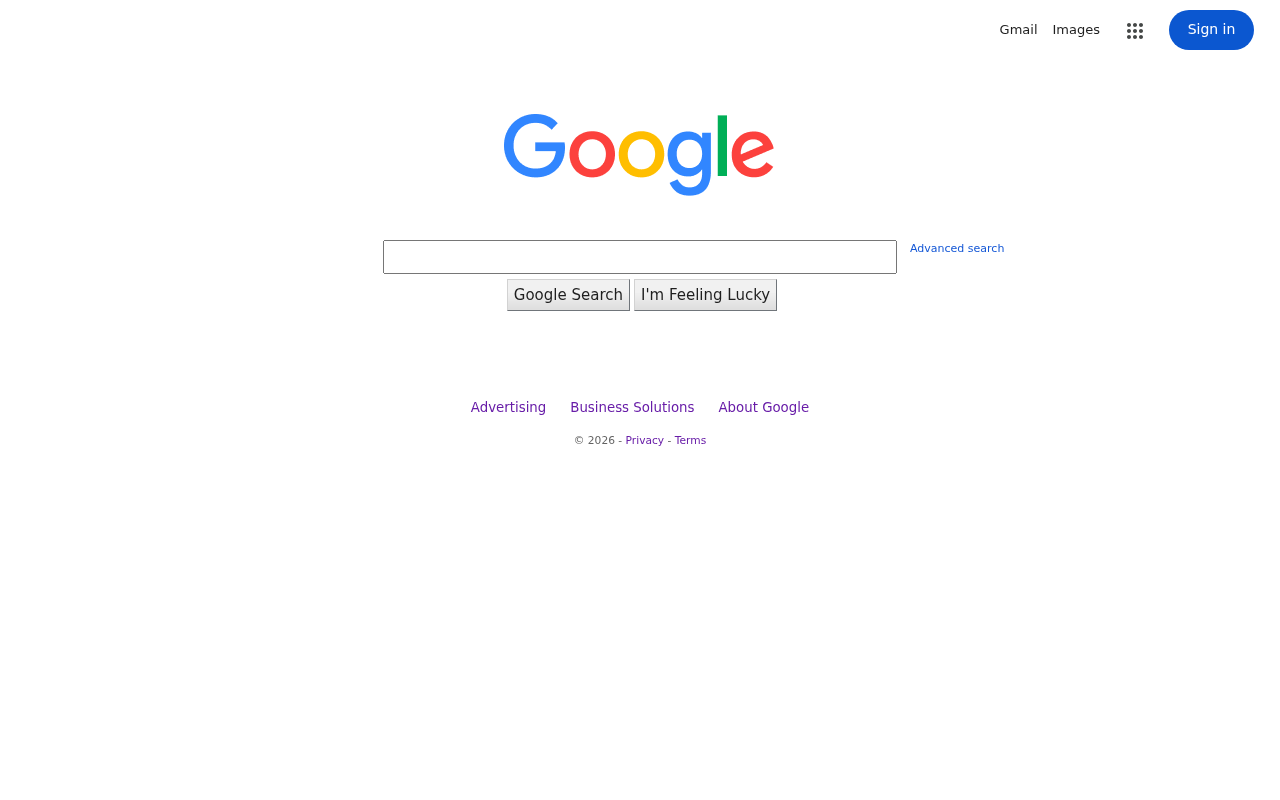
The browser render confirms the final visible page was the Google homepage, meaning the Brobizz-branded page itself was never a destination the visitor could inspect or verify.
Clean technical checks do not offset operator risk
The browser threat feed returned no threat warning and the saved TLS check found a valid encrypted connection. These are absence-of-detection signals, not evidence of legitimacy: a freshly stood-up phishing page on free hosting will often pass both until it is reported.
The hosting IP carries an abuse confidence score of 2/100 across 27 saved reports, which is low and therefore neutral context rather than a mitigating factor. The site's own contact details were not reviewed because the page text was not read in full, so there is no operator disclosure, registration, or policy text on the page to weigh in the site's favour.
Why the score is 18
The page automatically sent the browser to an unrelated external site. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
The browser rendered the Google homepage after the initial redirects.
What the captured page showed
1 observation- 01
The browser rendered the Google homepage after the initial redirects.
03 · Investigation Story
Investigation story
What the site claims
The captured page appears to offer a login portal service.
What we observed
Saved browser evidence recorded forced redirects.
What independent research found
1 external finding was saved and compared with the page evidence.
What remains unverified
2 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Login Portal
Observed behavior
Evidence behind this classification
- 01The page automatically sent the browser to an unrelated external site.
- 02The hostname dk-brobizzweb.wasmer.app impersonates Brobizz, a legitimate Danish toll service, while being hosted on the free Wasmer platform rather than Brobizz infrastructure.
- 03The hosting IP has an abuse confidence score of 2/100 across 27 saved reports, which is low and does not by itself indicate abuse.
What this means for you
What a visitor actually experiences
A visitor who opens dk-brobizzweb.wasmer.app expecting a Brobizz page is immediately redirected off the domain to dkapp-production.up.railway.app/gate.php, an external PHP script, before the browser finally lands on Google.
How the observed mechanism works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
Because the visible end state is the Google homepage, the visitor never reaches a genuine Brobizz login or information page. Any credentials or personal details entered during that redirect chain would be submitted to infrastructure controlled by the redirect operator, not to Brobizz.
Do not enter any Brobizz credentials, payment details, or personal information on dk-brobizzweb.wasmer.app or on the dkapp-production.up.railway.app/gate.php page it redirects to. If you need Brobizz, navigate directly to the official brobizz.com site by typing the address yourself. If you already entered login details through this redirect chain, change your Brobizz password immediately and contact Brobizz support through their official channels.
Web research findings
Independent findings for dk-brobizzweb.wasmer.app, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- urlquery.netopen
"dk-brobizz-php-42e42.wasmer.app Rank unknown | loads from | login.brobizz.com"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domaindk-brobizzweb.wasmer.app
- Redirects todk-brobizzweb.wasmer.app
- Hosted byHetzner Online GmbH
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Redirect Chain
- 1308http://dk-brobizzweb.wasmer.app/
- 2206https://dk-brobizzweb.wasmer.app/
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antivirusunavailable
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
unknownMalware, phishing, credential theft and hostile infrastructure.
The site's own contact details were not reviewed because the page text was not read in full, so no operator disclosure or policy text could be assessed. · browser-render The browser rendered the Google homepage after the initial redirects. Google www.google.com
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
The page automatically sent the browser to an unrelated external site. · The hostname dk-brobizzweb.wasmer.app impersonates Brobizz, a legitimate Danish toll service, while being hosted on the free Wasmer platform rather than Brobizz infrastructure.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | No usable engine result was saved | Unavailable | No saved finding | Not available |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 22, 2026 |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | this scan · Oct 22, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 22, 2026 |
| Independent research | 1 independent finding was saved | Completed | No adverse finding | this scan · Oct 22, 2026 |
- Antivirus
- ResultNo usable engine result was saved
- CompletionUnavailable
- FindingNo saved finding
- FreshnessNot available
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 22, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- Freshnessthis scan · Oct 22, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 22, 2026
- Independent research
- Result1 independent finding was saved
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 22, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is dk-brobizzweb.wasmer.app a scam or a legit website?
Is dk-brobizzweb.wasmer.app safe to use?
What should I do if I already gave my details to dk-brobizzweb.wasmer.app?
Can I get my money back from dk-brobizzweb.wasmer.app?
Did dk-brobizzweb.wasmer.app steal my password or personal information?
How do I report dk-brobizzweb.wasmer.app?
Why does dk-brobizzweb.wasmer.app look legitimate if it's a scam?
Is dk-brobizzweb.wasmer.app on any phishing or malware blacklists?
How old is the dk-brobizzweb.wasmer.app domain?
Where is dk-brobizzweb.wasmer.app hosted?
How often is the dk-brobizzweb.wasmer.app report updated?
08 · Final Verdict
Final verdict
Transient Wasmer subdomain impersonating Denmark's Brobizz toll service auto-redirects visitors through an external PHP gate
dk-brobizzweb.wasmer.app is a throwaway subdomain on the Wasmer hosting platform that borrows the name of Brobizz, the legitimate Danish toll and road-pricing service. When the page loads, the browser is automatically sent off-domain to a PHP gate at dkapp-production.up.railway.app/gate.php and then on to Google. Independent research links the Brobizz name to a separate Wasmer-hosted PHP page, consistent with a campaign that uses free, disposable hosting to stand up brand-impersonation pages. The site's own contact and policy text was never read, so nothing on the page itself vouches for the operator. A clean Safe Browsing result and a valid TLS certificate only mean no detection was recorded at scan time; they do not make an impersonation redirect safe. The combination of brand impersonation, transient third-party hosting, and an automatic cross-domain handoff to an external script places this in the Dangerous band.
09 · Community