
Is dzarena.
http://dzarena.com/
dzarena.com is flagged as phishing or malware by 10 security engines
dzarena.com returned 10 malicious and 1 suspicious verdicts from 93 antivirus engines, including phishing labels from BitDefender and G-Data and malware labels from Fortinet and Sophos. The page itself shows only a green 'DZArena' logo and a 'Home' heading, and the site's own pages could not be reviewed because the fetch timed out. The domain has existed since April 2023 and the browser threat feed shows no warning, which keeps the score from the Dangerous band, but the number of adverse engine verdicts puts it at High Risk.
At a glance
Saved with this scan, at the time of the check (Nov 20, 2026); each value is explained in the sections below.
Domain age
3 years old
Registered Apr 15, 2023Expires Apr 15, 2027Certificate
Valid
Expires Feb 3, 2027 (74 days after the check)Hosting
United States (US)
Cloudflare, Inc.Popularity
Not in the Cloudflare Radar top list
Antivirus
11/93 flagged
11 antivirus engines flagged this URLSafe Browsing
Not flagged
Not flagged on major threat listsCommunity
No ratings yet
Checked
Nov 20, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 22/100
High Risk covers scores 21–44. 3 findings pulled the score down; 2 pushed it up.
What pulled the score down
- Decisive9 independent antivirus families reported an adverse result. VirusTotal re-checked the URL on November 20, 2026; its earlier analysis from October 30, 2026 had 11 engines flag it.
- Moderate2 independent sources carry complaints or warnings about this site, including: "Sitio web sospechoso Gridinsoft clasifica actualmente este sitio como Sitio web sospechoso."
- Moderate2 independent sources carry complaints or warnings about this site, including: "This website has been reported as unsafe by Maltiverse"
What pushed the score up
- SupportsThe domain is about 3 years 7 months old, which is older than typical throwaway phishing domains.
- SupportsThe browser threat feed shows no warning and the TLS certificate is valid.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
Lost money or shared details on dzarena.com? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on dzarena.com, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Report the domain to its registrar
Cloudflare, Inc. takes abuse reports at registrar-abuse@cloudflare.com (+1.6503198930). Include the address and what happened.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 / 09
Investigation brief
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (61 of 93 engines answered): completed
- Google Safe Browsing: completed
- page reading · not available
- page capture: completed
- domain records: completed
- web research: completed
dzarena.com returned 10 malicious and 1 suspicious verdicts from 93 antivirus engines, including phishing labels from BitDefender and G-Data and malware labels from Fortinet and Sophos. The page itself shows only a green 'DZArena' logo and a 'Home' heading, and the site's own pages could not be reviewed because the fetch timed out. The domain has existed since April 2023 and the browser threat feed shows no warning, which keeps the score from the Dangerous band, but the number of adverse engine verdicts puts it at High Risk.
What the security engines found
The multi-engine malware scan reports 10 malicious and 1 suspicious detections across 93 engines. Nine independent antivirus families reported an adverse result, and the multi-engine malware scan re-checked the URL on November 20, 2026, after an earlier analysis from October 30, 2026 also flagged it, so the detections are current and have persisted.
Outside the antivirus engines, Gridinsoft rates the site as suspicious with a trust score of 1 out of 100, and an independent site-rating service notes that Maltiverse reported it as unsafe. These are third-party listings, not proof of what the page does, but they point the same way as the engine verdicts.
The browser threat feed shows no warning and the TLS certificate is valid. Those clean results mean no browser-level block at scan time, not that the site is safe.
What could and could not be verified about the site
The site's own pages could not be reviewed: the fetch timed out on both HTTP and HTTPS. The rendered screenshot shows a green 'DZArena' logo, a 'Home' heading and a single 'Home' link on an otherwise blank page, with no products, prices, forms, contact details or policies. No payload or credential-harvesting behavior was directly observed, and the site's purpose is unknown.
The domain is about 3 years 7 months old, and the hosting IP has an abuse score of 0 out of 100 with no saved reports. Registrant details are redacted, with a registrant state of Djelfa listed in WHOIS data. No operator disclosure was found on the site.
Ages and dates in this analysis are at the time of the check (Nov 20, 2026).
Why the score is 22
02 / 09
Security evidence
Antivirus engines
11/ 93
flaggedFresh result
11 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 10
- Suspicious
- 1
- Total
- 93
- Malicious10
- Suspicious1
- Clean50
- Undetected32
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | malicious |
| BitDefenderMalicious | phishing |
| CRDFMalicious | malicious |
| FortinetMalicious | malware |
| G-DataMalicious | phishing |
| LionicMalicious | malicious |
| NetcraftMalicious | malicious |
| RisingMalicious | malicious |
| SOCRadarMalicious | malicious |
| SophosMalicious | malware |
| GridinsoftSuspicious | suspicious |
All 93 engine results
- alphaMountain.ai - Malicious
- BitDefender - phishing - Malicious
- CRDF - Malicious
- Fortinet - malware - Malicious
- G-Data - phishing - Malicious
- Lionic - Malicious
- Netcraft - Malicious
- Rising - Malicious
- SOCRadar - Malicious
- Sophos - malware - Malicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Clean
- Fortra - Unrated
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Unrated
- LevelBlue - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiMalicious
- Sophosspyware and malware
- BitDefenderparked
- Forcepoint ThreatSeekervehicles
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed

Visual context from the captured page
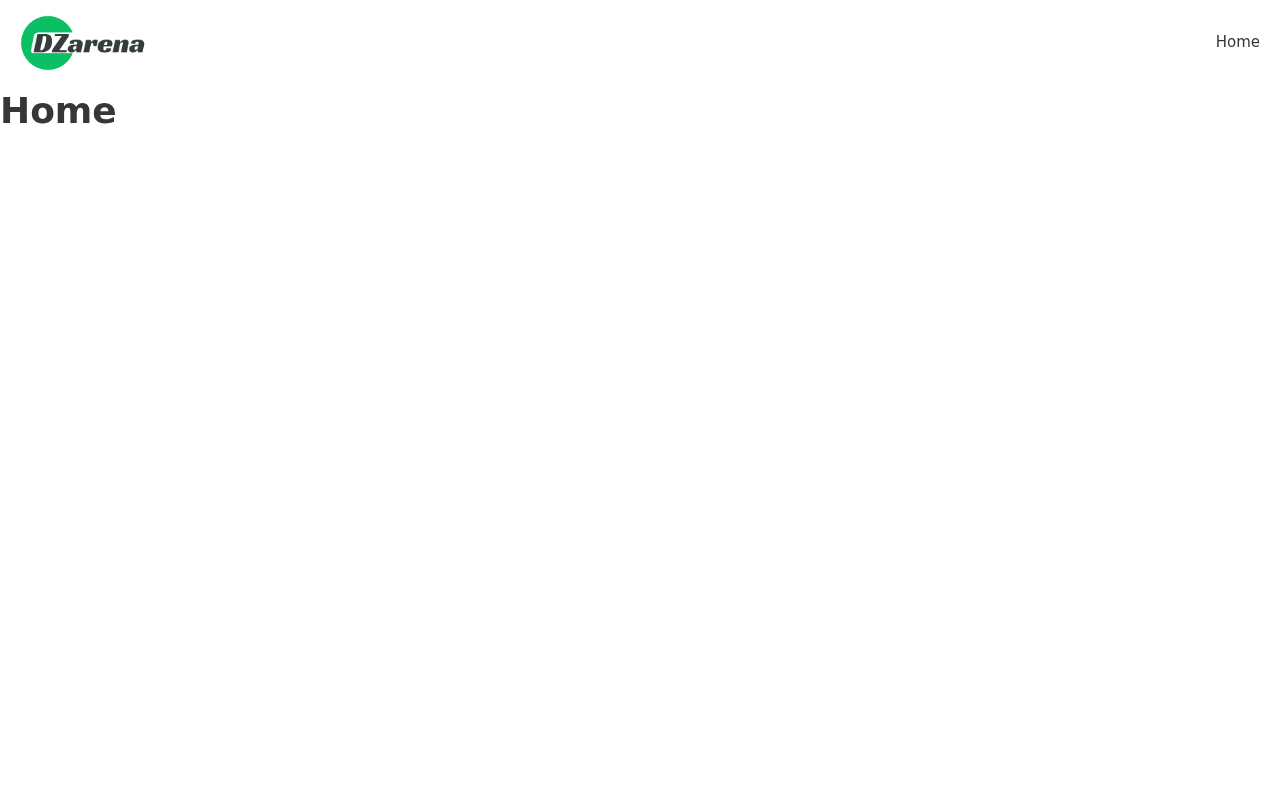
Top-left shows a green circular logo containing the word 'DZArena' in dark italic lettering. A single 'Home' link appears in the top-right navigation bar. A large 'Home' heading is displayed below the logo; the rest of the page is blank white with no products, prices, forms, contact details or policy links visible.
What the captured page showed
3 observations- 01
Top-left shows a green circular logo containing the word 'DZArena' in dark italic lettering.
- 02
A single 'Home' link appears in the top-right navigation bar.
- 03
A large 'Home' heading is displayed below the logo; the rest of the page is blank white with no products, prices, forms, contact details or policy links visible.
Browser behavior
What our isolated browser recorded while it loaded the page. Host names only: no full addresses are published.
- Pop-ups
- 0
- Download attempts
- 0
- Notification prompts
- 0
- Navigations
- 1
- Other hosts contacted
- 3
Where the page went
- First loaddzarena.comSame site
Hosts on our aggressive-advertising list
None contacted.
Test clicks
No test click was made on this page.
03 / 09
Investigation story
What the site claims
No page claim could be verified for dzarena.com because no usable page content or saved capture was available.
What we observed
The page itself could not be fully inspected, so the report relies on the other saved checks.
What independent research found
6 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Unknown
Observed behavior
Evidence behind this classification
Web research findings
Independent findings for dzarena.com, including public complaints, named review sources, registration records, and look-alike-domain evidence.
Reputation sources
04 / 09
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domaindzarena.
com - Redirects towww.
dzarena. com - Hosted byCloudflare, Inc.
Domain timeline
- Apr 15, 2023Domain registered
First appeared in WHOIS records — 3 years old when this review was saved.
- Nov 20, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
dzarena.com is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Domain & encryption
At the scan on Nov 20, 2026: 90% of the registration period had passed
Cloudflare DNS is used by legitimate and scam sites alike, so it does not identify who runs the site.
Report this domain to its registrar: send the address and what happened to this contact.
At the scan on Nov 20, 2026: 17% of the validity period had passed
Certificate issued for dzarena.com.
A shared Cloudflare address answers for many sites, so it is not the site's own server and says nothing about who runs it.
Redirect chain
- 1301http://dzarena.com/
- 2200https://www.dzarena.com/
Server reputation
Referenced domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
Grouped by what each domain is for. in page: named in the page’s HTML. contacted: the browser loaded it while rendering the page. ad list: on our aggressive-advertising list.
Analytics & tracking1
- static.cloudflareinsights.comcontacted
CDN & fonts1
- cdn.jsdelivr.netcontacted
Other / unknown1
- base.gateway.tenderly.cocontacted
05 / 09
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentunavailable
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
maliciousMalware, phishing, credential theft and hostile infrastructure.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 11 of 93 engines flagged | Completed | Adverse | fresh · analysed Nov 20, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 20, 2026 |
| Page content | Page content was not available for semantic review | Unavailable | No saved finding | Not available |
| Visual evidence | 3 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 20, 2026 |
| Independent research | 6 independent findings were saved | Completed | Adverse | this scan · Nov 20, 2026 |
- Antivirus
- Result11 of 93 engines flagged
- CompletionCompletedFindingAdverse
- Freshnessfresh · analysed Nov 20, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 20, 2026
- Page content
- ResultPage content was not available for semantic review
- CompletionUnavailableFindingNo saved finding
- FreshnessNot available
- Visual evidence
- Result3 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 20, 2026
- Independent research
- Result6 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 20, 2026
07 / 09
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is dzarena.com a scam or a legit website?
Is dzarena.com safe to use?
What should I do if I already gave my details to dzarena.com?
Can I get my money back from dzarena.com?
Did dzarena.com steal my password or personal information?
How do I report dzarena.com?
Why does dzarena.com look legitimate if it's a scam?
Has dzarena.com been flagged by antivirus engines?
Is dzarena.com on any phishing or malware blacklists?
How old is the dzarena.com domain?
Does dzarena.com have a valid SSL certificate?
How often is the dzarena.com report updated?
08 / 09
Final verdict
dzarena.com is flagged as phishing or malware by 10 security engines
dzarena.com returned 10 malicious and 1 suspicious verdicts from 93 antivirus engines, including phishing labels from BitDefender and G-Data and malware labels from Fortinet and Sophos. The page itself shows only a green 'DZArena' logo and a 'Home' heading, and the site's own pages could not be reviewed because the fetch timed out. The domain has existed since April 2023 and the browser threat feed shows no warning, which keeps the score from the Dangerous band, but the number of adverse engine verdicts puts it at High Risk.
09 / 09
Community
Are you the owner of dzarena.com?Verify and reply