
Is fitgirlrepacks.site safe?
http://fitgirlrepacks.site/
Coveragestrong4 of 6 applicable core capabilities
fitgirlrepacks.site is a parked typosquat of the official FitGirl Repacks site, historically flagged as malicious and now monetised as a domain-for-sale.
The site at fitgirlrepacks.site is not the real FitGirl Repacks destination. The legitimate project's own guidance points users to a single official domain and explicitly warns about fake and scam sites imitating it (research:v9:1), and this hostname appears in a published fake-domains blocklist (research:v9:2). The page currently resolves to a parking/sale notice reading "text fitgirlrepacks.site may be for sale, click to inquire" (derived:vision-observation:1), so visitors arriving from a misspelled link or search result land on an offer-to-sell page rather than a download portal. Saved antivirus telemetry also records two independent detections against this domain (source:antivirus:aggregate). Because the historical detections are stale and the current surface is a parked sale page, the score lands in the High Risk band rather than Dangerous.
Be the first to review fitgirlrepacks.site
Lost money to fitgirlrepacks.site? Warn others
Did you use fitgirlrepacks.site?
Loading saved screenshot
Preparing the saved page preview.
Follow fitgirlrepacks.site
Get a notification in your MalwareTips bell when new reviews arrive (one digest a day at most), when the verdict changes after a rescan, and when MalwareTips or the verified site owner replies. Unfollow any time.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
The site at fitgirlrepacks.site is not the real FitGirl Repacks destination. The legitimate project's own guidance points users to a single official domain and explicitly warns about fake and scam sites imitating it (research:v9:1), and this hostname appears in a published fake-domains blocklist (research:v9:2). The page currently resolves to a parking/sale notice reading "text fitgirlrepacks.site may be for sale, click to inquire" (derived:vision-observation:1), so visitors arriving from a misspelled link or search result land on an offer-to-sell page rather than a download portal. Saved antivirus telemetry also records two independent detections against this domain (source:antivirus:aggregate). Because the historical detections are stale and the current surface is a parked sale page, the score lands in the High Risk band rather than Dangerous.
A lookalike domain with a hostile track record
fitgirlrepacks.site is a deliberate near-spelling of the FitGirl Repacks brand. The project's recorded guidance names a single official destination for its releases and warns users away from "fake and scam sites" designed to look like it (research:v9:1). This hostname is a different domain, and it appears on a community-maintained list of fake domains targeting that brand (research:v9:2). Visitors who mistype the address or tap a spoofed search result are routed here instead of the genuine portal.
The domain is not new — it has existed for over six years (observed:domain-age) — but age does not wash away what it has been used for. Saved telemetry records adverse results from two independent antivirus families against this domain (source:antivirus:aggregate). Those detections are historical and should be read as evidence of past abuse rather than a live infection at the front door. The browser threat feed currently returns no warning on the host (observed:safe-browsing), which means the brand-impersonation risk here is not currently being surfaced by that layer.
What is actually on the page today
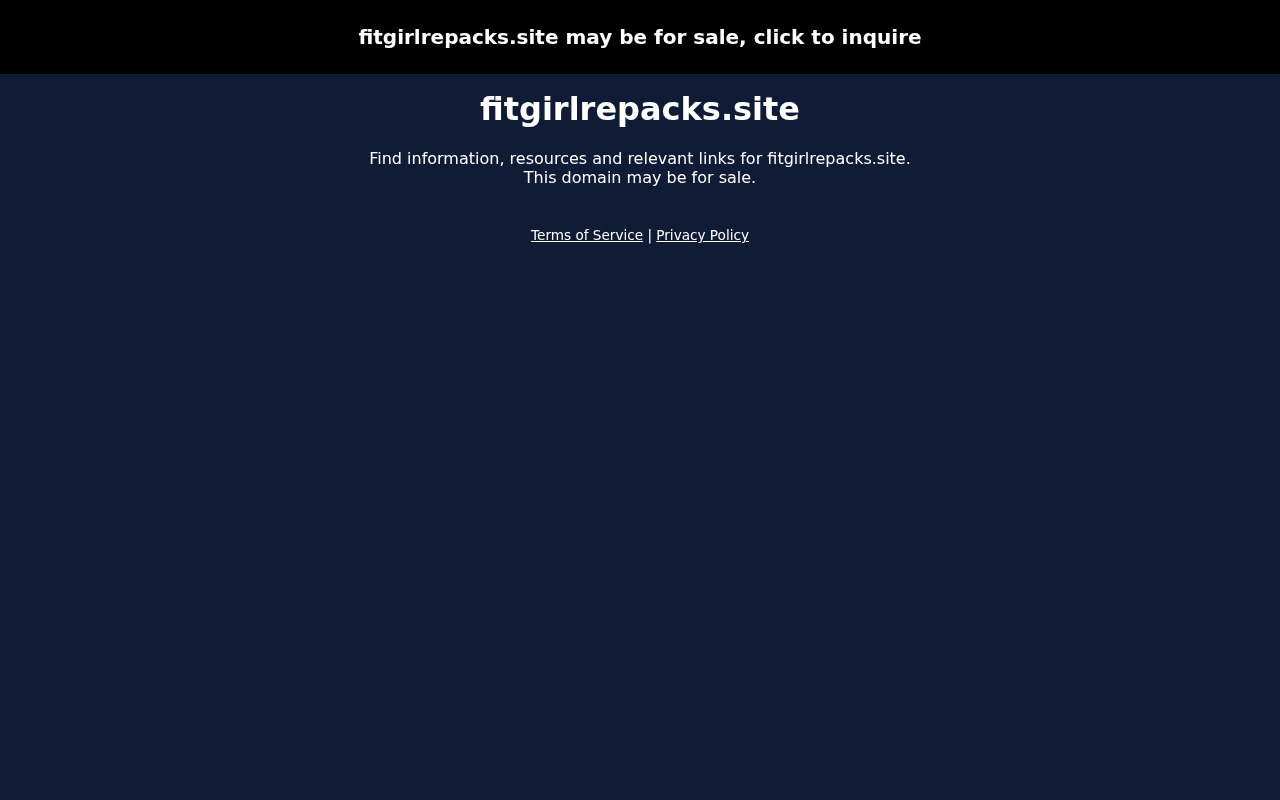
A screenshot review of the live page shows a single piece of commercial copy: "text fitgirlrepacks.site may be for sale, click to inquire" (derived:vision-observation:1). There is no software catalogue, no download button, and no brand content on the surface. That makes the domain's current business model domain brokerage — monetising a typo'd hostname that once carried malicious detections (source:antivirus:aggregate).
Separately, the host serves a valid certificate but the scanned address was plain HTTP with no redirect to HTTPS (observed:tls). A visitor who follows the "click to inquire" prompt or any future link from this domain has no transport-layer protection on that hop. Contact details for the operator were not reviewed (observed:page-content:contacts-not-reviewed), so nothing can be said one way or the other about who ultimately answers an inquiry.
Why the score is 30
2 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
6/ 92
detectionsSaved analysis from October 2, 2026 - stale
6 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 3
- Suspicious
- 3
- Total
- 92
| Engine | Finding |
|---|---|
| ADMINUSLabsMalicious | malicious |
| Chong Lua DaoMalicious | malicious |
| FortinetMalicious | malware |
| alphaMountain.aiSuspicious | suspicious |
| GridinsoftSuspicious | suspicious |
| URLQuerySuspicious | suspicious |
All 92 engine results
- ADMINUSLabs - Malicious
- Chong Lua Dao - Malicious
- Fortinet - malware - Malicious
- alphaMountain.ai - Suspicious
- Gridinsoft - Suspicious
- URLQuery - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Unrated
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Unrated
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
fitgirlrepacks.site may be for sale, click to inquire
What the captured page showed
1 observation- 01
fitgirlrepacks.site may be for sale, click to inquire
03 · Investigation Story
Investigation story
What the site claims
The captured page did not expose a clear title or service claim.
What we observed
The page content was captured and checked alongside 58 antivirus results.
What independent research found
2 external findings were saved and compared with the page evidence.
What remains unverified
2 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Fake Shop & Commercial Deception
Service and business model
Unknown
Observed behavior
Evidence behind this classification
- 012 independent sources carry complaints or warnings about this site, including: "The ONLY official site for FitGirl Repacks. Every single FG repack installer has a link inside, which leads here. Do not fall for fake and scam sites,"
- 022 independent sources carry complaints or warnings about this site, including: "fitgirlrepack.site"
- 032 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
If this is a scam — what it means for you
The visitor path from misspelled link to parked page
A visitor who intends to reach the real FitGirl Repacks project follows a typo or spoofed link to fitgirlrepacks.site (research:v9:2) and instead of a release index sees a single sale notice inviting them to click through to inquire about buying the domain (derived:vision-observation:1). The project's own guidance warns in advance that lookalike domains of this kind are fertile ground for fake and scam operators (research:v9:1).
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
The navigation happens over plain HTTP with no HTTPS redirect (observed:tls), so any content served on this hop — including whatever sits behind the "click to inquire" link — is delivered without transport encryption. Combined with the domain's history of adverse antivirus results (source:antivirus:aggregate), the safe course is to treat any future hosted content here as untrusted regardless of its branding.
Do not use fitgirlrepacks.site. Bookmark the project's stated official destination instead of typing the name into a search bar, because this domain is a spelling variant that the project itself lists as a fake-site risk (research:v9:1, research:v9:2). If you arrive here, close the tab rather than following the "click to inquire" solicitation (derived:vision-observation:1), and never enter credentials or payment details on a page served over plain HTTP (observed:tls). Installers obtained from a lookalike host should be treated as potentially tampered given this domain's history of adverse detections (source:antivirus:aggregate).
Web research findings
Independent findings for fitgirlrepacks.site, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainfitgirlrepacks.site
- Redirects tofitgirlrepacks.site
- Hosted byConfluence Networks Inc
- Referencesl.cdn-fileserver.com
Domain Timeline
- Apr 26, 2020Domain registered
First appeared in WHOIS records — 6 years old when this review was saved.
- Oct 26, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
fitgirlrepacks.site is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
2 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
2 independent sources carry complaints or warnings about this site, including: "The ONLY official site for FitGirl Repacks. Every single FG repack installer has a link inside, which leads here. Do not fall for fake and scam sites," · 2 independent sources carry complaints or warnings about this site, including: "fitgirlrepack.site"
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 6 of 92 engines flagged | Limited | Adverse | stale fallback · analysed Oct 2, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 26, 2026 |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | this scan · Oct 26, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 26, 2026 |
| Independent research | 2 independent findings were saved | Completed | Adverse | this scan · Oct 26, 2026 |
- Antivirus
- Result6 of 92 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · analysed Oct 2, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 26, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- Freshnessthis scan · Oct 26, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 26, 2026
- Independent research
- Result2 independent findings were saved
- CompletionCompleted
- FindingAdverse
- Freshnessthis scan · Oct 26, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is fitgirlrepacks.site a scam or a legit online store?
Is fitgirlrepacks.site safe to use?
I already paid or entered my details on fitgirlrepacks.site — what should I do?
Can I get my money back from fitgirlrepacks.site?
I ordered from fitgirlrepacks.site but nothing arrived — is it a fake shop?
How do I report fitgirlrepacks.site?
fitgirlrepacks.site looks professional — how can it still be a scam?
Has fitgirlrepacks.site been flagged by antivirus engines?
Is fitgirlrepacks.site on any phishing or malware blacklists?
How old is the fitgirlrepacks.site domain?
Does fitgirlrepacks.site have a valid SSL certificate?
How often is the fitgirlrepacks.site report updated?
08 · Final Verdict
Final verdict
fitgirlrepacks.site is a parked typosquat of the official FitGirl Repacks site, historically flagged as malicious and now monetised as a domain-for-sale.
The site at fitgirlrepacks.site is not the real FitGirl Repacks destination. The legitimate project's own guidance points users to a single official domain and explicitly warns about fake and scam sites imitating it (research:v9:1), and this hostname appears in a published fake-domains blocklist (research:v9:2). The page currently resolves to a parking/sale notice reading "text fitgirlrepacks.site may be for sale, click to inquire" (derived:vision-observation:1), so visitors arriving from a misspelled link or search result land on an offer-to-sell page rather than a download portal. Saved antivirus telemetry also records two independent detections against this domain (source:antivirus:aggregate). Because the historical detections are stale and the current surface is a parked sale page, the score lands in the High Risk band rather than Dangerous.
09 · Community
Community
Are you the owner of fitgirlrepacks.site?Verify and reply