

Is hif.to safe?
http://hif.to/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (60 of 93 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
Link shortener hif.to runs a working short-link and QR service, but one antivirus family labels the domain phishing and the operator publishes no company identity.
hif.to is a link-shortening and marketing tool: the homepage offers a box to paste a long URL with optional custom alias and password, and the site advertises QR codes, analytics and pixels. The domain is about seven years old, the encrypted connection is valid and the browser threat feed shows no warning, but a saved antivirus observation records a Kaspersky phishing verdict and a Gridinsoft suspicious verdict, and the site names no company, address, phone or email — only a web form. That mix of a real, long-lived service with an unresolved phishing label and an anonymous operator puts it in the moderate-risk band rather than the safe one.
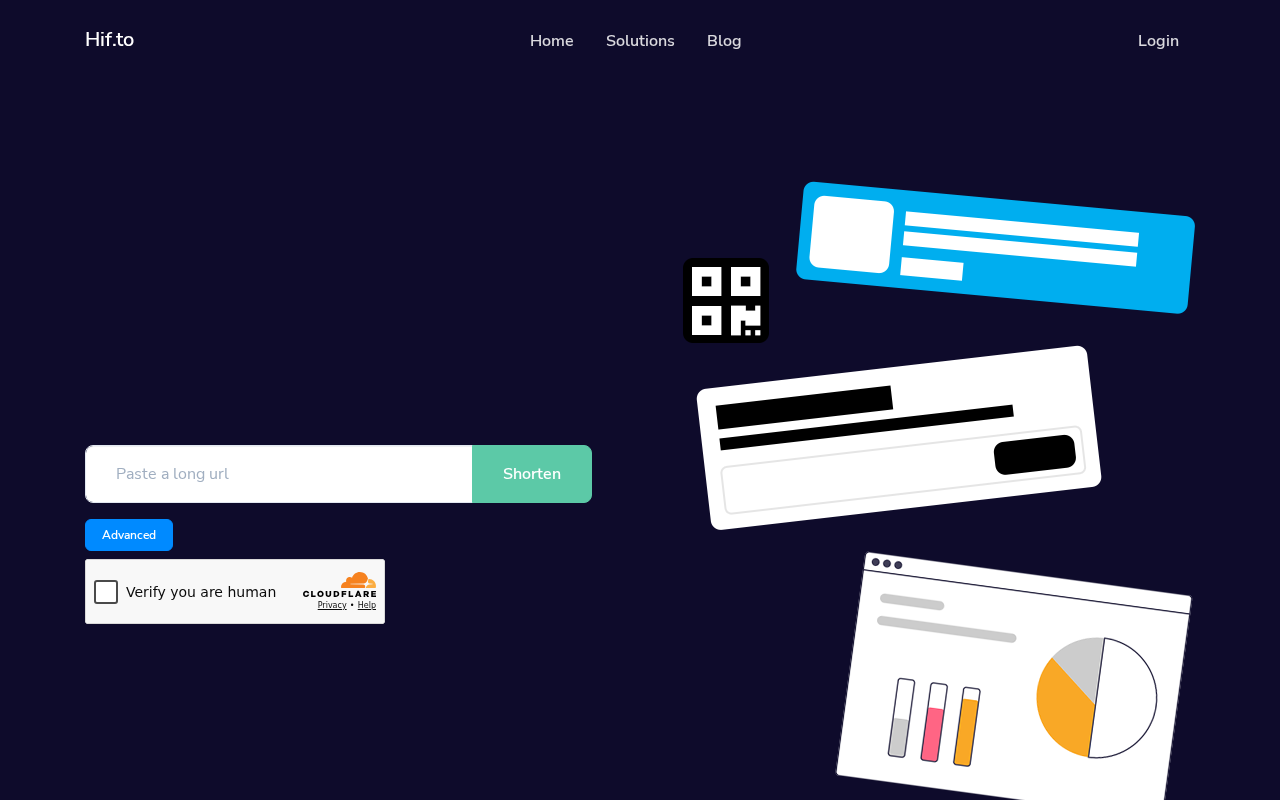 Saved site captureCaptured safely during this scan2 antivirus engines flagged this URLKaspersky, GridinsoftSaved antivirus result from Oct 24, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 62/100
Moderate Risk covers scores 45–69. 2 findings pulled the score down; 3 pushed it up.
What pulled the score down
- Strong1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.-2 pts
- ModerateNo company name, registration, address, phone or direct email is published; contact is only a web form.-1 pts
What pushed the score up
- SupportsThe registrable domain is about seven years old, registered in December 2019.
- SupportsThe saved TLS check found a valid encrypted connection.
- SupportsThe browser threat feed returned no threat warning for the site.
Points come from the saved evidence ledger: it lowered the score from 65 to 62 and split those 3 points between the findings that show points; the others carry no points in the ledger.
01 · Investigation Brief
Investigation Brief
hif.to is a link-shortening and marketing tool: the homepage offers a box to paste a long URL with optional custom alias and password, and the site advertises QR codes, analytics and pixels. The domain is about seven years old, the encrypted connection is valid and the browser threat feed shows no warning, but a saved antivirus observation records a Kaspersky phishing verdict and a Gridinsoft suspicious verdict, and the site names no company, address, phone or email — only a web form. That mix of a real, long-lived service with an unresolved phishing label and an anonymous operator puts it in the moderate-risk band rather than the safe one.
A short-link and QR-code tool with a same-site sign-up and contact flow
The homepage pitches short links as a marketing medium for collecting data about customers and their behaviour, and the same page promotes dynamic QR codes with statistics for campaigns. The main action is the 'Shorten' form, which takes a long URL plus an optional custom alias and password, with an 'Advanced' panel for more options.
Account and contact routes stay on the same host: 'Login' leads to the site's own login page, and 'Contact Us' leads to a form that asks for a name, email and message. No cross-domain checkout, payment page or affiliate destination appeared in the captured link graph, and the only third-party element seen was a Cloudflare human-verification widget below the shorten form.
Clean browser checks, an unresolved phishing verdict, and an unnamed operator
The technical picture is mixed. The browser threat feed returned no threat warning, the saved TLS check found a valid encrypted connection, and the hosting IP carries an abuse confidence score of 0 across no saved reports. Against that, a saved antivirus observation records one adverse family — Kaspersky with a phishing verdict — alongside a Gridinsoft suspicious verdict, and that observation is stale, so its timing relative to the current site is not confirmed.
The operator side is weaker than the technical side. The captured pages disclose no company name, registration number, postal address, phone number or direct email; the only route to the operator is the on-site contact form. For a service that handles other people's links and collects analytics on their visitors, that leaves no named party accountable for link abuse, data handling or billing questions.
The domain itself is not new — it was registered in December 2019 and is roughly seven years old — which argues against a throwaway operation. Independent web research returned nothing usable for this scan, so the operator's public reputation remains unverified rather than confirmed clean.
Why the score is 62
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
02 · Security Evidence
Security evidence
Antivirus Engines
2/ 93
detectionsSaved analysis from October 24, 2026 - stale
2 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 1
- Suspicious
- 1
- Total
- 93
| Engine | Finding |
|---|---|
| KasperskyMalicious | phishing |
| GridinsoftSuspicious | suspicious |
All 93 engine results
- Kaspersky - phishing - Malicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Clean
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiInformation Technology
- BitDefendermisc
- Forcepoint ThreatSeekerweb hosting
- Googletechnology
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Visual context from the captured page
Dark navy landing page with 'Hif.to' wordmark top-left and nav items Home, Solutions, Blog, Login top-right. White input field with placeholder 'Paste a long url' and a green 'Shorten' button, with a blue 'Advanced' button beneath. Cloudflare 'Verify you are human' checkbox widget with Privacy and Help links displayed below the shorten form. Decorative illustrations of a QR code, a link card, a browser window and a pie-chart analytics dashboard.
What the captured page showed
4 observations- 01
Dark navy landing page with 'Hif.to' wordmark top-left and nav items Home, Solutions, Blog, Login top-right.
- 02
White input field with placeholder 'Paste a long url' and a green 'Shorten' button, with a blue 'Advanced' button beneath.
- 03
Cloudflare 'Verify you are human' checkbox widget with Privacy and Help links displayed below the shorten form.
- 04
Decorative illustrations of a QR code, a link card, a browser window and a pie-chart analytics dashboard.
What the page says about itself
Quoted from the pages we read: the site's own words, not our findings.
- Page title
Hif.to
Pages we read
- Main page/Read
- Contact page/contactRead
03 · Investigation Story
Investigation story
What the site claims
Hif.to
What we observed
The page content was captured and checked alongside 60 antivirus results.
What independent research found
The search completed without a material external warning or corroborating report.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
No threat category confirmed
Service and business model
Saas
Observed behavior
Evidence behind this classification
- 011 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- 02No company name, registration, address, phone or direct email is published; contact is only a web form.
- 03The registrable domain is about seven years old, registered in December 2019.
If this is a scam — what it means for you
What a visitor actually does here, and where the exposure sits
A visitor pastes a destination URL into the shorten form, optionally sets a custom alias and a password, and receives a short link. Nothing in the captured pages asks for payment details, and no download or notification prompt was observed, so the direct exposure at that step is limited to the link and password being handled by an unnamed operator.
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
The larger exposure is on the receiving end. Short links hide their destination, and the saved antivirus observation carries a phishing verdict against this domain, so a hif.to link arriving in a message should be treated as an unknown destination until it is expanded and checked.
You can use hif.to to shorten a link if you accept that an unnamed operator handles it, but do not put a password on a link you care about and do not reuse credentials on the login page. Treat any hif.to short link you receive from someone else as an unknown destination: expand it first and check where it really goes before clicking through, especially if the message pressures you to log in or pay.
Web research findings
Independent findings for hif.to, including public complaints, named review sources, registration records, and look-alike-domain evidence.
No independently sourced scam reports or credibility records were found for hif.to. That is common for new or low-traffic sites and does not clear the site.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domainhif.to
- Redirects tohif.to
- Hosted by3NT Solutions LLP
- Referenceschallenges.cloudflare.com
Domain Timeline
- Dec 21, 2019Domain registered
First appeared in WHOIS records — 6 years old when this review was saved.
- Nov 4, 2026Saved security review — Rated Moderate Risk
The evidence in this saved scan is mixed or incomplete; the completed checks are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No direct contact email found on the captured page.
Domain & Encryption
Certificate issued for hif.to.
Security checks
- Cloudflare Turnstile
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://hif.to/
- 2200https://hif.to/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
No company name, registration, address, phone or direct email is published; contact is only a web form.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 2 of 93 engines flagged | Limited | Adverse | stale fallback · analysed Oct 24, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Visual evidence | 4 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Independent research | The search completed without a material external finding | Completed | No adverse finding | this scan · Nov 4, 2026 |
- Antivirus
- Result2 of 93 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Oct 24, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Visual evidence
- Result4 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Independent research
- ResultThe search completed without a material external finding
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is hif.to a scam or is it safe?
Is hif.to safe to use?
Has hif.to been flagged by antivirus engines?
Is hif.to on any phishing or malware blacklists?
How old is the hif.to domain?
Does hif.to have a valid SSL certificate?
Where is hif.to hosted?
How often is the hif.to report updated?
08 · Final Verdict
Final verdict
Link shortener hif.to runs a working short-link and QR service, but one antivirus family labels the domain phishing and the operator publishes no company identity.
hif.to is a link-shortening and marketing tool: the homepage offers a box to paste a long URL with optional custom alias and password, and the site advertises QR codes, analytics and pixels. The domain is about seven years old, the encrypted connection is valid and the browser threat feed shows no warning, but a saved antivirus observation records a Kaspersky phishing verdict and a Gridinsoft suspicious verdict, and the site names no company, address, phone or email — only a web form. That mix of a real, long-lived service with an unresolved phishing label and an anonymous operator puts it in the moderate-risk band rather than the safe one.
09 · Community
Community
Are you the owner of hif.to?Verify and reply