

Is howitwent.app safe?
http://howitwent.app/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (58 of 93 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
A young but openly operated trip-film app: named Austrian seller, Paddle-handled payments, no malicious detections
howitwent.app is the website for How It Went, an app that turns GPS tracks, photos and clips into short trip films for iPhone, iPad, Mac and Android. The site names its seller in full — CodeUX.design e.U., Herbert Poul, a street address in Vienna, Austria, and company register number FN 518636a — and routes website purchases through Paddle.com as Merchant of Record, with Apple and Google handling in-app purchases. Nothing malicious was found: no Safe Browsing warning, a valid encrypted connection, and a hosting IP with no abuse reports. The score sits in the low-risk band rather than higher because the domain is only 85 days old, one saved antivirus engine labelled it suspicious purely on newness, and independent reviews of the app were not found.
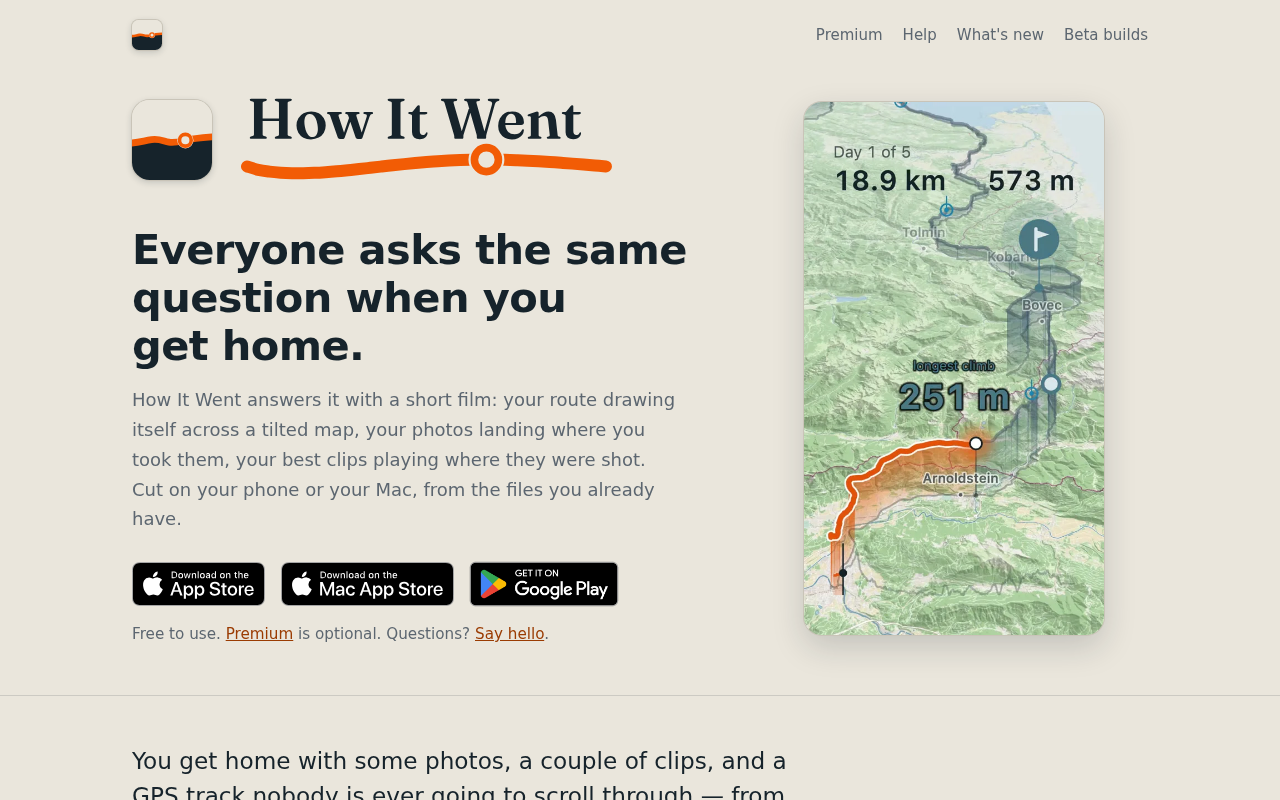 Saved site captureCaptured safely during this scan1 antivirus engine flagged this URLalphaMountain.aiSaved antivirus result from Oct 25, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 82/100
Low Risk covers scores 70–84. 2 findings pulled the score down; 6 pushed it up.
What pulled the score down
- Moderate1 antivirus result marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- MinorThe registrable domain is only 85 days old, so there is no operating history to check against.
What pushed the score up
- SupportsThe terms name the seller as CodeUX.design e.U., Herbert Poul, with a Vienna street address, company register FN 518636a and an imprint link.
- SupportsSafe Browsing returned no warning, TLS is valid, and the hosting IP has an abuse score of 0/100 across zero reports.
- SupportsWebsite orders run through Paddle.com as Merchant of Record, which handles customer service and returns, with refunds and the 14-day EU withdrawal right routed through Paddle's refund policy.
- SupportsIndependent research found a Product Hunt launch post and a TestFlight listing, but no independent reviews or complaint records for the app.
- SupportsThe app is distributed through the App Store, Mac App Store and Google Play, and has a public TestFlight beta listing.
- SupportsThe rendered page shows no card fields, price table, countdown timer or popup, and no notification prompt or download attempt was observed.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
01 · Investigation Brief
Investigation Brief
howitwent.app is the website for How It Went, an app that turns GPS tracks, photos and clips into short trip films for iPhone, iPad, Mac and Android. The site names its seller in full — CodeUX.design e.U., Herbert Poul, a street address in Vienna, Austria, and company register number FN 518636a — and routes website purchases through Paddle.com as Merchant of Record, with Apple and Google handling in-app purchases. Nothing malicious was found: no Safe Browsing warning, a valid encrypted connection, and a hosting IP with no abuse reports. The score sits in the low-risk band rather than higher because the domain is only 85 days old, one saved antivirus engine labelled it suspicious purely on newness, and independent reviews of the app were not found.
Who runs the site and how money moves
The terms page identifies the business behind the app: CodeUX.design e.U., Herbert Poul, Wenhartgasse 23/3/6, 1210 Vienna, Austria, with company register FN 518636a and a link to a full imprint. That is a specific, checkable identity rather than an anonymous storefront, and it matches the first-person launch post written by 'Herbert' and the TestFlight beta listing for the same app.
Premium is optional and the core app is free. Website orders are processed by Paddle.com as online reseller and Merchant of Record, which the site says handles customer service and returns; refunds, including the 14-day EU/EEA/UK/Swiss withdrawal right, go through Paddle's refund policy and the link in the receipt email. Purchases made inside the app are sold by Apple or Google under their own terms.
The yearly plan is recurring billing that is disclosed rather than hidden: the terms say deleting the account cancels a yearly plan bought on the website, and Paddle's receipt and renewal emails link to where the plan can be managed or cancelled. The outbound links on the site go to Paddle's buyer terms and refund policy, Apple's report-a-problem page, and map attribution to OpenStreetMap and Mapterhorn — functional and legal destinations, not affiliate funnels.
Technical checks came back clean, with one age-based caveat
The browser threat feed returned no threat warning, the saved TLS check found a valid encrypted connection, and the hosting IP carries an abuse confidence score of 0/100 across zero saved reports. The rendered page shows no card fields, countdown timer, popup, notification prompt or download attempt — just store badges, a product screenshot and a newsletter form.
The one adverse technical mark is a saved antivirus observation in which a single engine labelled the URL suspicious. That verdict tracks the domain's newness — the registrable domain is 85 days old — rather than any demonstrated behaviour, and the saved analysis is stale. It is a reason to stay measured, not evidence of malware.
The newsletter form asks only for an email address, uses a confirmation link before adding anyone to the list, and every email carries an unsubscribe link; the privacy policy states where data is kept. No credential-harvesting behaviour was observed anywhere on the site.
What is still unverified
The domain is 85 days old, so there is no long operating history behind the app. Independent research surfaced a Product Hunt launch post and a TestFlight beta listing for the same product, but no independent reviews or complaint records that would corroborate a track record either way.
The checkout page itself was not captured, so how clearly the yearly Premium price and renewal terms are shown at the point of payment could not be confirmed. The 'Say hello' contact link's destination was also not captured.
Why the score is 82
The saved checks found no material threat, but the evidence was not strong enough for the highest Safe tier.
02 · Security Evidence
Security evidence
Antivirus Engines
1/ 93
detectionsSaved analysis from October 25, 2026 - stale
1 engine flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 0
- Suspicious
- 1
- Total
- 93
| Engine | Finding |
|---|---|
| alphaMountain.aiSuspicious | suspicious |
All 93 engine results
- alphaMountain.ai - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiSuspicious, Newly Registered
- Googletechnology
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Visual context from the captured page
Header shows an app icon and the wordmark 'How It Went' with an orange route line graphic; top nav reads Premium, Help, What's new, Beta builds. Headline 'Everyone asks the same question when you get home.' with body copy describing a short film built from route, photos and clips, cut on phone or Mac. Three store badges are visible: 'Download on the App Store', 'Download on the Mac App Store', and 'GET IT ON Google Play'. Line under the badges reads 'Free to use. Premium is optional. Questions? Say hello.' with Premium and Say hello as links. Right side shows a phone mockup of a map with a drawn orange route, labels 'Day 1 of 5', '18.9 km', '573 m', 'longest climb 251 m' and place names Tolmin, Kobarid, Bovec, Arnoldstein. No card fields, price table, countdown timer or popup is visible on the rendered page; no notification prompt or download attempt was observed.
What the captured page showed
6 observations- 01
Header shows an app icon and the wordmark 'How It Went' with an orange route line graphic; top nav reads Premium, Help, What's new, Beta builds.
- 02
Headline 'Everyone asks the same question when you get home.' with body copy describing a short film built from route, photos and clips, cut on phone or Mac.
- 03
Three store badges are visible: 'Download on the App Store', 'Download on the Mac App Store', and 'GET IT ON Google Play'.
- 04
Line under the badges reads 'Free to use. Premium is optional. Questions? Say hello.' with Premium and Say hello as links.
- 05
Right side shows a phone mockup of a map with a drawn orange route, labels 'Day 1 of 5', '18.9 km', '573 m', 'longest climb 251 m' and place names Tolmin, Kobarid, Bovec, Arnoldstein.
- 06
No card fields, price table, countdown timer or popup is visible on the rendered page; no notification prompt or download attempt was observed.
What the page says about itself
Quoted from the pages we read: the site's own words, not our findings.
- Page title
How It Went — Trip Films
- Meta description
One ride or a whole trip, cut into a short film from the track, photos and clips — on your phone or your Mac.
Pages we read
- Main page/Read
- Terms/terms/Read
- Refund / returns policy/refunds/Read
- Support / FAQ/help/Read
03 · Investigation Story
Investigation story
What the site claims
How It Went — Trip Films
What we observed
The page content was captured and checked alongside 58 antivirus results.
What independent research found
3 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
No threat category confirmed
Service and business model
Saas
Observed behavior
Evidence behind this classification
- 01The terms name the seller as CodeUX.design e.U., Herbert Poul, with a Vienna street address, company register FN 518636a and an imprint link.
- 02Website orders run through Paddle.com as Merchant of Record, which handles customer service and returns, with refunds and the 14-day EU withdrawal right routed through Paddle's refund policy.
- 03The registrable domain is only 85 days old, so there is no operating history to check against.
Web research findings
Independent findings for howitwent.app, including public complaints, named review sources, registration records, and look-alike-domain evidence.
- Product Huntopen
"Hi, I'm Herbert. I ride multi-day bikepacking trips"
- Product Huntopen
"The whole film is free on iPhone, iPad, Mac and Android, from your own files and at every export size."
- TestFlight - Appleopen
"How It Went turns multi-day GPS activities, photos, and video clips into shareable trip films with animated routes and elevation maps."
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domainhowitwent.app
- Redirects tohowitwent.app
- Hosted byHetzner Online GmbH
- Referencesapps.apple.com · play.google.com
Domain Timeline
- Aug 10, 2026Domain registered
First appeared in WHOIS records — 85 days old when this review was saved.
- Nov 4, 2026Saved security review — Rated Low Risk
This saved scan found no material threat, but the evidence was not strong enough for the highest Safe tier.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Cloudflare DNS is used by legitimate and scam sites alike, so it does not identify who runs the site.
A certificate issued weeks or days before the scan on a domain registered recently is common on short-lived sites, though new legitimate sites look the same.
Certificate issued for *.howitwent.app.
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://howitwent.app/
- 2206https://howitwent.app/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
unknownMalware, phishing, credential theft and hostile infrastructure.
1 antivirus result marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
unknownComplaints, withdrawals, business conduct and commercial traps.
The registrable domain is only 85 days old, so there is no operating history to check against.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 1 of 93 engines flagged | Limited | Adverse | stale fallback · analysed Oct 25, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Visual evidence | 6 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 4, 2026 |
| Independent research | 3 independent findings were saved | Completed | No adverse finding | this scan · Nov 4, 2026 |
- Antivirus
- Result1 of 93 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Oct 25, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Visual evidence
- Result6 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
- Independent research
- Result3 independent findings were saved
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 4, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is howitwent.app a scam or is it safe?
Is howitwent.app safe to use?
Has howitwent.app been flagged by antivirus engines?
Is howitwent.app on any phishing or malware blacklists?
How old is the howitwent.app domain?
Does howitwent.app have a valid SSL certificate?
Where is howitwent.app hosted?
How often is the howitwent.app report updated?
08 · Final Verdict
Final verdict
A young but openly operated trip-film app: named Austrian seller, Paddle-handled payments, no malicious detections
howitwent.app is the website for How It Went, an app that turns GPS tracks, photos and clips into short trip films for iPhone, iPad, Mac and Android. The site names its seller in full — CodeUX.design e.U., Herbert Poul, a street address in Vienna, Austria, and company register number FN 518636a — and routes website purchases through Paddle.com as Merchant of Record, with Apple and Google handling in-app purchases. Nothing malicious was found: no Safe Browsing warning, a valid encrypted connection, and a hosting IP with no abuse reports. The score sits in the low-risk band rather than higher because the domain is only 85 days old, one saved antivirus engine labelled it suspicious purely on newness, and independent reviews of the app were not found.
09 · Community
Community
Are you the owner of howitwent.app?Verify and reply