
Is jesauvelasecu.info safe?
http://jesauvelasecu.info/
Coveragecomplete4 of 4 applicable core capabilities
Expired domain with a documented phishing history now sits on a NameSilo parking page
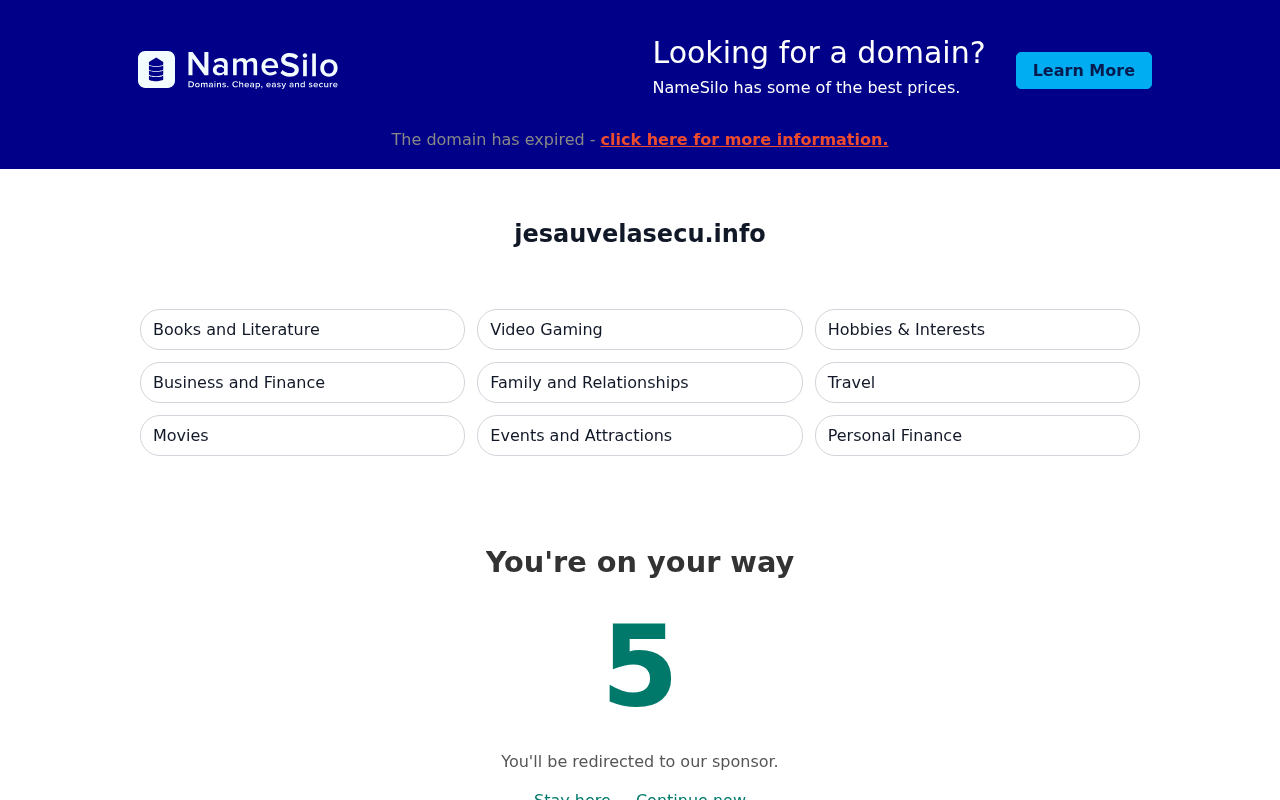
jesauvelasecu.info is not a working website. It currently resolves to a NameSilo parking page that states the domain has expired, and the only interactive element is a generic 'Learn More' link pointing back to the registrar. That alone would be unremarkable, but the domain carries a heavy adverse history: 17 malicious and 3 suspicious detections across 94 engines, 15 independent antivirus families reporting an adverse result, and a threat-feed record tying it to active phishing infrastructure. The domain is roughly a year old, which is consistent with a short-lived phishing campaign that has since lapsed. Because the domain is expired and parked, there is no live credential-harvesting page to interact with right now, but the reputation damage is real and the domain could be re-registered and reactivated at any time. The score reflects that combination: no current live threat surface, but a strongly documented malicious past and no legitimate operator identity behind it.
Be the first to review jesauvelasecu.info
Lost money to jesauvelasecu.info? Warn others
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
jesauvelasecu.info is not a working website. It currently resolves to a NameSilo parking page that states the domain has expired, and the only interactive element is a generic 'Learn More' link pointing back to the registrar. That alone would be unremarkable, but the domain carries a heavy adverse history: 17 malicious and 3 suspicious detections across 94 engines, 15 independent antivirus families reporting an adverse result, and a threat-feed record tying it to active phishing infrastructure. The domain is roughly a year old, which is consistent with a short-lived phishing campaign that has since lapsed. Because the domain is expired and parked, there is no live credential-harvesting page to interact with right now, but the reputation damage is real and the domain could be re-registered and reactivated at any time. The score reflects that combination: no current live threat surface, but a strongly documented malicious past and no legitimate operator identity behind it.
A domain with a documented phishing past
The strongest evidence against this domain is its detection record. A the multi-engine malware scan-style aggregate shows 17 malicious and 3 suspicious detections across 94 engines, and 15 independent antivirus families returned an adverse result. That is not a single false positive; it is a broad, multi-vendor consensus that this host was serving something harmful.
Independent research adds context: the domain appears in a phishing-focused threat feed alongside a registrar reference to NameSilo, LLC. The feed entry is classified as a warning with a customer-report flag, meaning it is adverse external evidence rather than a neutral directory listing. Together with the antivirus consensus, this points to the domain having been used in credential-phishing activity during its active period.
The domain is only 376 days old, which fits the pattern of a short-lived phishing host that was registered, used, and then abandoned. There is no long operating history, no established brand, and no independent reputation to weigh against the adverse detections.
What a visitor actually sees today
The live page is a registrar parking placeholder. Visual review shows the text 'The domain has expired - click here for more information' together with the NameSilo brand and the domain name itself. The page body is essentially a loading placeholder, and the only outbound action is a generic 'Learn More' link to the registrar.
Because the domain is expired and parked, there is no checkout, no login form, and no download on the page right now. The site's own contact and policy pages were not reviewed in full, so nothing can be said about what the operator would disclose if the domain were reactivated. The absence of a live threat surface today is the main reason the score is not lower.
The browser threat feed returned no current threat warning, and the saved TLS check did not validate the connection. These are neutral-to-mildly-supportive signals about the parked state, but they do not erase the historical detection record and they do not establish that the domain is safe to trust.
Why the score lands in the Dangerous band
The scoring here weighs two dimensions. Technically, the current page is inert: it is a parking placeholder with no scripts of concern observed and no active malicious behavior. Operationally, the picture is much worse. A domain with 17 malicious detections, 15 adverse antivirus families, and a phishing threat-feed entry has a demonstrated history of being used to harm visitors, and there is no legitimate operator identity, no company registration, and no independent reputation to offset that.
Expired domains with this kind of history are frequently re-registered and reactivated for new campaigns, sometimes within days. A visitor who bookmarked or was sent this URL has no way to know whether the next time they load it they will get a parking page or a fresh phishing kit. That uncertainty, combined with the documented past, is why the score sits in the Dangerous range rather than being treated as a harmless dead link.
Why the score is 18
15 independent antivirus families reported an adverse result. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
20/ 94
detectionsFresh result
20 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 17
- Suspicious
- 3
- Total
- 94
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | phishing |
| BitDefenderMalicious | phishing |
| CRDFMalicious | malicious |
| CyRadarMalicious | phishing |
| EmsisoftMalicious | malware |
| Forcepoint ThreatSeekerMalicious | phishing |
| FortinetMalicious | phishing |
| G-DataMalicious | phishing |
| KasperskyMalicious | phishing |
| LionicMalicious | phishing |
| RisingMalicious | phishing |
| SafeToOpenMalicious | phishing |
| SeclookupMalicious | malicious |
| SOCRadarMalicious | phishing |
| SophosMalicious | phishing |
| VIPREMalicious | phishing |
| WebrootMalicious | malicious |
| DNS8Suspicious | suspicious |
| ESETSuspicious | suspicious |
| GridinsoftSuspicious | suspicious |
All 94 engine results
- alphaMountain.ai - phishing - Malicious
- BitDefender - phishing - Malicious
- CRDF - Malicious
- CyRadar - phishing - Malicious
- Emsisoft - malware - Malicious
- Forcepoint ThreatSeeker - phishing - Malicious
- Fortinet - phishing - Malicious
- G-Data - phishing - Malicious
- Kaspersky - phishing - Malicious
- Lionic - phishing - Malicious
- Rising - phishing - Malicious
- SafeToOpen - phishing - Malicious
- Seclookup - Malicious
- SOCRadar - phishing - Malicious
- Sophos - phishing - Malicious
- VIPRE - phishing - Malicious
- Webroot - Malicious
- DNS8 - Suspicious
- ESET - Suspicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- Cluster25 - Unrated
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- desenmascara.me - Clean
- Dr.Web - Clean
- EmergingThreats - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Fortra - Unrated
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- LevelBlue - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Snort IP sample list - Unrated
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- ViriBack - Clean
- VX Vault - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
The domain has expired - click here for more information.
What the captured page showed
1 observation- 01
The domain has expired - click here for more information.
03 · Investigation Story
Investigation story
What the site claims
Redirecting...
What we observed
The page content was captured and checked alongside 64 antivirus results.
What independent research found
1 external finding was saved and compared with the page evidence.
What remains unverified
The checks completed, but ownership, business claims, and future site behavior can still change after this snapshot.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Unknown
Observed behavior
Evidence behind this classification
- 0117 malicious and 3 suspicious detections across 94 engines, with 15 independent antivirus families reporting an adverse result.
- 0215 independent antivirus families reported an adverse result.
- 03One public warning on a scam-warning or security site: "jesauvelasecu.info 21 VT Active allegro"
Web research findings
Independent findings for jesauvelasecu.info, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- PhishDestroyopen
"jesauvelasecu.info 21 VT Active allegro"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainjesauvelasecu.info
- Redirects tojesauvelasecu.info
- Hosted byLinode
Domain Timeline
- Oct 8, 2025Domain registered
First appeared in WHOIS records — 1 year old when this review was saved.
- Oct 20, 2026Saved security review — Rated Dangerous
The completed checks from this saved scan are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
maliciousMalware, phishing, credential theft and hostile infrastructure.
15 independent antivirus families reported an adverse result. · The domain is expired and shows a NameSilo parking page with a 'Learn More' link to the registrar.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
One public warning on a scam-warning or security site: "jesauvelasecu.info 21 VT Active allegro"
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 20 of 94 engines flagged | Completed | Adverse | fresh · analysed Oct 19, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 20, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Oct 20, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 20, 2026 |
| Independent research | 1 independent finding was saved | Completed | Adverse | this scan · Oct 20, 2026 |
- Antivirus
- Result20 of 94 engines flagged
- CompletionCompleted
- FindingAdverse
- Freshnessfresh · analysed Oct 19, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 20, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 20, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 20, 2026
- Independent research
- Result1 independent finding was saved
- CompletionCompleted
- FindingAdverse
- Freshnessthis scan · Oct 20, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is jesauvelasecu.info a scam or a legit website?
Is jesauvelasecu.info safe to use?
What should I do if I already gave my details to jesauvelasecu.info?
Can I get my money back from jesauvelasecu.info?
Did jesauvelasecu.info steal my password or personal information?
How do I report jesauvelasecu.info?
Why does jesauvelasecu.info look legitimate if it's a scam?
Has jesauvelasecu.info been flagged by antivirus engines?
Is jesauvelasecu.info on any phishing or malware blacklists?
How old is the jesauvelasecu.info domain?
Where is jesauvelasecu.info hosted?
How often is the jesauvelasecu.info report updated?
08 · Final Verdict
Final verdict
Expired domain with a documented phishing history now sits on a NameSilo parking page
jesauvelasecu.info is not a working website. It currently resolves to a NameSilo parking page that states the domain has expired, and the only interactive element is a generic 'Learn More' link pointing back to the registrar. That alone would be unremarkable, but the domain carries a heavy adverse history: 17 malicious and 3 suspicious detections across 94 engines, 15 independent antivirus families reporting an adverse result, and a threat-feed record tying it to active phishing infrastructure. The domain is roughly a year old, which is consistent with a short-lived phishing campaign that has since lapsed. Because the domain is expired and parked, there is no live credential-harvesting page to interact with right now, but the reputation damage is real and the domain could be re-registered and reactivated at any time. The score reflects that combination: no current live threat surface, but a strongly documented malicious past and no legitimate operator identity behind it.
09 · Community