
Is joyjak.st safe?
http://joyjak.st/
Coveragepartial2 of 4 applicable core capabilities
joyjak.st is a bait-and-switch shock site that triggers loud audio, visual shocks, and unexpected file downloads when users interact with the page.
The site presents itself as an imageboard for sharing 'joyjaks' but functions as a Kekma-style screamer that delivers malicious shocks and downloads upon clicking anywhere on the page. Multiple antivirus engines flag the domain as malicious or suspicious, and external documentation confirms its deceptive behavior.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
The site presents itself as an imageboard for sharing 'joyjaks' but functions as a Kekma-style screamer that delivers malicious shocks and downloads upon clicking anywhere on the page. Multiple antivirus engines flag the domain as malicious or suspicious, and external documentation confirms its deceptive behavior.
Security detections and external documentation
Three independent antivirus engines (alphaMountain.ai, Fortinet, and Gridinsoft) have flagged joyjak.st as malicious or suspicious, with Gridinsoft specifically classifying it as a Suspicious Website.
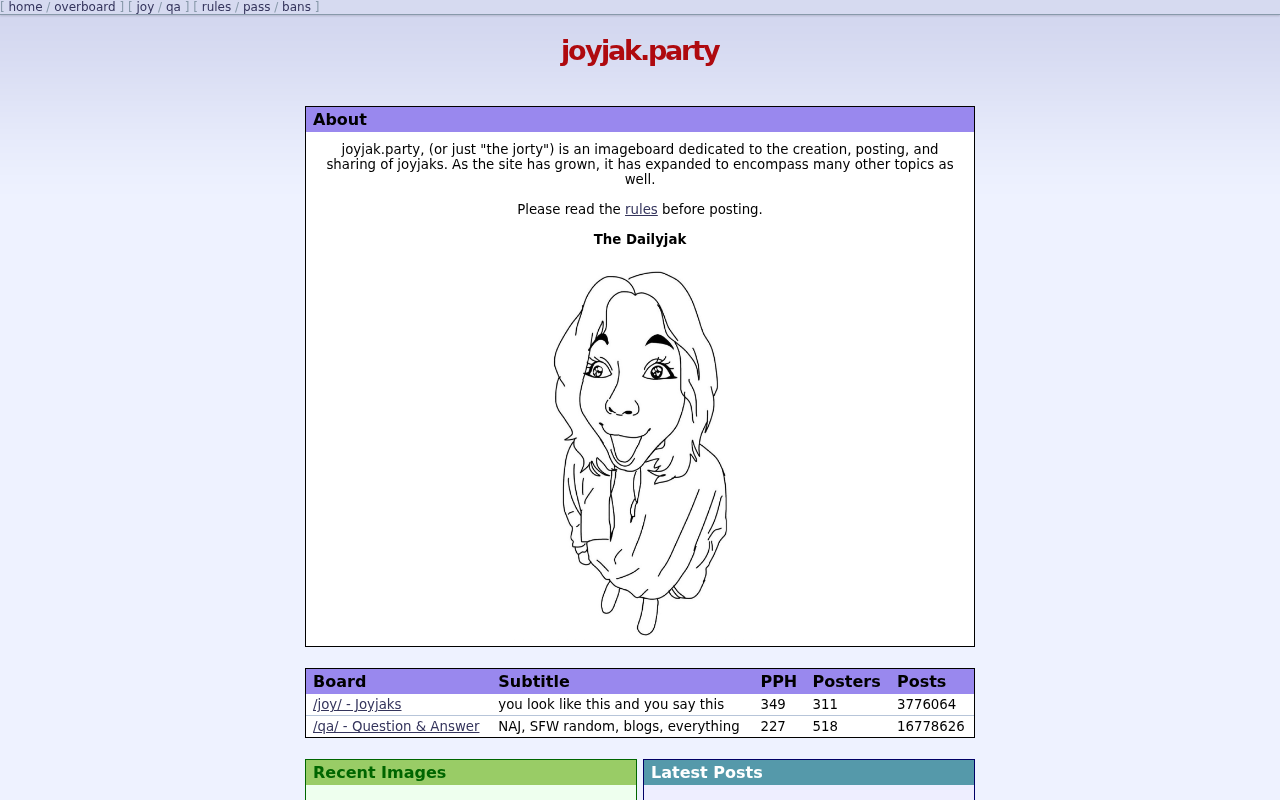
External research documentation identifies the site as a 'Joyjak Screamer' that appears as a normal imageboard with boards for posting joyjaks, but when users click anywhere, they experience AI-generated slot machine sounds, loud noises, and strange files being downloaded.
Observed site behavior and visitor exposure
The site lacks any direct contact email or transparent ownership information, presenting itself as an anonymous imageboard while hosting deceptive content designed to shock visitors.
The domain is hosted on GitHub Pages infrastructure, which has a moderate abuse confidence score, though this alone does not determine the malicious nature of the content served.
Why the score is 25
2 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
3/ 92
detectionsSaved result - stale
3 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 2
- Suspicious
- 1
- Total
- 92
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | malicious |
| FortinetMalicious | phishing |
| GridinsoftSuspicious | suspicious |
All 92 engine results
- alphaMountain.ai - malicious - Malicious
- Fortinet - phishing - Malicious
- Gridinsoft - suspicious - Suspicious
- 0xSI_f33d - unrated - Clean
- Abusix - clean - Clean
- Acronis - clean - Clean
- ADMINUSLabs - clean - Clean
- AILabs (MONITORAPP) - clean - Clean
- AlienVault - clean - Clean
- AlphaSOC - unrated - Clean
- Antiy-AVL - clean - Clean
- ArcSight Threat Intelligence - unrated - Clean
- AutoShun - unrated - Clean
- Bfore.Ai PreCrime - unrated - Clean
- BitDefender - clean - Clean
- Bkav - unrated - Clean
- BlockList - clean - Clean
- Blueliv - clean - Clean
- Certego - clean - Clean
- ChainPatrol - unrated - Clean
- Chong Lua Dao - clean - Clean
- CINS Army - clean - Clean
- CRDF - clean - Clean
- Criminal IP - clean - Clean
- CSIS Security Group - unrated - Clean
- CTX AI - clean - Clean
- Cyan - unrated - Clean
- Cyble - clean - Clean
- CyRadar - clean - Clean
- desenmascara.me - clean - Clean
- DNS8 - unrated - Clean
- Dr.Web - clean - Clean
- EmergingThreats - clean - Clean
- Emsisoft - clean - Clean
- Ermes - unrated - Clean
- ESET - clean - Clean
- ESTsecurity - clean - Clean
- Forcepoint ThreatSeeker - unrated - Clean
- Fortra - unrated - Clean
- G-Data - clean - Clean
- GCP Abuse Intelligence - unrated - Clean
- Google Safe Browsing - clean - Clean
- GreenSnow - clean - Clean
- GreyNoise - unrated - Clean
- Guardpot - unrated - Clean
- Heimdal Security - clean - Clean
- Hunt.io Intelligence - unrated - Clean
- IPsum - clean - Clean
- Juniper Networks - clean - Clean
- K7AntiVirus - unrated - Clean
- Kaspersky - clean - Clean
- LevelBlue - clean - Clean
- Lionic - clean - Clean
- Lumu - unrated - Clean
- Malwared - clean - Clean
- MalwarePatrol - clean - Clean
- MalwareURL - unrated - Clean
- Mimecast - unrated - Clean
- Netcraft - unrated - Clean
- OpenPhish - clean - Clean
- PhishFort - unrated - Clean
- Phishing Database - clean - Clean
- Phishtank - clean - Clean
- PREBYTES - clean - Clean
- PrecisionSec - unrated - Clean
- Quick Heal - clean - Clean
- Quttera - clean - Clean
- Rising - clean - Clean
- SafeToOpen - unrated - Clean
- Sangfor - clean - Clean
- Sansec eComscan - unrated - Clean
- Scantitan - clean - Clean
- SCUMWARE.org - clean - Clean
- Seclookup - clean - Clean
- Snort IP sample list - unrated - Clean
- SOCRadar - unrated - Clean
- Sophos - clean - Clean
- StopForumSpam - clean - Clean
- Sucuri SiteCheck - clean - Clean
- Synthient - unrated - Clean
- ThreatHive - clean - Clean
- URLhaus - clean - Clean
- URLQuery - unrated - Clean
- Viettel Threat Intelligence - clean - Clean
- VIPRE - unrated - Clean
- ViriBack - clean - Clean
- VX Vault - clean - Clean
- Webroot - clean - Clean
- Xcitium Verdict Cloud - clean - Clean
- Yandex Safebrowsing - clean - Clean
- ZeroCERT - clean - Clean
- ZeroFox - unrated - Clean
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
joyjak.party, (or just the jorty) is an imageboard dedicated to the creation, posting, and sharing of joyjaks.
What the captured page showed
1 observation- 01
joyjak.party, (or just the jorty) is an imageboard dedicated to the creation, posting, and sharing of joyjaks.
03 · Investigation Story
Investigation story
What the site claims
joyjak.party
What we observed
Saved browser evidence recorded deceptive download controls.
What independent research found
2 external findings were saved and compared with the page evidence.
What remains unverified
2 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Malware & Deceptive Downloads
Service and business model
Content
Observed behavior
Evidence behind this classification
- 01Site triggers unexpected downloads and audio/visual shocks upon interaction
- 022 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Web research findings
Independent findings for joyjak.st, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- SNCApediaopen
"joyjak.st, formerly joyjack.party, also known as the Joyjak Screamer, is a Kekma style bait-and-switch site that appears as a normal imageboard with 2 boards (/joy/ and /qa/) for the purpose of posting Joyjaks, but when you click anywhere, you WILL be shocked with AI 'slot, 'o, loud noises and strange files downloaded to your computer."
- Gridinsoftopen
"Suspicious Website Gridinsoft currently classifies this site as Suspicious Website. The report highlights 1 blacklist detections"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainjoyjak.st
- Redirects tojoyjak.st
- Hosted byGitHub, Inc.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No direct contact email found on the captured page.
Domain & Encryption
Redirect Chain
- 1301http://joyjak.st/
- 2206https://joyjak.st/
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
Additional evidence review · Additional evidence review
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
Additional evidence review
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 3 of 92 engines flagged | Limited | Adverse | stale fallback · Oct 6, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | Not available |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | Not available |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | Not available |
| Independent research | 2 independent findings were saved | Completed | Adverse | Not available |
- Antivirus
- Result3 of 92 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · Oct 6, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- FreshnessNot available
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- FreshnessNot available
- Independent research
- Result2 independent findings were saved
- CompletionCompleted
- FindingAdverse
- FreshnessNot available
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is joyjak.st a scam or a legit download site?
Is joyjak.st safe to use?
I already paid or entered my details on joyjak.st — what should I do?
Can I get my money back from joyjak.st?
Is my device infected after visiting joyjak.st?
How do I report joyjak.st?
joyjak.st looks professional — how can it still be a scam?
Has joyjak.st been flagged by antivirus engines?
Is joyjak.st on any phishing or malware blacklists?
Does joyjak.st have a valid SSL certificate?
Where is joyjak.st hosted?
How often is the joyjak.st report updated?
08 · Final Verdict
Final verdict
joyjak.st is a bait-and-switch shock site that triggers loud audio, visual shocks, and unexpected file downloads when users interact with the page.
The site presents itself as an imageboard for sharing 'joyjaks' but functions as a Kekma-style screamer that delivers malicious shocks and downloads upon clicking anywhere on the page. Multiple antivirus engines flag the domain as malicious or suspicious, and external documentation confirms its deceptive behavior.
09 · Community