

Is justynaholistycznie.pl safe?
http://justynaholistycznie.pl/
Checked on
How we checked
Coverage: complete · 6 of 6 applicable core capabilities
- Antivirus (56 of 93 engines answered): completed
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
New personal holistic-health consulting site with email-and-bank-transfer payment and no security detections
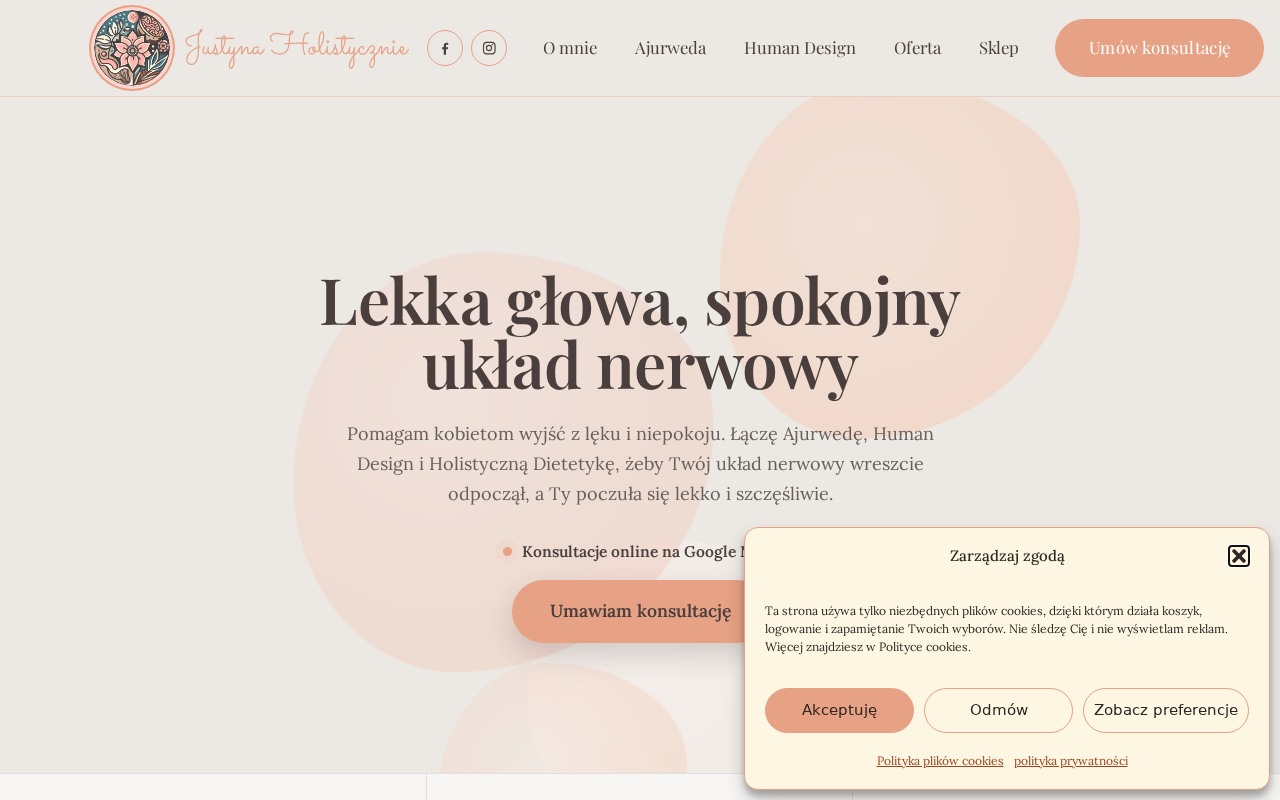
Justyna Holistycznie (justynaholistycznie.pl) presents itself as a personal holistic-health service offering consultations around Ayurveda and Human Design, with a site titled around feeling "light head, calm nervous system" and a straightforward "Umów konsultację" (book a consultation) path. Booking works by emailing hej@justynaholistycznie.pl on the site's own domain, after which the operator replies with bank transfer details and a session time is agreed once payment is made. Technical checks are clean: 0 of 93 antivirus engines flagged it, the browser threat feed returned no warning, and TLS is valid. The domain, however, is only 11 days old and the operator's full legal identity is not disclosed, which are real limits on confidence for a service that asks for a bank transfer before a session. On the evidence available this is a low-risk, unverified personal-service site rather than a demonstrated scam.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 76/100
Low Risk covers scores 70–84. 1 finding pulled the score down; 2 pushed it up.
What pulled the score down
- ModeratePayment is arranged by email and completed by manual bank transfer before a session is scheduled, which removes automatic card dispute and chargeback protection.
What pushed the score up
- SupportsThe contact address hej@justynaholistycznie.pl sits on the site's own domain rather than a free mailbox, and the site links to two social profiles.
- Supports0 of 93 antivirus engines flagged the site, the browser threat feed returned no warning, and TLS is valid.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor). Community reviews never change the Safety Score.
01 · Investigation Brief
Investigation Brief
Justyna Holistycznie (justynaholistycznie.pl) presents itself as a personal holistic-health service offering consultations around Ayurveda and Human Design, with a site titled around feeling "light head, calm nervous system" and a straightforward "Umów konsultację" (book a consultation) path. Booking works by emailing hej@justynaholistycznie.pl on the site's own domain, after which the operator replies with bank transfer details and a session time is agreed once payment is made. Technical checks are clean: 0 of 93 antivirus engines flagged it, the browser threat feed returned no warning, and TLS is valid. The domain, however, is only 11 days old and the operator's full legal identity is not disclosed, which are real limits on confidence for a service that asks for a bank transfer before a session. On the evidence available this is a low-risk, unverified personal-service site rather than a demonstrated scam.
What the site actually offers and how you would book it
The page is a personal brand site for holistic-health consulting. Vision and page text show the name Justyna Holistycznie alongside the strap line "Lekka głowa, spokojny układ nerwowy" (light head, calm nervous system), and the primary call to action is "Umów konsultację" — book a consultation.
Booking is deliberately manual and off-platform. The site tells visitors to write to hej@justynaholistycznie.pl, to choose the consultation they want, and that the operator will reply with bank transfer details; once payment is made, a day and time are agreed together. For a Human Design reading the visitor is asked to supply their exact birth date and time.
The contact address sits on the site's own domain rather than a free mailbox, and the site links out to two social profiles — Instagram and Facebook — which are the only cross-domain links found and carry no commercial or affiliate markers.
Clean technical checks, but the operator side is unverified
Nothing technical points to harm here. The saved antivirus result shows 0 malicious and 0 suspicious detections across 93 engines, the browser threat feed returned no threat warning, and the saved TLS check found a valid encrypted connection. Those results mean no detections were found — they are not a statement about the honesty of the person behind the site.
The operator-side picture is much thinner. The registrable domain is only 11 days old, and the site's own pages do not set out a full legal identity, registration number or address that a buyer could check before sending money. For a service that collects payment by bank transfer rather than through a card gateway, that combination — a very new domain plus an undisclosed operator — is the main reason this cannot be treated as fully established.
Why the payment flow matters more than the page design
There is no integrated checkout here. The visitor emails the operator, receives bank transfer details in a reply, pays by transfer, and only then fixes a session date. That means the buyer loses the automatic dispute and chargeback protections that come with a card or processor-backed checkout, and there is no visible refund or cancellation policy quoted on the evidence available.
That arrangement is common for small independent consultants and is not by itself deceptive — nothing in the reviewed page text promises a guaranteed outcome, hides a recurring charge, or pushes a gift-card, crypto or wire-only payment. The concern is purely about how little recourse exists if the session is never delivered.
Why the score is 76
The saved checks found no material threat, but the evidence was not strong enough for the highest Safe tier. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
0/ 93
No detectionsFresh result
No detections across 56 engines that rated this URL
No antivirus engine that answered raised an adverse result; 37 had no rating for this URL. This is one signal, not a guarantee.
- Malicious
- 0
- Suspicious
- 0
- Total
- 93
All 93 engine results
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Unrated
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Unrated
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
Justyna Holistycznie Lekka głowa, spokojny układ nerwowy
What the captured page showed
2 observations- 01
Justyna Holistycznie
- 02
Lekka głowa, spokojny układ nerwowy
What the page says about itself
What the site says about itself, quoted from the pages we read. The site wrote these words; they are not our findings.
- Page title
Strona główna
- Meta description
Chcę, żebyś poczuła, jak to NAPRAWDĘ jest być zdrową i szczęśliwą.
Pages we read
- Main page/Read
03 · Investigation Story
Investigation story
What the site claims
Strona główna
What we observed
The page content was captured and checked alongside 56 antivirus results.
What independent research found
The search completed without a material external warning or corroborating report.
What remains unverified
The checks completed, but ownership, business claims, and future site behavior can still change after this snapshot.
What kind of site and risk is this?
Threat category
No threat category confirmed
Service and business model
Content
Observed behavior
Evidence behind this classification
- 01The registrable domain is 11 days old, so there is no track record to judge the operator by.
- 02The contact address hej@justynaholistycznie.pl sits on the site's own domain rather than a free mailbox, and the site links to two social profiles.
- 030 of 93 antivirus engines flagged the site, the browser threat feed returned no warning, and TLS is valid.
Web research findings
Independent findings for justynaholistycznie.pl, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
No independently sourced scam reports or credibility records were found for justynaholistycznie.pl. That is common for new or low-traffic sites and does not clear the site.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainjustynaholistycznie.pl
- Redirects tojustynaholistycznie.pl
- Hosted byLH.pl Sp. z o.o.
- Referencesfonts.googleapis.com · fonts.gstatic.com
Domain Timeline
- Oct 22, 2026Domain registered
First appeared in WHOIS records — 11 days old when this review was saved.
- Nov 2, 2026Saved security review — Rated Low Risk
This saved scan found no material threat, but the evidence was not strong enough for the highest Safe tier.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- Contact email on the site's own domain (hej@justynaholistycznie.pl).
- Links to 2 social profiles.
Domain & Encryption
A certificate issued weeks or days before the scan on a domain registered recently is common on short-lived sites, though new legitimate sites look the same.
Certificate issued for justynaholistycznie.pl.
Scripts, fonts and CDNs
- Google Fonts
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://justynaholistycznie.pl/
- 2200https://justynaholistycznie.pl/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
unknownMalware, phishing, credential theft and hostile infrastructure.
No confirmed evidence in this dimension.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
Payment is arranged by email and completed by manual bank transfer before a session is scheduled, which removes automatic card dispute and chargeback protection.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 0 of 93 engines flagged | Completed | No adverse finding | fresh · analysed Nov 2, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 2, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 2, 2026 |
| Visual evidence | 2 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 2, 2026 |
| Independent research | The search completed without a material external finding | Completed | No adverse finding | this scan · Nov 2, 2026 |
- Antivirus
- Result0 of 93 engines flagged
- CompletionCompletedFindingNo adverse finding
- Freshnessfresh · analysed Nov 2, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
- Visual evidence
- Result2 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
- Independent research
- ResultThe search completed without a material external finding
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is justynaholistycznie.pl a scam or is it safe?
Is justynaholistycznie.pl safe to use?
Has justynaholistycznie.pl been flagged by antivirus engines?
Is justynaholistycznie.pl on any phishing or malware blacklists?
How old is the justynaholistycznie.pl domain?
Does justynaholistycznie.pl have a valid SSL certificate?
Where is justynaholistycznie.pl hosted?
How often is the justynaholistycznie.pl report updated?
08 · Final Verdict
Final verdict
New personal holistic-health consulting site with email-and-bank-transfer payment and no security detections
Justyna Holistycznie (justynaholistycznie.pl) presents itself as a personal holistic-health service offering consultations around Ayurveda and Human Design, with a site titled around feeling "light head, calm nervous system" and a straightforward "Umów konsultację" (book a consultation) path. Booking works by emailing hej@justynaholistycznie.pl on the site's own domain, after which the operator replies with bank transfer details and a session time is agreed once payment is made. Technical checks are clean: 0 of 93 antivirus engines flagged it, the browser threat feed returned no warning, and TLS is valid. The domain, however, is only 11 days old and the operator's full legal identity is not disclosed, which are real limits on confidence for a service that asks for a bank transfer before a session. On the evidence available this is a low-risk, unverified personal-service site rather than a demonstrated scam.
09 · Community
Community
Are you the owner of justynaholistycznie.pl?Verify and reply