
Is kuisoen.com safe?
http://kuisoen.com/
Coveragestrong3 of 4 applicable core capabilities
KUISOEN is a seven-month-old web shop with conflicting ownership signals and security-vendor warnings
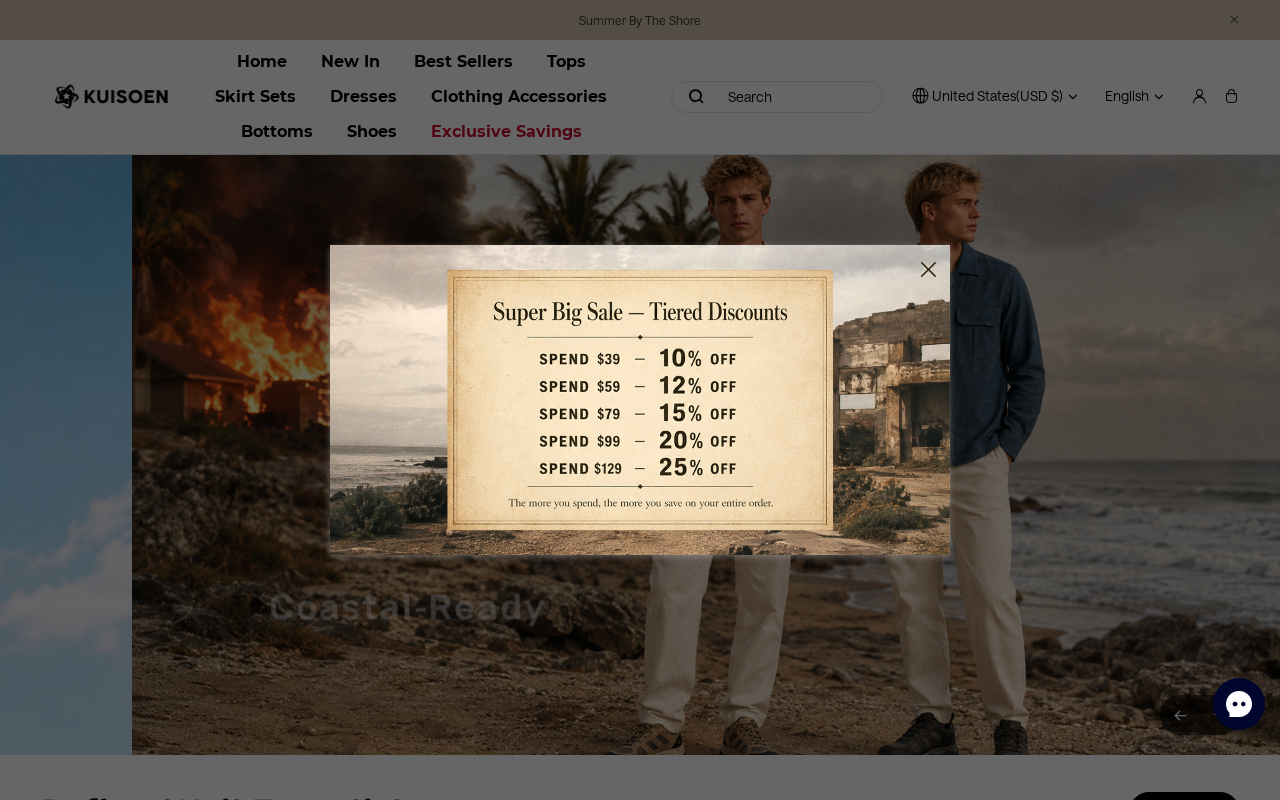
kuisoen.com is an online store running a "Super Big Sale" with tiered discounts and a bag-and-checkout flow. Its terms name FANINM INC at an address in Fresno, California. A public WHOIS record lists the domain registrant in Guangdong, China, and the domain is only 214 days old. Contact is a generic service@ mailbox, and no phone number appears on the captured page. One antivirus family reported an adverse result, and an independent scanner rates the site 37/100 and advises treating it as untrusted. No single item proves the shop fails to deliver, but together these signals put it in the High Risk band.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
kuisoen.com is an online store running a "Super Big Sale" with tiered discounts and a bag-and-checkout flow. Its terms name FANINM INC at an address in Fresno, California. A public WHOIS record lists the domain registrant in Guangdong, China, and the domain is only 214 days old. Contact is a generic service@ mailbox, and no phone number appears on the captured page. One antivirus family reported an adverse result, and an independent scanner rates the site 37/100 and advises treating it as untrusted. No single item proves the shop fails to deliver, but together these signals put it in the High Risk band.
Who runs this shop is unclear
The store's terms of service give the operator as FANINM INC at 2590 N Grove Industrial Dr in Fresno, CA. The public WHOIS record, however, lists the registrant's province as Guangdong, China. The site's own pages show no company registration number to reconcile the two.
The only contact listed is a generic service@kuisoen.com address, a pattern repeated across fake-shop networks, and the captured page lists no phone number. The domain is about seven months old, so it has little track record.
Clean connection, but warnings about the operator
The connection is properly encrypted, and the browser threat feed showed no warning. These checks only mean nothing malicious was detected. They do not show whether orders are actually fulfilled.
On the other side, a saved antivirus result showed one vendor family flagging the domain. An independent URL scanner gave it a trust score of 37/100 and advised treating it as untrusted.
What a shopper sees
Visitors land on a "Super Big Sale" with tiered discounts. From there they can open product details and continue to a bag and checkout on the same domain. The site also has order-processing and order-tracking pages.
Why the score is 40
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
3/ 91
detectionsSaved analysis from September 20, 2026 - stale
3 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 1
- Suspicious
- 2
- Total
- 91
| Engine | Finding |
|---|---|
| CRDFMalicious | malicious |
| alphaMountain.aiSuspicious | spam |
| FortinetSuspicious | spam |
All 91 engine results
- CRDF - Malicious
- alphaMountain.ai - spam - Suspicious
- Fortinet - spam - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- Criminal IP - Clean
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Unrated
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
Super Big Sale – Tiered Discounts
What the captured page showed
1 observation- 01
Super Big Sale – Tiered Discounts
03 · Investigation Story
Investigation story
What the site claims
KUISOEN
What we observed
The page content was captured and checked alongside 58 antivirus results.
What independent research found
2 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Fake Shop & Commercial Deception
Service and business model
Shop
Observed behavior
Evidence behind this classification
- 01The store gives a generic service@ mailbox as its contact, a pattern repeated across fake-shop networks.
- 02One public warning on a scam-warning or security site: "We reviewed kuisoen.com and found strong risk signals. The current trust score is 37/100, so this site should be treated as untrusted unless there is strong…"
- 03The terms name a Fresno, CA company, while WHOIS lists a Guangdong registrant.
Web research findings
Independent findings for kuisoen.com, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- Gridinsoftopen
"We reviewed kuisoen.com and found strong risk signals. The current trust score is 37/100, so this site should be treated as untrusted unless there is strong independent proof to the contrary."
- 西部数码open
"Registrant State/Province: Guang Dong Sheng"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainkuisoen.com
- Redirects tokuisoen.com
- Hosted byCloudflare, Inc.
- Referencesimg.uisksa.com · static.uisksa.com
Domain Timeline
- Mar 16, 2026Domain registered
First appeared in WHOIS records — 7 months old when this review was saved.
- Oct 16, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No phone number listed on the captured page.
- Contact email on the site's own domain (service@kuisoen.com).
- Postal address visible on the page.
Domain & Encryption
Redirect Chain
- 1301http://kuisoen.com/
- 2200https://kuisoen.com/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
The store gives a generic service@ mailbox as its contact, a pattern repeated across fake-shop networks. · The terms name a Fresno, CA company, while WHOIS lists a Guangdong registrant.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 3 of 91 engines flagged | Limited | Adverse | stale fallback · analysed Sep 20, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 16, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Oct 16, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 16, 2026 |
| Independent research | 2 independent findings were saved | Completed | Adverse | this scan · Oct 16, 2026 |
- Antivirus
- Result3 of 91 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · analysed Sep 20, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 16, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 16, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 16, 2026
- Independent research
- Result2 independent findings were saved
- CompletionCompleted
- FindingAdverse
- Freshnessthis scan · Oct 16, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is kuisoen.com a scam or a legit online store?
Is kuisoen.com safe to use?
I already paid or entered my details on kuisoen.com — what should I do?
Can I get my money back from kuisoen.com?
I ordered from kuisoen.com but nothing arrived — is it a fake shop?
How do I report kuisoen.com?
kuisoen.com looks professional — how can it still be a scam?
Has kuisoen.com been flagged by antivirus engines?
Is kuisoen.com on any phishing or malware blacklists?
How old is the kuisoen.com domain?
Does kuisoen.com have a valid SSL certificate?
How often is the kuisoen.com report updated?
08 · Final Verdict
Final verdict
KUISOEN is a seven-month-old web shop with conflicting ownership signals and security-vendor warnings
kuisoen.com is an online store running a "Super Big Sale" with tiered discounts and a bag-and-checkout flow. Its terms name FANINM INC at an address in Fresno, California. A public WHOIS record lists the domain registrant in Guangdong, China, and the domain is only 214 days old. Contact is a generic service@ mailbox, and no phone number appears on the captured page. One antivirus family reported an adverse result, and an independent scanner rates the site 37/100 and advises treating it as untrusted. No single item proves the shop fails to deliver, but together these signals put it in the High Risk band.
09 · Community