

Is preview.owasp-juice.shop safe?
http://preview.owasp-juice.shop/
Checked on
How we checked
Coverage: strong · 4 of 6 applicable core capabilities
- Antivirus (58 of 92 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading · limited: did not fully complete
- page capture: completed
- domain records: completed
- web research: completed
OWASP Juice Shop is a legitimate, intentionally vulnerable training application hosted by the non-profit OWASP project, not a real shop.
preview.owasp-juice.shop is the demo instance of OWASP Juice Shop, an open-source web application deliberately built with security flaws so that developers and security learners can practise exploitation techniques. The site's own text describes it as the opposite of a best-practice template, and independent documentation confirms it is a training target. There is no commercial checkout, no affiliate funnel and no operator-customer risk mechanism in the evidence. The score reflects a safe educational resource with two minor technical caveats: the scanned address was served over plain HTTP without a redirect to HTTPS, and one saved antivirus observation reported an adverse result that should be treated as stale rather than current.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 88/100
Safe covers scores 85–100. 1 finding pulled the score down; 3 pushed it up.
What pulled the score down
- Strong1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
What pushed the score up
- SupportsThe site is the demo instance of OWASP Juice Shop, an open-source training application hosted by the non-profit OWASP project and documented by independent security tooling.
- SupportsThe registrable domain owasp-juice.shop is 3269 days old, consistent with an established project rather than a newly created shell.
- SupportsThe browser threat feed returned no threat warning for the host.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor). Community reviews never change the Safety Score.
01 · Investigation Brief
Investigation Brief
preview.owasp-juice.shop is the demo instance of OWASP Juice Shop, an open-source web application deliberately built with security flaws so that developers and security learners can practise exploitation techniques. The site's own text describes it as the opposite of a best-practice template, and independent documentation confirms it is a training target. There is no commercial checkout, no affiliate funnel and no operator-customer risk mechanism in the evidence. The score reflects a safe educational resource with two minor technical caveats: the scanned address was served over plain HTTP without a redirect to HTTPS, and one saved antivirus observation reported an adverse result that should be treated as stale rather than current.
An intentionally insecure training application, not a storefront
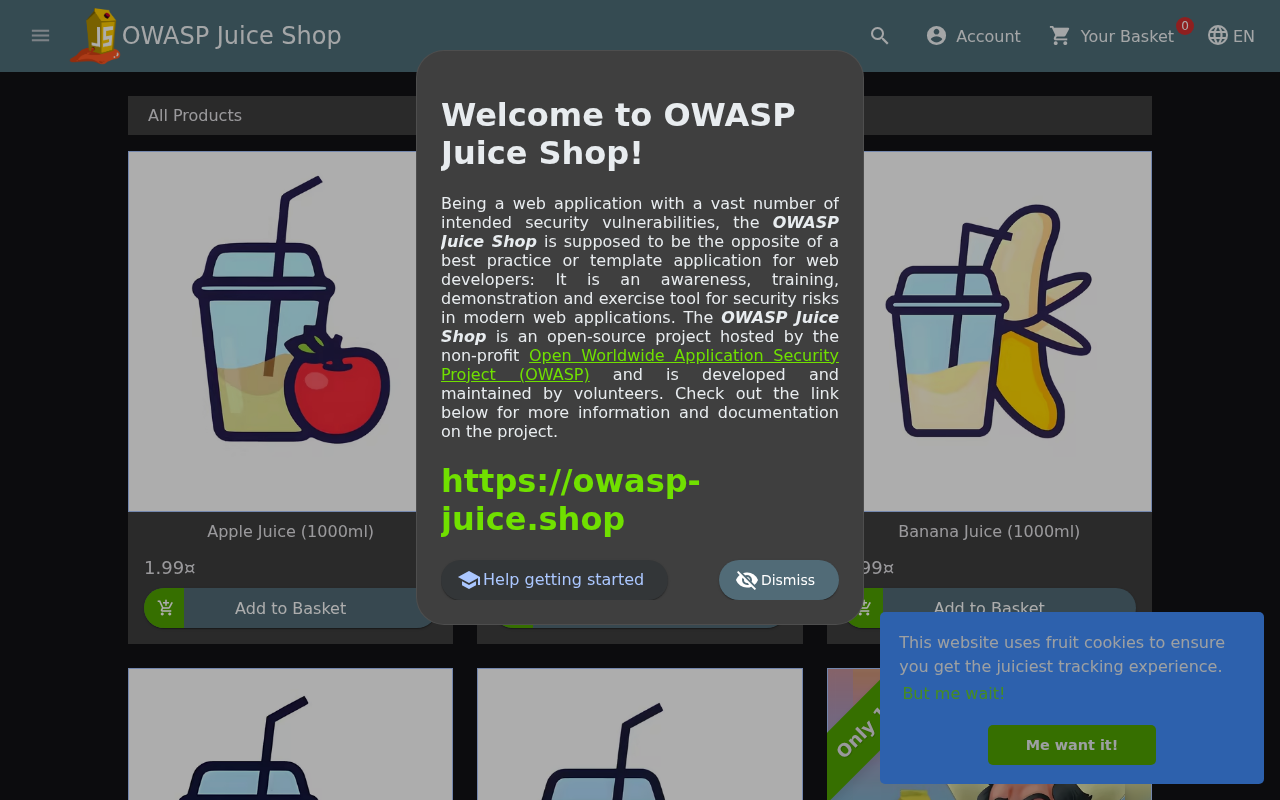
The page itself states that OWASP Juice Shop is a web application with a vast number of intended security vulnerabilities and is supposed to be the opposite of a best-practice or template application for web developers. That is the defining characteristic of the project: the flaws are the product, not an accident.
Independent documentation from the ZAP project describes the online Juice Shop as a shared instance where visitors should register a unique user because other people may change the default user. This confirms the site is a public, multi-user training environment rather than a commercial service.
The registrable domain owasp-juice.shop is 3269 days old, consistent with a long-running project rather than a recently created shell. The subdomain host itself may be newer, but the parent domain's history supports the project's established identity.
Technical caveats versus operator risk
The scanned address was served over plain HTTP with no redirect to HTTPS, so the connection to it was not encrypted even though a valid TLS certificate exists for the host. For a training site where users are told to register accounts, this is a real but minor technical weakness: credentials typed into the demo could travel unencrypted.
One saved antivirus observation reported an adverse result from a single engine. This is a stale, partial record rather than a fresh submission, so it should be treated as a historical detection to confirm rather than a current verdict on the site.
The browser threat feed returned no threat warning for the host, which is consistent with a known educational project rather than a malicious distribution point.
What happens when you use the demo
A visitor who registers an account on the public Juice Shop instance is told to use a unique username because other people may change the default user. The exposure is to other learners on a shared, deliberately broken application, not to a commercial operator.
Because the scanned address was served over plain HTTP without a redirect to HTTPS, anything typed into the demo travels unencrypted. The practical takeaway is to avoid reusing real passwords on this training instance.
Why the score is 88
The saved checks and analysis found no material threat. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
1/ 92
detectionsSaved analysis from August 25, 2026 - stale
1 engine flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 1
- Suspicious
- 0
- Total
- 92
| Engine | Finding |
|---|---|
| ESETMalicious | malware |
All 92 engine results
- ESET - malware - Malicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Unrated
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- Cluster25 - Unrated
- CRDF - Clean
- Criminal IP - Clean
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Clean
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Unrated
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- Forcepoint ThreatSeekerinformation technology
- Googleshopping
- Sophosreference
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
Being a web application with a vast number of intended security vulnerabilities, the OWASP Juice Shop is supposed to be the opposite of a best practice or template application for web developers
What the captured page showed
1 observation- 01
Being a web application with a vast number of intended security vulnerabilities, the OWASP Juice Shop is supposed to be the opposite of a best practice or template application for web developers
What the page says about itself
What the site says about itself, quoted from the pages we read. The site wrote these words; they are not our findings.
- Page title
OWASP Juice Shop
- Meta description
Probably the most modern and sophisticated insecure web application
Pages we read
- Main page/Read
03 · Investigation Story
Investigation story
What the site claims
OWASP Juice Shop
What we observed
The page content was captured and checked alongside 58 antivirus results.
What independent research found
1 external finding was saved and compared with the page evidence.
What remains unverified
2 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
No threat category confirmed
Service and business model
Content
Observed behavior
Evidence behind this classification
- 01The site is the demo instance of OWASP Juice Shop, an open-source training application hosted by the non-profit OWASP project and documented by independent security tooling.
- 02The registrable domain owasp-juice.shop is 3269 days old, consistent with an established project rather than a newly created shell.
- 03The browser threat feed returned no threat warning for the host.
Web research findings
Independent findings for preview.owasp-juice.shop, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
No independently sourced scam reports or credibility records were found for preview.owasp-juice.shop. That is common for new or low-traffic sites and does not clear the site.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainpreview.owasp-juice.shop
- Redirects topreview.owasp-juice.shop
- Hosted bySTRATO AG
- Referencesfonts.googleapis.com · fonts.gstatic.com
Domain Timeline
- Nov 20, 2017Domain registered
First appeared in WHOIS records — 8 years old when this review was saved.
- Nov 2, 2026Saved security review — Rated Safe
This saved scan found no active threat signals in the checks it completed.
preview.owasp-juice.shop has operated for years with no threat signals in this review — a long, stable track record, though it is never a guarantee on its own.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Certificate issued for *.owasp-juice.shop.
Scripts, fonts and CDNs
- Google Fonts
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
unknownComplaints, withdrawals, business conduct and commercial traps.
No confirmed evidence in this dimension.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 1 of 92 engines flagged | Limited | Adverse | stale fallback · analysed Aug 25, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 2, 2026 |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | this scan · Nov 2, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Nov 2, 2026 |
| Independent research | 1 independent finding was saved | Completed | No adverse finding | this scan · Nov 2, 2026 |
- Antivirus
- Result1 of 92 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Aug 25, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimitedFindingNo saved finding
- Freshnessthis scan · Nov 2, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
- Independent research
- Result1 independent finding was saved
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 2, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is preview.owasp-juice.shop legit and safe?
Is preview.owasp-juice.shop safe to use?
Could a legitimate site like preview.owasp-juice.shop still be used in a scam?
Has preview.owasp-juice.shop been flagged by antivirus engines?
Is preview.owasp-juice.shop on any phishing or malware blacklists?
How old is the preview.owasp-juice.shop domain?
Does preview.owasp-juice.shop have a valid SSL certificate?
Where is preview.owasp-juice.shop hosted?
How often is the preview.owasp-juice.shop report updated?
08 · Final Verdict
Final verdict
OWASP Juice Shop is a legitimate, intentionally vulnerable training application hosted by the non-profit OWASP project, not a real shop.
preview.owasp-juice.shop is the demo instance of OWASP Juice Shop, an open-source web application deliberately built with security flaws so that developers and security learners can practise exploitation techniques. The site's own text describes it as the opposite of a best-practice template, and independent documentation confirms it is a training target. There is no commercial checkout, no affiliate funnel and no operator-customer risk mechanism in the evidence. The score reflects a safe educational resource with two minor technical caveats: the scanned address was served over plain HTTP without a redirect to HTTPS, and one saved antivirus observation reported an adverse result that should be treated as stale rather than current.
09 · Community
Community
Are you the owner of preview.owasp-juice.shop?Verify and reply