
Is rcoinheart.com safe?
http://rcoinheart.com/
Coveragestrong3 of 4 applicable core capabilities
RCoinheart is a young precious-metals storefront with no verifiable operator, a free-mail support inbox, and a Terms page naming a different domain as the operator
RCoinheart presents itself as an online shop selling silver coins and similar items, with a cart, a payment-method page, order tracking, and a stated 30-day money-back policy. The technical side is not the problem: the saved TLS check shows a valid encrypted connection and the browser threat feed returned no warning, though one independent antivirus family did flag the domain as phishing. The real concern is operator transparency. The registrable domain is only 355 days old, the site lists no phone number and no postal address, and its only visible support address is a free Gmail inbox rather than a mailbox on its own domain. Most tellingly, the site's own Terms page names a different domain, www.joyfultobuy.com, as the operator. That combination — a new domain, no verifiable business identity, off-domain free-mail contact, and a cross-domain operator reference — is the pattern of a template-based storefront rather than an established precious-metals dealer. It does not by itself prove that orders go undelivered, but it means a buyer has no reliable way to identify, contact, or hold accountable the party taking their money.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
RCoinheart presents itself as an online shop selling silver coins and similar items, with a cart, a payment-method page, order tracking, and a stated 30-day money-back policy. The technical side is not the problem: the saved TLS check shows a valid encrypted connection and the browser threat feed returned no warning, though one independent antivirus family did flag the domain as phishing. The real concern is operator transparency. The registrable domain is only 355 days old, the site lists no phone number and no postal address, and its only visible support address is a free Gmail inbox rather than a mailbox on its own domain. Most tellingly, the site's own Terms page names a different domain, www.joyfultobuy.com, as the operator. That combination — a new domain, no verifiable business identity, off-domain free-mail contact, and a cross-domain operator reference — is the pattern of a template-based storefront rather than an established precious-metals dealer. It does not by itself prove that orders go undelivered, but it means a buyer has no reliable way to identify, contact, or hold accountable the party taking their money.
No verifiable operator behind the storefront
The captured page shows no phone number and no operator postal address, so there is no way to identify the business behind the shop or to reach it outside email. The only support address visible is adorebuyservice@gmail.com, a free-mail inbox rather than a mailbox on the site's own domain. A legitimate precious-metals dealer handling payments and shipping normally publishes a registered company name, a physical address, and a domain-based contact address; none of those appear here.
The registrable domain is only 355 days old, which is young for a store asking customers to pay for physical goods that must then be shipped. Age alone is not proof of wrongdoing, but combined with the missing business details it means there is no track record a buyer can check before paying.
The Terms page names a different domain as the operator
The site's own Terms of Service page references www.joyfultobuy.com as the operator. That is a cross-domain reference on a storefront that otherwise presents itself as RCoinheart, and it suggests the shop was assembled from a template or belongs to a wider network of sites rather than being run by the business it names. A visitor reading the Terms would be dealing with an entity whose stated identity does not match the domain they are shopping on.
The commercial flow itself is ordinary e-commerce: the page includes a payment-method page, an order-tracking link, and a view-full-details control, and the banner advertises free shipping on international orders over $50 alongside a 30-day money-back claim. Those are normal shop features, but they sit on top of an operator identity that cannot be verified, which is what makes the checkout path risky rather than reassuring.
Clean encryption and Safe Browsing do not offset the operator risk
The saved TLS check found a valid encrypted connection and the browser threat feed returned no threat warning, so the connection itself is not the danger. However, one independent antivirus family flagged the domain as phishing, and that detection comes from a saved observation rather than a fresh submission, so it should be treated as a real but possibly dated signal rather than a current verdict.
The decisive risk here is not malware or a technical exploit; it is that a customer paying this shop has no verifiable counterparty. With no company registration, no address, no phone number, and a free-mail contact, resolving a dispute, requesting a refund under the advertised 30-day policy, or confirming who actually received the payment would be difficult. That is an operator and customer risk, and it is why the score sits in the High Risk band despite the clean technical checks.
Why the score is 42
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
3/ 92
detectionsSaved analysis from October 3, 2026 - stale
3 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 1
- Suspicious
- 2
- Total
- 92
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | phishing |
| GridinsoftSuspicious | suspicious |
| URLQuerySuspicious | suspicious |
All 92 engine results
- alphaMountain.ai - phishing - Malicious
- Gridinsoft - Suspicious
- URLQuery - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
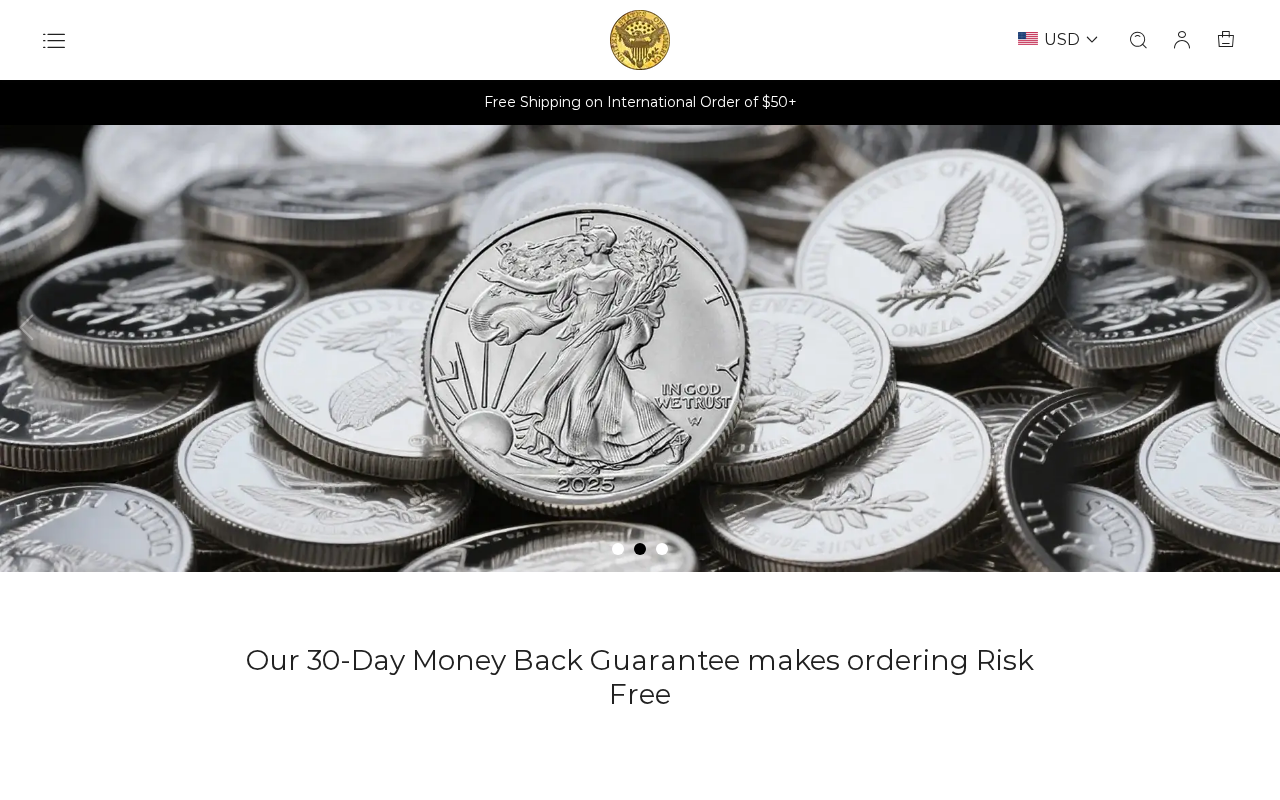
The website displays a header with a logo, navigation menu, currency selector, search icon, user account icon, and shopping cart icon. A banner states 'Free Shipping on International Order of $50+'. The main content area shows a hero image of silver coins, followed by a text block: 'Our 30-Day Money Back Guarantee makes ordering Risk Free'.
What the captured page showed
1 observation- 01
The website displays a header with a logo, navigation menu, currency selector, search icon, user account icon, and shopping cart icon. A banner states 'Free Shipping on International Order of $50+'. The main content area shows a hero image of silver coins, followed by a text block: 'Our 30-Day Money Back Guarantee makes ordering Risk Free'.
03 · Investigation Story
Investigation story
What the site claims
RCoinheart
What we observed
The page content was captured and checked alongside 60 antivirus results.
What independent research found
The search completed without a material external warning or corroborating report.
What remains unverified
1 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Fake Shop & Commercial Deception
Service and business model
Shop
Observed behavior
Evidence behind this classification
- 01The store's contact address is a free-mail inbox (gmail.com) rather than a mailbox on its own domain.
- 021 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- 03The only visible support address is a free Gmail inbox rather than a mailbox on the site's own domain.
Web research findings
Independent findings for rcoinheart.com, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
No independently sourced scam reports or credibility records were found for rcoinheart.com. That is common for new or low-traffic sites and does not clear the site.
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainrcoinheart.com
- Redirects towww.rcoinheart.com
- Hosted byAlibaba Cloud - US
- Referencesstatic.abeloo.top · fonts.abeloo.top
Domain Timeline
- Oct 27, 2025Domain registered
First appeared in WHOIS records — 11 months old when this review was saved.
- Oct 17, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No contact email uses the site's own domain.
- Business contact uses a free-mail provider (gmail.com).
- No phone number listed on the captured page.
- No operator postal address visible on the captured page.
Domain & Encryption
Redirect Chain
- 1301http://rcoinheart.com/
- 2302https://rcoinheart.com/
- 3200https://www.rcoinheart.com/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
1 independent antivirus family reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
The store's contact address is a free-mail inbox (gmail.com) rather than a mailbox on its own domain. · The site's Terms page names www.joyfultobuy.com as the operator, a different domain from the one being shopped on.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 3 of 92 engines flagged | Limited | Adverse | stale fallback · analysed Oct 3, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 17, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Oct 17, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 17, 2026 |
| Independent research | The search completed without a material external finding | Completed | No adverse finding | this scan · Oct 17, 2026 |
- Antivirus
- Result3 of 92 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · analysed Oct 3, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 17, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 17, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 17, 2026
- Independent research
- ResultThe search completed without a material external finding
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 17, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is rcoinheart.com a scam or a legit online store?
Is rcoinheart.com safe to use?
What should I do if I already gave my details to rcoinheart.com?
Can I get my money back from rcoinheart.com?
I ordered from rcoinheart.com but nothing arrived — is it a fake shop?
How do I report rcoinheart.com?
Why does rcoinheart.com look legitimate if it's a scam?
Has rcoinheart.com been flagged by antivirus engines?
Is rcoinheart.com on any phishing or malware blacklists?
How old is the rcoinheart.com domain?
Does rcoinheart.com have a valid SSL certificate?
How often is the rcoinheart.com report updated?
08 · Final Verdict
Final verdict
RCoinheart is a young precious-metals storefront with no verifiable operator, a free-mail support inbox, and a Terms page naming a different domain as the operator
RCoinheart presents itself as an online shop selling silver coins and similar items, with a cart, a payment-method page, order tracking, and a stated 30-day money-back policy. The technical side is not the problem: the saved TLS check shows a valid encrypted connection and the browser threat feed returned no warning, though one independent antivirus family did flag the domain as phishing. The real concern is operator transparency. The registrable domain is only 355 days old, the site lists no phone number and no postal address, and its only visible support address is a free Gmail inbox rather than a mailbox on its own domain. Most tellingly, the site's own Terms page names a different domain, www.joyfultobuy.com, as the operator. That combination — a new domain, no verifiable business identity, off-domain free-mail contact, and a cross-domain operator reference — is the pattern of a template-based storefront rather than an established precious-metals dealer. It does not by itself prove that orders go undelivered, but it means a buyer has no reliable way to identify, contact, or hold accountable the party taking their money.
09 · Community