

Is viinisi.fi safe?
http://viinisi.fi/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (58 of 92 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
Finnish wine shop with a clean technical profile, but a third-party scanner warning about paid orders not arriving and no visible business address
viinisi.fi is a Finnish-language Shopify storefront selling wine bundles, with a same-site cart and checkout, a domain email and phone number, published customer-service hours and a stated 30-day cancellation right. Nothing malicious was found technically: no threat warning from Safe Browsing, a valid encrypted connection, and no popups, downloads or notification prompts during rendering. The concerns are about the operator rather than the code: a third-party scanner page labels the shop suspicious and cites recurring complaints of payment without delivery and wrong or inferior goods, and no postal address or company registration is visible on the captured page. That mix of clean infrastructure and unresolved delivery/identity questions places the site in the moderate-risk band rather than Safe.
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 62/100
Moderate Risk covers scores 45–69. 3 findings pulled the score down; 4 pushed it up.
What pulled the score down
- ModerateOne public warning on a scam-warning or security site: "Viinisi.fi est signalé comme boutique suspecte. Les plaintes récurrentes concernent paiement sans livraison, produit différent ou qualité très inférieure."
- Moderate1 antivirus result marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- MinorNo operator postal address or company registration is visible on the captured page, only a domain email and phone.
What pushed the score up
- SupportsSafe Browsing returned no threat warning and the saved TLS check found a valid encrypted connection.
- SupportsThe shop publishes a domain email address, a Finnish phone number and customer-service hours.
- SupportsThe domain is 623 days old and the hosting IP has an abuse confidence score of 0/100.
- SupportsOne review site concludes the shop is probably not a scam but legitimate, while noting low traffic rank.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor). Community reviews never change the Safety Score.
01 · Investigation Brief
Investigation Brief
viinisi.fi is a Finnish-language Shopify storefront selling wine bundles, with a same-site cart and checkout, a domain email and phone number, published customer-service hours and a stated 30-day cancellation right. Nothing malicious was found technically: no threat warning from Safe Browsing, a valid encrypted connection, and no popups, downloads or notification prompts during rendering. The concerns are about the operator rather than the code: a third-party scanner page labels the shop suspicious and cites recurring complaints of payment without delivery and wrong or inferior goods, and no postal address or company registration is visible on the captured page. That mix of clean infrastructure and unresolved delivery/identity questions places the site in the moderate-risk band rather than Safe.
Delivery complaints and a missing business address
A third-party URL scanner page describes viinisi.fi as a suspicious shop and lists recurring complaints about payment without delivery and about goods arriving different from what was ordered or of much lower quality. That is one vendor's assessment rather than a set of independently verified customer reports, so it should be weighed as a warning sign, not as proof that any particular order failed.
The same scanner page notes that the domain was registered through Gandi SAS and that the owner's details are not publicly available, and that no complaints contact was found. On the site itself, the captured page shows a domain email address and a Finnish phone number with service hours, but no postal address or company registration number, which makes it harder for a buyer to identify and pursue the seller if an order goes wrong.
Clean technical checks and genuine-looking shop signals
The technical side is unremarkable in a good way: the browser threat feed returned no threat warning, the saved TLS check found a valid encrypted connection, and the hosting IP carries an abuse confidence score of 0/100 across 92 saved reports. The domain is 623 days old, which is old enough to be a real trading history rather than a throwaway registration.
One saved antivirus observation marks the URL as suspicious, but it is a single engine's result from a saved scan rather than a fresh submission, and it is the same vendor whose page carries the shop warning. Independent review coverage is mixed: one review site concludes the shop is probably not a scam but legitimate and notes that people are giving it positive reviews, while also noting a rather low traffic rank. The site itself displays an independent review platform's rating of 4.7 from 928 reviews, though the underlying profile was not independently inspected.
Why the score is 62
One public warning on a scam-warning or security site: "Viinisi.fi est signalé comme boutique suspecte. Les plaintes récurrentes concernent paiement sans livraison, produit différent ou qualité très inférieure.". Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
1/ 92
detectionsSaved analysis from October 2, 2026 - stale
1 engine flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 0
- Suspicious
- 1
- Total
- 92
| Engine | Finding |
|---|---|
| GridinsoftSuspicious | suspicious |
All 92 engine results
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- alphaMountain.ai - Unrated
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESET - Clean
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Unrated
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- Googleshopping
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
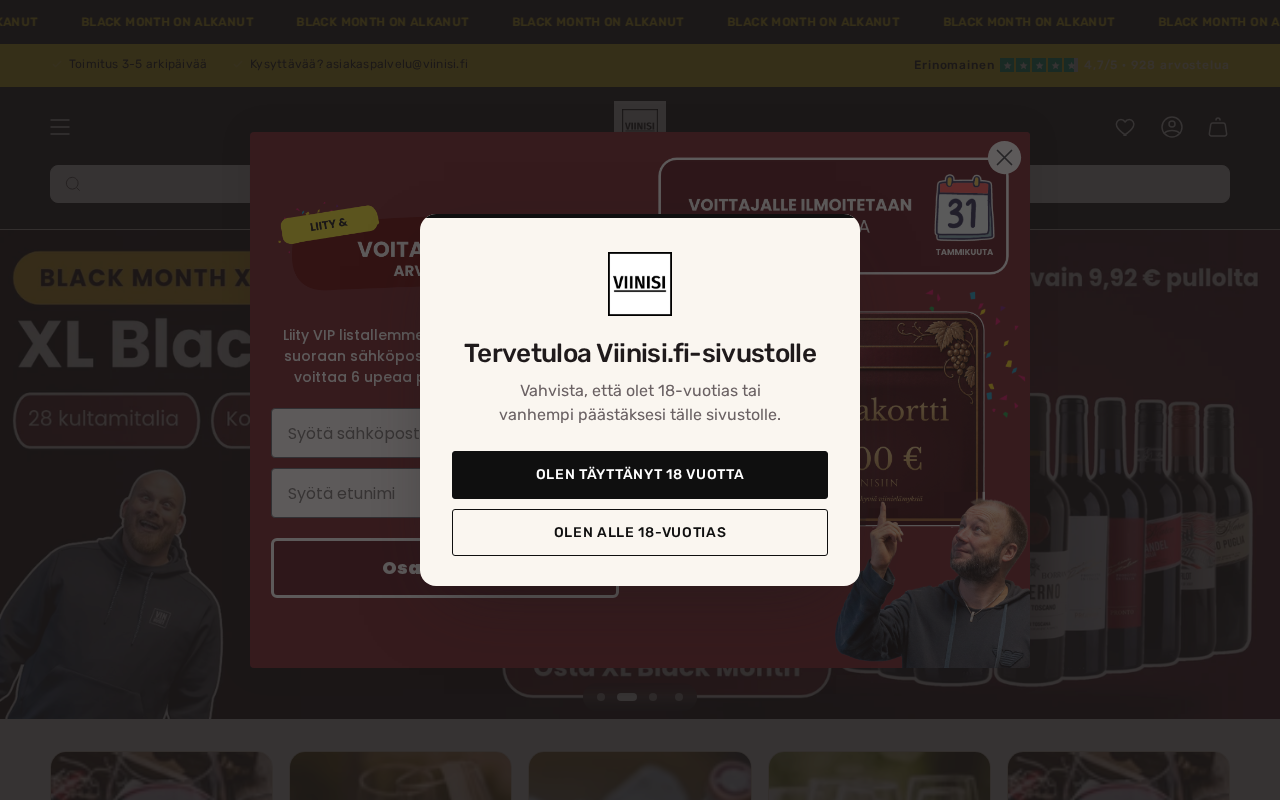
Centered modal titled 'Tervetulo Viinisi.fi-sivustolle' asks the visitor to confirm they are 18 or older, with buttons 'OLEN TÄYTTÄNYT 18 VUOTTA' and 'OLEN ALLE 18-VUOTIAS'. Top marquee banner repeats 'BLACK MONTH ON ALKANUT' and a header strip shows 'Toimitus 3-5 arkipäivää', 'asiakaspalvelu@viinisi.fi' and a Trustpilot 'Erinomainen' rating. Background overlay promotes an 'XL Black' offer, a VIP email signup ('LIITY VIP-listallemme'), a '31 TAMMIKUUTA' giveaway countdown and 'vain 9,92 € pullolta' pricing. Wine bottles and two men gesturing are shown in the background hero imagery; no checkout, payment or delivery screens are visible.
What the captured page showed
4 observations- 01
Centered modal titled 'Tervetulo Viinisi.fi-sivustolle' asks the visitor to confirm they are 18 or older, with buttons 'OLEN TÄYTTÄNYT 18 VUOTTA' and 'OLEN ALLE 18-VUOTIAS'.
- 02
Top marquee banner repeats 'BLACK MONTH ON ALKANUT' and a header strip shows 'Toimitus 3-5 arkipäivää', 'asiakaspalvelu@viinisi.fi' and a Trustpilot 'Erinomainen' rating.
- 03
Background overlay promotes an 'XL Black' offer, a VIP email signup ('LIITY VIP-listallemme'), a '31 TAMMIKUUTA' giveaway countdown and 'vain 9,92 € pullolta' pricing.
- 04
Wine bottles and two men gesturing are shown in the background hero imagery; no checkout, payment or delivery screens are visible.
What the page says about itself
What the site says about itself, quoted from the pages we read. The site wrote these words; they are not our findings.
- Page title
sinunviinisi.fi
Pages we read
- Main page/Read
- Terms/policies/terms-of-serviceRead
- Refund / returns policy/policies/refund-policyRead
- Shipping policy/policies/shipping-policyRead
- Contact page/policies/contact-informationRead
03 · Investigation Story
Investigation story
What the site claims
sinunviinisi.fi
What we observed
The page content was captured and checked alongside 58 antivirus results.
What independent research found
5 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Fake Shop & Commercial Deception
Service and business model
Shop
Observed behavior
Evidence behind this classification
- 01One public warning on a scam-warning or security site: "Viinisi.fi est signalé comme boutique suspecte. Les plaintes récurrentes concernent paiement sans livraison, produit différent ou qualité très inférieure."
- 02No operator postal address or company registration is visible on the captured page, only a domain email and phone.
- 031 antivirus result marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
If this is a scam — what it means for you
What happens when you buy
A visitor adds wine to the cart and proceeds through 'Siirry maksamaan' on the same domain; the checkout shows an estimated delivery of 3–5 business days, a checkbox accepting the shop terms, and a stated 30-day cancellation right. No cross-domain payment redirect or affiliate hop appears in the link graph, so the money path itself is a normal same-site transaction.
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
The commercial pressure points are ordinary retail tactics rather than traps: a free-shipping threshold that prompts further spending to reach €119, a footer newsletter signup, and promotional overlays for a 'Black Month' offer, a VIP email list and a giveaway countdown. None of these were observed to hide recurring billing or a withdrawal-style fee.
If you want to order, keep the first purchase small and pay with a method that offers chargeback protection such as a credit card or PayPal rather than a bank transfer. Before paying, ask the shop in writing for its company name, business ID and postal address, and check an independent review platform's profile directly rather than relying on the embedded widget. Given the unresolved delivery complaints and the missing business address, treat any large or prepaid order with caution.
Web research findings
Independent findings for viinisi.fi, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- Gridinsoft (FR)open
"Viinisi.fi est signalé comme boutique suspecte. Les plaintes récurrentes concernent paiement sans livraison, produit différent ou qualité très inférieure."
- Gridinsoft (FR)open
"Ce domaine a été enregistré il y a 1 an par la société Gandi SAS et les informations sur le propriétaire ne sont pas accessibles publiquement. Aucun contact pour les réclamations trouvé."
- ScamAdviseropen
"In summary, viinisi.fi is probably not a scam but legit."
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domainviinisi.fi
- Redirects toviinisi.fi
- Hosted byShopify, Inc.
- Referencesfonts.shopifycdn.com · chat.cdn.zuzana.ai
Domain Timeline
- Feb 18, 2025Domain registered
First appeared in WHOIS records — 1.7 years old when this review was saved.
- Nov 3, 2026Saved security review — Rated Moderate Risk
The evidence in this saved scan is mixed or incomplete; the completed checks are detailed above.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No operator postal address visible on the captured page.
- Contact email on the site's own domain (asiakaspalvelu@viinisi.fi).
- Phone number listed (+358 304108620).
- Links to 4 social profiles.
Domain & Encryption
Certificate issued for viinisi.fi.
A shared content-delivery network address answers for many sites, so it is not the site's own server and says nothing about who runs it.
Analytics and ads
- Microsoft Clarity
Chat, reviews and email
- Klaviyo
Payment providers the page loads
- Shop Pay
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://viinisi.fi/
- 2200https://viinisi.fi/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
unknownMalware, phishing, credential theft and hostile infrastructure.
1 antivirus result marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
One public warning on a scam-warning or security site: "Viinisi.fi est signalé comme boutique suspecte. Les plaintes récurrentes concernent paiement sans livraison, produit différent ou qualité très inférieure." · No operator postal address or company registration is visible on the captured page, only a domain email and phone.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 1 of 92 engines flagged | Limited | Adverse | stale fallback · analysed Oct 2, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 3, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 3, 2026 |
| Visual evidence | 4 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 3, 2026 |
| Independent research | 5 independent findings were saved | Completed | Adverse | this scan · Nov 3, 2026 |
- Antivirus
- Result1 of 92 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Oct 2, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 3, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 3, 2026
- Visual evidence
- Result4 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 3, 2026
- Independent research
- Result5 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 3, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is viinisi.fi a scam or is it safe?
Is viinisi.fi safe to use?
Has viinisi.fi been flagged by antivirus engines?
Is viinisi.fi on any phishing or malware blacklists?
How old is the viinisi.fi domain?
Does viinisi.fi have a valid SSL certificate?
Where is viinisi.fi hosted?
How often is the viinisi.fi report updated?
08 · Final Verdict
Final verdict
Finnish wine shop with a clean technical profile, but a third-party scanner warning about paid orders not arriving and no visible business address
viinisi.fi is a Finnish-language Shopify storefront selling wine bundles, with a same-site cart and checkout, a domain email and phone number, published customer-service hours and a stated 30-day cancellation right. Nothing malicious was found technically: no threat warning from Safe Browsing, a valid encrypted connection, and no popups, downloads or notification prompts during rendering. The concerns are about the operator rather than the code: a third-party scanner page labels the shop suspicious and cites recurring complaints of payment without delivery and wrong or inferior goods, and no postal address or company registration is visible on the captured page. That mix of clean infrastructure and unresolved delivery/identity questions places the site in the moderate-risk band rather than Safe.
09 · Community
Community
Are you the owner of viinisi.fi?Verify and reply