

Is cherrybetty.com safe?
http://cherrybetty.com/
Checked on
How we checked
Coverage: strong · 5 of 6 applicable core capabilities
- Antivirus (60 of 93 engines answered) · saved result: did not fully complete
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
Cherrybetty sells vintage-style western clothing from an undisclosed operator, and independent checks rate it 1.2 stars across 199 reviews with security vendors calling it a suspected fake shop.
cherrybetty.com is a Shoplazza-hosted women's fashion storefront selling embroidered western shirts, blouses and dresses, with coupon banners, struck-through comparison prices and an email-capture pop-up offering $60 off. The technical side is not the problem: Safe Browsing is clean, the certificate is valid and the CDN address has no abuse reports. The problem is the merchant. No operator name, address, phone or email appears in the page content we captured, and the footer was beyond our read limit so it went unreviewed. Independent checks describe 199 an independent review platform's reviews averaging 1.2 stars, a 'mostly dissatisfied' rating, and reviewers saying the products do not match the photos, sizing is wrong and messages go unanswered. Security vendors also classify the domain as a suspected fake shop. That combination puts it in the High Risk band.
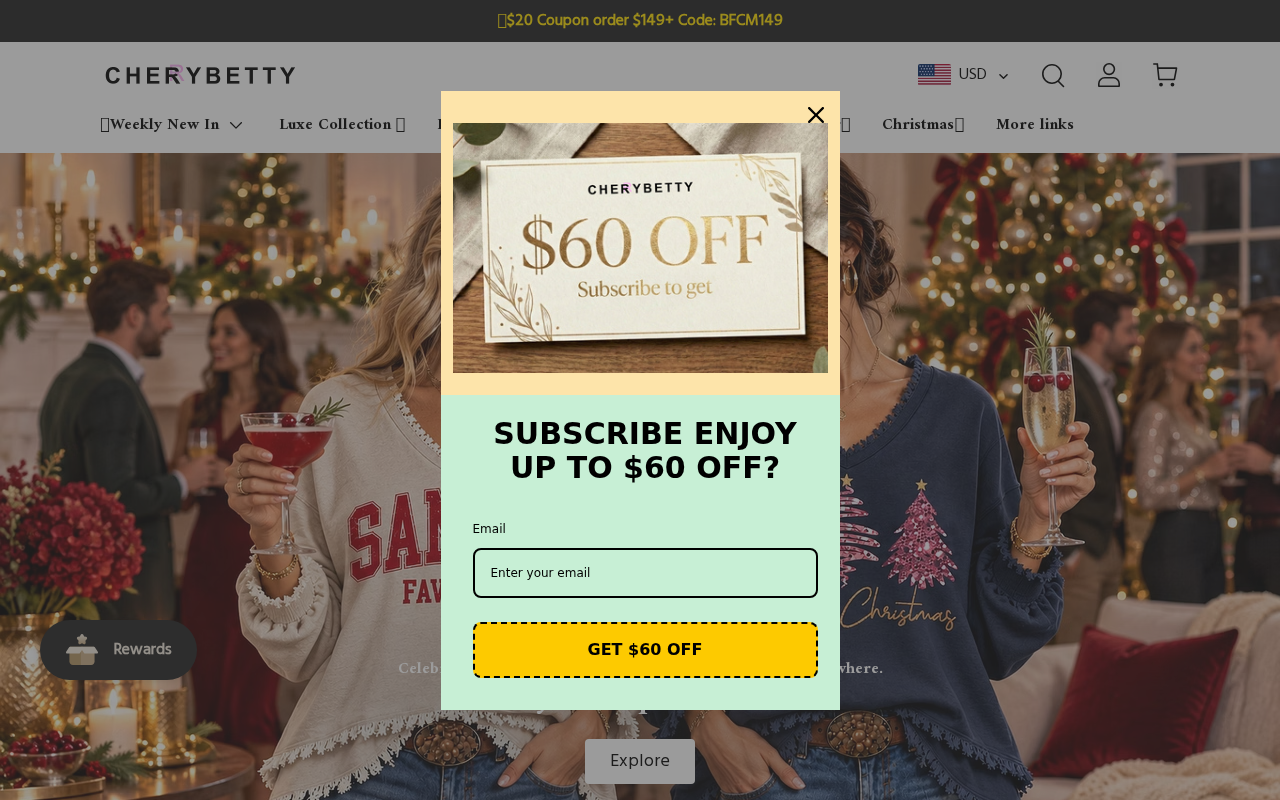 Saved site captureCaptured safely during this scan3 antivirus engines flagged this URLalphaMountain.ai, ESET, GridinsoftSaved antivirus result from Nov 3, 2026
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 38/100
High Risk covers scores 21–44. 5 findings pulled the score down; 4 pushed it up.
What pulled the score down
- Moderate3 independent sources carry complaints or warnings about this site, including: "Be cautious: its 199 reviews on Trustpilot average only 1.2 stars out of 5. We could not find an address, an email address or a phone number."
- Moderate3 independent sources carry complaints or warnings about this site, including: "O Gridinsoft bloqueia este site porque ele foi classificado como loja suspeita."
- Moderate3 independent sources carry complaints or warnings about this site, including: "Patterns don’t match what they show you on their site. Poor quality, sizing is inaccurate. They do not respond to messages on social media or email."
- Moderate3 antivirus results marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
- MinorThe captured page content names no operator, registration ID, address, phone or email; the footer was past the read limit and was not reviewed.
What pushed the score up
- SupportsThe browser threat feed returned no threat warning for the URL.
- SupportsThe saved TLS check found a valid encrypted connection.
- SupportsThe hosting address has an abuse confidence score of 0/100 across zero saved reports.
- SupportsThe domain is 2229 days old, registered in September 2020 through Alibaba Cloud Computing in Beijing with ownership not publicly available.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
Lost money or shared details on cherrybetty.com? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on cherrybetty.com, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Report the domain to its registrar
Alibaba Cloud Computing (Beijing) Co., Ltd. takes abuse reports at domainabuse@service.aliyun.com (+86.95187). Include the address and what happened.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 · Investigation Brief
Investigation Brief
cherrybetty.com is a Shoplazza-hosted women's fashion storefront selling embroidered western shirts, blouses and dresses, with coupon banners, struck-through comparison prices and an email-capture pop-up offering $60 off. The technical side is not the problem: Safe Browsing is clean, the certificate is valid and the CDN address has no abuse reports. The problem is the merchant. No operator name, address, phone or email appears in the page content we captured, and the footer was beyond our read limit so it went unreviewed. Independent checks describe 199 an independent review platform's reviews averaging 1.2 stars, a 'mostly dissatisfied' rating, and reviewers saying the products do not match the photos, sizing is wrong and messages go unanswered. Security vendors also classify the domain as a suspected fake shop. That combination puts it in the High Risk band.
What buyers and independent checks report
An independent business check reports that the shop's 199 an independent review platform's reviews average only 1.2 out of 5 and summarises customer satisfaction as mostly dissatisfied. The same source says it could not find an address, an email address or a phone number for the business.
A review excerpt describes the delivered goods as not matching what the site shows, poor quality and inaccurately sized, and says the shop does not answer messages on social media or by email.
Security vendors go further than reputation: one scanner blocks the site as a suspected shop and says it shows characteristics commonly associated with fraudulent online stores, including suspicious prices and payment methods, and another lists it under a fake-shop risk label alongside blacklisting by security providers.
Clean connection, unclear merchant
Nothing in the connection itself is malicious. The browser threat feed returned no threat warning, the saved TLS check found a valid encrypted connection, and the hosting address carries an abuse confidence score of 0/100 across zero saved reports. A saved antivirus aggregation does mark the URL suspicious in three engines, but that observation is stale, so it is a reputation signal rather than a fresh detection.
The merchant side is where the risk sits. The page we captured names no operator, registration ID, address, phone, domain email or social links, and because the page ran past our read limit the footer contact details were never reviewed, so we cannot say what is or is not listed there. The domain itself is not new — it was registered in September 2020 through Alibaba Cloud Computing in Beijing, with ownership details not publicly available.
Why the score is 38
3 independent sources carry complaints or warnings about this site, including: "Be cautious: its 199 reviews on Trustpilot average only 1.2 stars out of 5. We could not find an address, an email address or a phone number.".
02 · Security Evidence
Security evidence
Antivirus Engines
3/ 93
detectionsSaved analysis from November 3, 2026 - stale
3 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 0
- Suspicious
- 3
- Total
- 93
| Engine | Finding |
|---|---|
| alphaMountain.aiSuspicious | suspicious |
| ESETSuspicious | suspicious |
| GridinsoftSuspicious | suspicious |
All 93 engine results
- alphaMountain.ai - Suspicious
- ESET - Suspicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Clean
- Fortinet - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiShopping, Suspicious
- BitDefenderonlineshop
- Forcepoint ThreatSeekershopping
- Googleshopping
- Sophosonline shopping
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Visual context from the captured page
Header shows the wordmark 'CHERYBETTY' (rendered with a single R) next to a US flag, 'USD' currency selector, search, account and cart icons. A dark top bar reads '$20 Coupon order $149+ Code: BFCM149'. A centered modal overlays the page with a '$60 OFF Subscribe to get' card and the heading 'SUBSCRIBE ENJOY UP TO $60 OFF?', an 'Email' field with placeholder 'Enter your email', and a yellow 'GET $60 OFF' button. Menu items include 'Weekly New In', 'Luxe Collection', 'Christmas' and 'More links'; a floating 'Rewards' widget sits at lower left. Hero background shows a holiday party scene with models in western-style clothing holding cocktails, with a 'Celebrate the season...' caption and an 'Explore' button.
What the captured page showed
5 observations- 01
Header shows the wordmark 'CHERYBETTY' (rendered with a single R) next to a US flag, 'USD' currency selector, search, account and cart icons.
- 02
A dark top bar reads '$20 Coupon order $149+ Code: BFCM149'.
- 03
A centered modal overlays the page with a '$60 OFF Subscribe to get' card and the heading 'SUBSCRIBE ENJOY UP TO $60 OFF?', an 'Email' field with placeholder 'Enter your email', and a yellow 'GET $60 OFF' button.
- 04
Menu items include 'Weekly New In', 'Luxe Collection', 'Christmas' and 'More links'; a floating 'Rewards' widget sits at lower left.
- 05
Hero background shows a holiday party scene with models in western-style clothing holding cocktails, with a 'Celebrate the season...' caption and an 'Explore' button.
What the page says about itself
Quoted from the pages we read: the site's own words, not our findings.
- Page title
CHERRYBETTY – Vintage Western Shirts & Blouses for Women
- Meta description
CHERRYBETTY is an online boutique for exclusive vintage western women’s fashion, featuring unique embroidered shirts and blouses, along with dresses and stylish accessories.
Pages we read
- Main page/Read
03 · Investigation Story
Investigation story
What the site claims
CHERRYBETTY – Vintage Western Shirts & Blouses for Women
What we observed
The page content was captured and checked alongside 60 antivirus results.
What independent research found
8 external findings were saved and compared with the page evidence.
What remains unverified
1 of the 6 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What kind of site and risk is this?
Threat category
Fake Shop & Commercial Deception
Service and business model
Shop
Observed behavior
Evidence behind this classification
- 013 independent sources carry complaints or warnings about this site, including: "O Gridinsoft bloqueia este site porque ele foi classificado como loja suspeita."
- 023 independent sources carry complaints or warnings about this site, including: "Be cautious: its 199 reviews on Trustpilot average only 1.2 stars out of 5. We could not find an address, an email address or a phone number."
- 033 independent sources carry complaints or warnings about this site, including: "Patterns don’t match what they show you on their site. Poor quality, sizing is inaccurate. They do not respond to messages on social media or email."
If this is a scam — what it means for you
What happens when you shop here
On arrival a modal asks for your email address in exchange for '$60 OFF', and the top bar pushes tiered coupon codes such as $20 off orders over $149. The screenshot shows no subscription or recurring-charge terms attached to that email capture.
If this is a scam, how it works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
If you go on to order, the documented outcome from reviewers is goods that do not match the listing, poor quality and wrong sizing, with no reply when you try to raise it by email or social media. We found no page evidence of non-delivery, refund obstruction or hidden charges, so those specific mechanics are not confirmed here.
Do not place an order here. The shop hides who runs it, independent reviewers rate it 1.2 stars across 199 reviews and describe goods that do not match the listings with no support response, and security vendors label it a suspected fake shop. If you have already paid, dispute the charge with your card issuer or payment provider rather than waiting on the shop's support.
Web research findings
Independent findings for cherrybetty.com, including public complaints, named review sources, registration records, and look-alike-domain evidence.
- Gridinsoft (Portuguese)open
"O Gridinsoft bloqueia este site porque ele foi classificado como loja suspeita."
- Gridinsoft (Portuguese)open
"Este site mostra características comumente associadas a lojas online fraudulentas, incluindo preços e métodos de pagamento suspeitos."
- Gridinsoft (German)open
"Gridinsoft bewertet cherrybetty.com, mit Fokus auf verdächtige Inhaltsindikatoren (Fake Shop - Risk, Blacklisted by Security Providers, Low BBB Reviews)"
- Truth Signalopen
"Be cautious: its 199 reviews on Trustpilot average only 1.2 stars out of 5. We could not find an address, an email address or a phone number."
- Truth Signalopen
"Customer satisfaction: mostly dissatisfied"
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domaincherrybetty.com
- Redirects towww.cherrybetty.com
- Hosted byCloudflare, Inc.
- Referencesimg.staticdj.com · static.staticdj.com
Domain Timeline
- Sep 29, 2020Domain registered
First appeared in WHOIS records — 6 years old when this review was saved.
- Nov 6, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
cherrybetty.com is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Report this domain to its registrar: send the address and what happened to this contact.
Certificate issued for www.cherrybetty.com.
A shared Cloudflare address answers for many sites, so it is not the site's own server and says nothing about who runs it.
Analytics and ads
- Google Tag Manager
Scripts, fonts and CDNs
- Google Fonts
Payment providers the page loads
None seen among the outside domains we saved.
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://cherrybetty.com/
- 2301https://cherrybetty.com/
- 3200https://www.cherrybetty.com/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
unknownMalware, phishing, credential theft and hostile infrastructure.
3 antivirus results marked the URL as suspicious. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
3 independent sources carry complaints or warnings about this site, including: "Be cautious: its 199 reviews on Trustpilot average only 1.2 stars out of 5. We could not find an address, an email address or a phone number." · 3 independent sources carry complaints or warnings about this site, including: "O Gridinsoft bloqueia este site porque ele foi classificado como loja suspeita."
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 3 of 93 engines flagged | Limited | Adverse | stale fallback · analysed Nov 3, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 6, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 6, 2026 |
| Visual evidence | 5 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 6, 2026 |
| Independent research | 8 independent findings were saved | Completed | Adverse | this scan · Nov 6, 2026 |
- Antivirus
- Result3 of 93 engines flagged
- CompletionLimitedFindingAdverse
- Freshnessstale fallback · analysed Nov 3, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 6, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 6, 2026
- Visual evidence
- Result5 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 6, 2026
- Independent research
- Result8 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 6, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is cherrybetty.com a scam or a legit online store?
Is cherrybetty.com safe to use?
What should I do if I already gave my details to cherrybetty.com?
Can I get my money back from cherrybetty.com?
I ordered from cherrybetty.com but nothing arrived — is it a fake shop?
How do I report cherrybetty.com?
Why does cherrybetty.com look legitimate if it's a scam?
Has cherrybetty.com been flagged by antivirus engines?
Is cherrybetty.com on any phishing or malware blacklists?
How old is the cherrybetty.com domain?
Does cherrybetty.com have a valid SSL certificate?
How often is the cherrybetty.com report updated?
08 · Final Verdict
Final verdict
Cherrybetty sells vintage-style western clothing from an undisclosed operator, and independent checks rate it 1.2 stars across 199 reviews with security vendors calling it a suspected fake shop.
cherrybetty.com is a Shoplazza-hosted women's fashion storefront selling embroidered western shirts, blouses and dresses, with coupon banners, struck-through comparison prices and an email-capture pop-up offering $60 off. The technical side is not the problem: Safe Browsing is clean, the certificate is valid and the CDN address has no abuse reports. The problem is the merchant. No operator name, address, phone or email appears in the page content we captured, and the footer was beyond our read limit so it went unreviewed. Independent checks describe 199 an independent review platform's reviews averaging 1.2 stars, a 'mostly dissatisfied' rating, and reviewers saying the products do not match the photos, sizing is wrong and messages go unanswered. Security vendors also classify the domain as a suspected fake shop. That combination puts it in the High Risk band.
09 · Community
Community
Are you the owner of cherrybetty.com?Verify and reply