
Is tg-verify-check.online safe?
http://tg-verify-check.online/
Coveragepartial2 of 4 applicable core capabilities
Brand-new lookalike domain impersonating Telegram, flagged as phishing by multiple security engines
tg-verify-check.online is a 150-day-old domain whose name borrows Telegram's brand and a 'verify-check' lure, yet it is not an official Telegram domain. Twelve antivirus families returned an adverse result and independent research flagged it as suspicious and newly registered. The site's own pages could not be reviewed because it immediately redirects visitors to the legitimate Telegram FAQ page, so the operator's identity and intent stay hidden behind that redirect.
Be the first to review tg-verify-check.online
Lost money to tg-verify-check.online? Warn others
Loading saved screenshot
Preparing the saved page preview.
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
01 · Investigation Brief
Investigation Brief
tg-verify-check.online is a 150-day-old domain whose name borrows Telegram's brand and a 'verify-check' lure, yet it is not an official Telegram domain. Twelve antivirus families returned an adverse result and independent research flagged it as suspicious and newly registered. The site's own pages could not be reviewed because it immediately redirects visitors to the legitimate Telegram FAQ page, so the operator's identity and intent stay hidden behind that redirect.
Security engines and researchers flag this domain
A saved antivirus observation records 12 independent antivirus families reporting an adverse result, naming alphaMountain.ai, BitDefender and Chong Lua Dao among them. That detection is real but stale, so its timing should be confirmed rather than assumed current.
Independent research adds that the domain was flagged by 3 of 91 security engines and that web-classification data labeled it suspicious and newly registered. Registration records show it was created on 23 May 2026 through REG.RU LLC, resolving to an IP address in Finland associated with a named individual.
Clean encryption does not offset the operator risk
The technical layer looks unremarkable: the saved TLS check found a valid encrypted connection and the browser threat feed returned no threat warning. Those results mean no detections were recorded, not that the operator is trustworthy.
The operator side is where the risk sits. The domain is only 150 days old, its name mimics Telegram's brand and a verification theme, and its own contact and policy pages were never read in full because the site redirects away immediately. There is no disclosed operator identity to weigh against the phishing flags.
Why the score is 18
12 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing. Coverage remains separate so missing sources cannot be mistaken for clean results.
02 · Security Evidence
Security evidence
Antivirus Engines
15/ 92
detectionsSaved analysis from October 2, 2026 - stale
15 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 13
- Suspicious
- 2
- Total
- 92
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | phishing |
| BitDefenderMalicious | phishing |
| Chong Lua DaoMalicious | malicious |
| CyRadarMalicious | phishing |
| ESETMalicious | phishing |
| Forcepoint ThreatSeekerMalicious | phishing |
| G-DataMalicious | phishing |
| KasperskyMalicious | phishing |
| LevelBlueMalicious | phishing |
| LionicMalicious | phishing |
| RisingMalicious | phishing |
| SophosMalicious | phishing |
| VIPREMalicious | phishing |
| FortinetSuspicious | spam |
| GridinsoftSuspicious | suspicious |
All 92 engine results
- alphaMountain.ai - phishing - Malicious
- BitDefender - phishing - Malicious
- Chong Lua Dao - Malicious
- CyRadar - phishing - Malicious
- ESET - phishing - Malicious
- Forcepoint ThreatSeeker - phishing - Malicious
- G-Data - phishing - Malicious
- Kaspersky - phishing - Malicious
- LevelBlue - phishing - Malicious
- Lionic - phishing - Malicious
- Rising - phishing - Malicious
- Sophos - phishing - Malicious
- VIPRE - phishing - Malicious
- Fortinet - spam - Suspicious
- Gridinsoft - Suspicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Fortra - Unrated
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Seclookup - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Loading saved screenshot
Preparing the saved page preview.
Visual context from the captured page
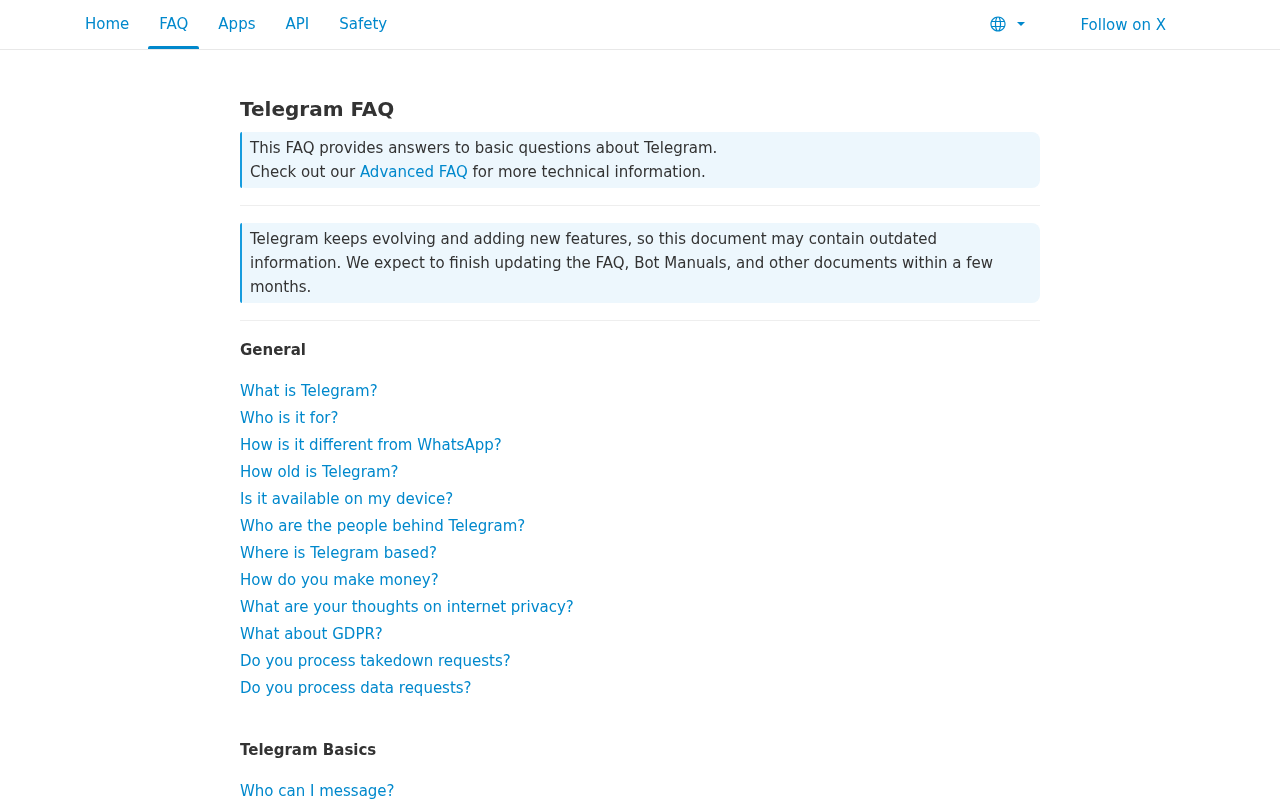
The screenshot shows the official Telegram FAQ page, which the site redirects to.
What the captured page showed
1 observation- 01
The screenshot shows the official Telegram FAQ page, which the site redirects to.
03 · Investigation Story
Investigation story
What the site claims
Loading
What we observed
The page content was captured and checked alongside 61 antivirus results.
What independent research found
2 external findings were saved and compared with the page evidence.
What remains unverified
2 of the 4 applicable core capabilities did not complete, so those gaps remain visible in the coverage ledger.
What this means for you
What a visitor actually experiences
A visitor arriving at tg-verify-check.online is not shown a verification form or any site content; the page automatically sends the browser to an unrelated external site, the official Telegram FAQ at telegram.org/faq.
How the observed mechanism works
The evidence-backed path
Each stage below is preserved from the grounded analysis and linked to saved evidence.
The screenshot confirms the landing view is the official Telegram FAQ page, which the redirect delivers. That redirect obscures the site's real purpose and leaves the phishing mechanism unresolved, while the domain's name still trades on Telegram's brand.
Do not enter any Telegram login code, password or personal details on tg-verify-check.online, and do not treat it as an official Telegram service. If you reached it from a message claiming your account needs verification, go to Telegram directly through its official app or telegram.org instead, and report the link.
Web research findings
Independent findings for tg-verify-check.online, including public complaints, named review sources, registration records, and look-alike-domain evidence. A missing result is shown as unverified, never converted into a clean bill of health.
- PhishDestroyopen
"The domain tg-verify-check.online was registered on 23 May 2026 through REG.RU LLC and is currently active. DNS resolution points to the IPv4 address 87.120.107.209, which geolocates to Finland and is associated with the name Mykyta Skorobohatko."
- PCriskopen
"This domain shows several cautionary signals at the time of this scan. It was flagged by 3 out of 91 security engines, and web-classification data labeled it as suspicious and newly registered."
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too. Use this to corroborate the verdict, not to overturn it.
Infrastructure map
How the saved page connected to the wider web.
- Domaintg-verify-check.online
- Redirects totg-verify-check.online
- Hosted byShinomiya-Hosting
- Referencesfonts.googleapis.com · fonts.gstatic.com
Domain Timeline
- May 21, 2026Domain registered
First appeared in WHOIS records — 5 months old when this review was saved.
- Oct 19, 2026Saved security review — Rated Dangerous
The completed checks from this saved scan are detailed above.
tg-verify-check.online was registered very recently when this review was saved and was already flagged. Freshly-registered domains are disproportionately used for scams, and a young domain with active threat signals warrants extra caution.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
Domain & Encryption
Redirect Chain
- 1308http://tg-verify-check.online/
- 2200https://tg-verify-check.online/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruspartial
- Browser threat feedcomplete
- Page contentpartial
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
suspiciousMalware, phishing, credential theft and hostile infrastructure.
12 independent antivirus families reported an adverse result. This comes from a saved antivirus observation rather than a new submission, so treat the detection as real but confirm the timing.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
The page automatically sent the browser to an unrelated external site.
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 15 of 92 engines flagged | Limited | Adverse | stale fallback · analysed Oct 2, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Oct 19, 2026 |
| Page content | Page fetched · HTTP 200 | Limited | No saved finding | this scan · Oct 19, 2026 |
| Visual evidence | 1 visible observation saved with the page capture | Completed | No adverse finding | this scan · Oct 19, 2026 |
| Independent research | 2 independent findings were saved | Completed | Adverse | this scan · Oct 19, 2026 |
- Antivirus
- Result15 of 92 engines flagged
- CompletionLimited
- FindingAdverse
- Freshnessstale fallback · analysed Oct 2, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 19, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionLimited
- FindingNo saved finding
- Freshnessthis scan · Oct 19, 2026
- Visual evidence
- Result1 visible observation saved with the page capture
- CompletionCompleted
- FindingNo adverse finding
- Freshnessthis scan · Oct 19, 2026
- Independent research
- Result2 independent findings were saved
- CompletionCompleted
- FindingAdverse
- Freshnessthis scan · Oct 19, 2026
07 · Safety FAQ
Safety FAQ
Common questions, answered directly from the scan data above — so the answers reflect the saved verdict and evidence in this report.
Is tg-verify-check.online a scam or a legit website?
Is tg-verify-check.online safe to use?
I already paid or entered my details on tg-verify-check.online — what should I do?
Can I get my money back from tg-verify-check.online?
Is my device at risk after visiting tg-verify-check.online?
How do I report tg-verify-check.online?
tg-verify-check.online looks professional — how can it still be a scam?
Has tg-verify-check.online been flagged by antivirus engines?
Is tg-verify-check.online on any phishing or malware blacklists?
How old is the tg-verify-check.online domain?
Where is tg-verify-check.online hosted?
How often is the tg-verify-check.online report updated?
08 · Final Verdict
Final verdict
Brand-new lookalike domain impersonating Telegram, flagged as phishing by multiple security engines
tg-verify-check.online is a 150-day-old domain whose name borrows Telegram's brand and a 'verify-check' lure, yet it is not an official Telegram domain. Twelve antivirus families returned an adverse result and independent research flagged it as suspicious and newly registered. The site's own pages could not be reviewed because it immediately redirects visitors to the legitimate Telegram FAQ page, so the operator's identity and intent stay hidden behind that redirect.
09 · Community