

Is getpaymentservices.com safe?
http://getpaymentservices.com/
Checked on
How we checked
Coverage: complete · 6 of 6 applicable core capabilities
- Antivirus (59 of 93 engines answered): completed
- Google Safe Browsing: completed
- page reading: completed
- page capture: completed
- domain records: completed
- web research: completed
Adobe- and PayPal-branded payment page with no named operator, legal terms hosted on an unrelated domain, and four antivirus vendors flagging it
getpaymentservices.com is a marketing page for "Payment Services for Adobe Commerce and Magento Open Source," built on PayPal Complete Payments, carrying an Adobe Commerce wordmark and Adobe/PayPal support labels. Nothing on the page says who runs it: no company name, registration, email, phone or address is visible, and the Privacy Policy and Terms of Use links lead to bridge.partners, a domain with no stated tie to Adobe or PayPal. Four antivirus families flag the host as malicious or phishing, while the browser threat feed shows no warning and the certificate is valid. Brand impersonation plus an undisclosed operator and adverse vendor verdicts put this in the High Risk band.
 Saved site captureCaptured safely during this scan4 antivirus engines flagged this URLalphaMountain.ai, ESET, Fortinet, Seclookup
Where this site sits
- Dangerous1–20
- High Risk21–44
- Moderate Risk45–69
- Low Risk70–84
- Safe85–100
The score combines saved evidence strength and analysis quality. Coverage is reported separately.
Why 38/100
High Risk covers scores 21–44. 4 findings pulled the score down; 2 pushed it up.
What pulled the score down
- Decisive4 independent antivirus families reported an adverse result.
- ModerateThe page uses Adobe Commerce branding and PayPal product claims but discloses no company, registration, email, phone or address.
- ModeratePrivacy Policy and Terms of Use links point to bridge.partners, a domain with no stated relationship to Adobe or PayPal.
- ModerateOne public warning on a scam-warning or security site: "该网站因多个风险信号被归类为可疑商店,包括5 个黑名单命中和尚无稳定的公开用户评价历史。"
What pushed the score up
- SupportsThe browser threat feed returned no warning and the saved TLS check found a valid encrypted connection.
- SupportsThe registrable domain is 753 days old and hosted on infrastructure with a low abuse confidence score of 7/100.
No points per finding are stored for this report: our analysis weighed all findings together to set the score. Each finding shows its saved severity instead (Decisive, Strong, Moderate or Minor).
Lost money or shared details on getpaymentservices.com? Do this now
Act quickly: the first hours matter most for a chargeback.
- Call your bank or card issuer now
Ask them to dispute the charge or open a chargeback; the sooner you act, the better your odds. Card payments can often be reversed. Bank transfers and gift cards are harder, but report them to your bank too. Crypto payments usually cannot be reversed: report the wallet address and transaction ID to the exchange you sent from.
- Change any password you entered
If you entered a password on getpaymentservices.com, change it there and anywhere you reused it, and turn on two-factor authentication. Keep screenshots, order confirmations and messages as evidence.
- Report the site
Reports help get scam sites taken down faster and warn other people.
- Report the domain to its registrar
GoDaddy.com, LLC takes abuse reports at abuse@godaddy.com (480-624-2505). Include the address and what happened.
- Ignore anyone offering to recover your money
"Recovery" services or agents who contact you, or ask for a fee up front, are almost always a second scam aimed at victims. Your bank's dispute process and the official reporting services never charge a fee in advance.
Full answers about refunds and reporting are in the Safety FAQ below.
01 · Investigation Brief
Investigation Brief
getpaymentservices.com is a marketing page for "Payment Services for Adobe Commerce and Magento Open Source," built on PayPal Complete Payments, carrying an Adobe Commerce wordmark and Adobe/PayPal support labels. Nothing on the page says who runs it: no company name, registration, email, phone or address is visible, and the Privacy Policy and Terms of Use links lead to bridge.partners, a domain with no stated tie to Adobe or PayPal. Four antivirus families flag the host as malicious or phishing, while the browser threat feed shows no warning and the certificate is valid. Brand impersonation plus an undisclosed operator and adverse vendor verdicts put this in the High Risk band.
Adobe and PayPal branding over an unnamed operator
The page is dressed as an official Adobe Commerce property: the header carries an Adobe Commerce wordmark, the hero reads "Payment Services," and the copy describes a fully integrated solution for Adobe Commerce and Magento Open Source built on PayPal Complete Payments. Adobe support and PayPal support labels sit alongside the product claims.
Yet the rendered page shows no company name, address, phone number, email address or operator disclosure, and no direct contact email was found on the captured page. A payment-services site that borrows two major brands' identities without naming the business behind it gives a merchant no way to check who is actually collecting anything.
The legal pages reinforce the gap: the Privacy Policy and Terms of Use links resolve to bridge.partners, a third-party domain unrelated to Adobe or PayPal, so the entity behind the branding is not identified on-site. The domain itself was registered on 13 October 2024 through GoDaddy.
Split technical verdict: vendor flags against a clean browser check
Four of 93 engines returned malicious results with none suspicious, and four independent antivirus families reported an adverse result, including a phishing verdict and a malware verdict. That is a direct technical warning about this host, not a generic category guess.
The counterweight is real but partial: the browser threat feed returned no threat warning, the saved TLS check found a valid encrypted connection, and the hosting IP carries a low abuse confidence score of 7/100 across three saved reports. The domain is also 753 days old, which argues against a throwaway host. Clean transport and a clean browser list mean no detection, not that the operator is trustworthy.
Independent research adds a second adverse view: a scanner-based write-up classifies the site as a suspicious store citing five blacklist hits and no stable public review history, and describes it as a fraudulent e-commerce site using deceptive tactics to collect payments and personal data. That is a third-party assessment rather than a verified customer account, so it is weighed as supporting context.
Where the buttons actually send a visitor
The "Contact" and "Contact us" buttons leave the site for business.adobe.com's payment-services resources page, so the merchant onboarding path terminates on Adobe's own business site rather than on this host. Payment-method documentation links (Apple Pay, Google Pay, advanced eligibility, country availability) go to developer.paypal.com and paypal.com.
The only same-site commercial action is a "Read the case study" link to a PDF on the site's own file path, and the page's statistics cite PYMNTS Intelligence and Adobe studies. No affiliate or referral parameters appear in the outbound links, so a referral funnel is not demonstrated by the link graph; the concern here is the borrowed brand identity and the hidden operator, not a redirect chain.
Why the score is 38
4 independent antivirus families reported an adverse result.
02 · Security Evidence
Security evidence
Antivirus Engines
4/ 93
detectionsFresh result
4 engines flagged this URL
Every saved adverse engine is listed below. The full provider matrix remains available for audit.
- Malicious
- 4
- Suspicious
- 0
- Total
- 93
| Engine | Finding |
|---|---|
| alphaMountain.aiMalicious | malicious |
| ESETMalicious | phishing |
| FortinetMalicious | malware |
| SeclookupMalicious | malicious |
All 93 engine results
- alphaMountain.ai - Malicious
- ESET - phishing - Malicious
- Fortinet - malware - Malicious
- Seclookup - Malicious
- 0xSI_f33d - Unrated
- Abusix - Clean
- Acronis - Clean
- ADMINUSLabs - Clean
- AILabs (MONITORAPP) - Clean
- AlienVault - Clean
- AlphaSOC - Unrated
- Antiy-AVL - Clean
- ArcSight Threat Intelligence - Unrated
- AutoShun - Unrated
- Bfore.Ai PreCrime - Unrated
- BitDefender - Clean
- Bkav - Unrated
- BlockList - Clean
- Blueliv - Clean
- Certego - Clean
- ChainPatrol - Unrated
- Chong Lua Dao - Clean
- CINS Army - Clean
- CRDF - Clean
- Criminal IP - Unrated
- CSIS Security Group - Unrated
- CTX AI - Clean
- Cyan - Unrated
- Cyble - Clean
- CyRadar - Clean
- desenmascara.me - Clean
- DNS8 - Unrated
- Dr.Web - Clean
- EmergingThreats - Clean
- Emsisoft - Clean
- Ermes - Unrated
- ESTsecurity - Clean
- Forcepoint ThreatSeeker - Clean
- Fortra - Unrated
- G-Data - Clean
- GCP Abuse Intelligence - Unrated
- Google Safe Browsing - Clean
- GreenSnow - Clean
- GreyNoise - Unrated
- Gridinsoft - Unrated
- Guardpot - Unrated
- Heimdal Security - Clean
- Hunt.io Intelligence - Unrated
- IPsum - Clean
- Juniper Networks - Clean
- K7AntiVirus - Unrated
- Kaspersky - Clean
- LevelBlue - Clean
- Lionic - Clean
- Lumu - Unrated
- Malwared - Clean
- MalwarePatrol - Clean
- MalwareURL - Unrated
- Mimecast - Unrated
- Netcraft - Unrated
- OpenPhish - Clean
- Orcapot - Unrated
- PhishFort - Unrated
- Phishing Database - Clean
- Phishtank - Clean
- PREBYTES - Clean
- PrecisionSec - Unrated
- Quick Heal - Clean
- Quttera - Clean
- Rising - Clean
- SafeToOpen - Unrated
- Sangfor - Clean
- Sansec eComscan - Unrated
- Scantitan - Clean
- SCUMWARE.org - Clean
- Snort IP sample list - Unrated
- SOCRadar - Unrated
- Sophos - Clean
- StopForumSpam - Clean
- Sucuri SiteCheck - Clean
- Synthient - Unrated
- ThreatHive - Clean
- URLhaus - Clean
- URLQuery - Unrated
- Viettel Threat Intelligence - Clean
- VIPRE - Unrated
- ViriBack - Clean
- VX Vault - Clean
- Webroot - Clean
- Xcitium Verdict Cloud - Clean
- Yandex Safebrowsing - Clean
- ZeroCERT - Clean
- ZeroFox - Unrated
How security vendors categorise this site
- alphaMountain.aiMalicious
- Forcepoint ThreatSeekerfinancial data and services
- Googletechnology
Each vendor’s own label for the site, saved with the antivirus result. Labels are separate from the engine verdicts above and can disagree with each other.
Security Scans
Checked against the browser threat feeds available to this scan — no hit.
What we observed
Visual context from the captured page
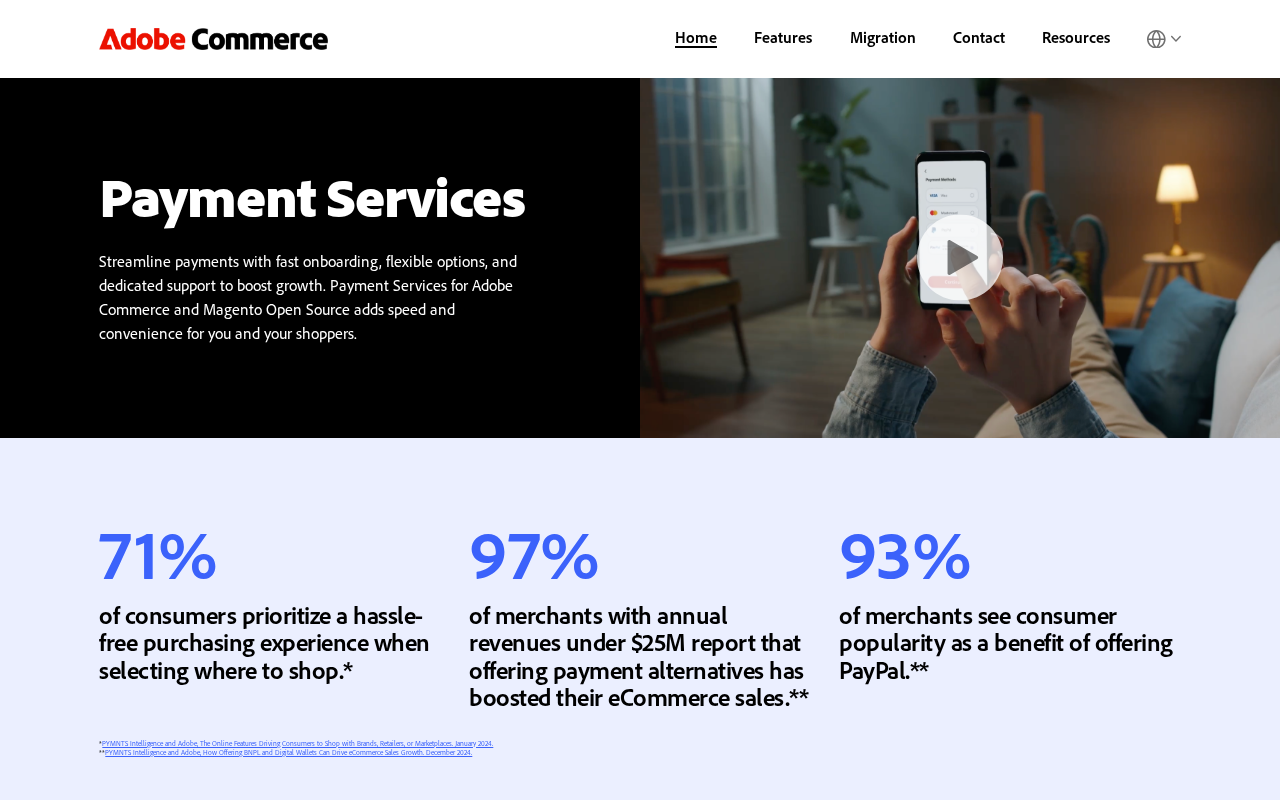
Header shows an 'Adobe Commerce' wordmark logo at top-left, with nav items Home, Features, Migration, Contact, Resources and a language globe selector. Hero reads 'Payment Services' with subtext about streamlining payments with fast onboarding, flexible options and dedicated support for Adobe Commerce and Magento Open Source. Hero right side shows a video player thumbnail of hands holding a smartphone with a payment screen, overlaid with a play button. Three large statistics displayed: 71% of consumers prioritize a hassle-free purchasing experience; 97% of merchants under $25M revenue report payment alternatives boosted sales; 93% of merchants see consumer popularity as a benefit of offering PayPal. Small footnote text cites PYMNTS Intelligence and Adobe studies from January 2024 and December 2024. No company name, address, phone number, email address or operator disclosure is visible in the rendered viewport.
What the captured page showed
6 observations- 01
Header shows an 'Adobe Commerce' wordmark logo at top-left, with nav items Home, Features, Migration, Contact, Resources and a language globe selector.
- 02
Hero reads 'Payment Services' with subtext about streamlining payments with fast onboarding, flexible options and dedicated support for Adobe Commerce and Magento Open Source.
- 03
Hero right side shows a video player thumbnail of hands holding a smartphone with a payment screen, overlaid with a play button.
- 04
Three large statistics displayed: 71% of consumers prioritize a hassle-free purchasing experience; 97% of merchants under $25M revenue report payment alternatives boosted sales; 93% of merchants see consumer popularity as a benefit of offering PayPal.
- 05
Small footnote text cites PYMNTS Intelligence and Adobe studies from January 2024 and December 2024.
- 06
No company name, address, phone number, email address or operator disclosure is visible in the rendered viewport.
What the page says about itself
Quoted from the pages we read: the site's own words, not our findings.
- Page title
Payment Services for Adobe Commerce
- Meta description
Streamline payment processing with Payment Services for Adobe Commerce & Magento, offering secure, flexible payment options and fast onboarding.
Pages we read
- Main page/Read
03 · Investigation Story
Investigation story
What the site claims
Payment Services for Adobe Commerce
What we observed
The page content was captured and checked alongside 59 antivirus results.
What independent research found
5 external findings were saved and compared with the page evidence.
What remains unverified
The checks completed, but ownership, business claims, and future site behavior can still change after this snapshot.
What kind of site and risk is this?
Threat category
Phishing & Impersonation
Service and business model
Financial Service
Observed behavior
Evidence behind this classification
- 01Four of 93 engines returned malicious results, with four independent antivirus families reporting adverse verdicts including phishing and malware labels.
- 024 independent antivirus families reported an adverse result.
- 03The page uses Adobe Commerce branding and PayPal product claims but discloses no company, registration, email, phone or address.
Web research findings
Independent findings for getpaymentservices.com, including public complaints, named review sources, registration records, and look-alike-domain evidence.
- Adobe Experience Leagueopen
"Payment Services for Adobe Commerce and Magento Open Source is a fully integrated payment solution that allows you to efficiently oversee payment and order data from all of your storefronts in one place"
- Adobe Experience League (preview)open
"Payment Services for Adobe Commerce and Magento Open Source is your turnkey self-service solution, including sandbox testing and a simple setup, for providing robust and secure payment processing for your Commerce websites."
Reputation Sources
How this domain rates across independent threat-intelligence and blocklist providers.
04 · Domain & Infrastructure
Domain & infrastructure
The plumbing behind the site — who registered it, how it’s encrypted, where it’s hosted, and where it links out. A valid certificate or a calm server doesn’t mean the business is honest — scam sites pass these checks too.
Infrastructure map
- Domaingetpaymentservices.com
- Redirects towww.getpaymentservices.com
- Hosted byHubSpot, Inc.
- Referencesgoogletagmanager.com · cookie-cdn.cookiepro.com
Domain Timeline
- Oct 13, 2024Domain registered
First appeared in WHOIS records — 2 years old when this review was saved.
- Nov 5, 2026Saved security review — Rated High Risk
The completed checks from this saved scan are detailed above.
getpaymentservices.com is an established domain now carrying threat signals. An older domain that starts tripping security checks is a classic pattern for an asset that was sold, repurposed, or compromised — the age alone is not reassurance.
Contact Verification
Saved contact details can help identify the operator. Their presence supports traceability; it does not prove the business is trustworthy.
- No direct contact email found on the captured page.
Domain & Encryption
Report this domain to its registrar: send the address and what happened to this contact.
Certificate issued for c83a9410.sni.cloudflaressl.com.
A shared content-delivery network address answers for many sites, so it is not the site's own server and says nothing about who runs it.
Analytics and ads
- Google Tag Manager
Scripts, fonts and CDNs
- jQuery CDN
Payment providers the page loads
- PayPal
Read from the first 20 outside domains the page loads and the shop platform it uses; the web server and platform rows are under Hosting & Technology. A payment script on the page does not prove the shop accepts that method at checkout, or that you are protected.
Redirect Chain
- 1301http://getpaymentservices.com/
- 2301https://getpaymentservices.com/
- 3200https://www.getpaymentservices.com/
Server Reputation
Referenced Domains
Outbound domains this page links to or loads resources from. Each links to its own security scan.
05 · Evidence Ledger
Evidence ledger
- Antiviruscomplete
- Browser threat feedcomplete
- Page contentcomplete
- Analysiscomplete
- Visual evidencecomplete
The conclusion is supported by the evidence saved with this report.
Technical threat
maliciousMalware, phishing, credential theft and hostile infrastructure.
4 independent antivirus families reported an adverse result. · The page uses Adobe Commerce branding and PayPal product claims but discloses no company, registration, email, phone or address.
Operator / customer risk
suspiciousComplaints, withdrawals, business conduct and commercial traps.
One public warning on a scam-warning or security site: "该网站因多个风险信号被归类为可疑商店,包括5 个黑名单命中和尚无稳定的公开用户评价历史。"
Source coverage and freshness
Status shows whether usable evidence was saved; finding shows what that evidence observed.
| Source | Result | Completion | Finding | Freshness |
|---|---|---|---|---|
| Antivirus | 4 of 93 engines flagged | Completed | Adverse | fresh · analysed Nov 4, 2026 |
| Browser protection | No browser threat-list match | Completed | No adverse finding | this scan · Nov 5, 2026 |
| Page content | Page fetched · HTTP 200 | Completed | No adverse finding | this scan · Nov 5, 2026 |
| Visual evidence | 6 visible observations saved with the page capture | Completed | No adverse finding | this scan · Nov 5, 2026 |
| Independent research | 5 independent findings were saved | Completed | Adverse | this scan · Nov 5, 2026 |
- Antivirus
- Result4 of 93 engines flagged
- CompletionCompletedFindingAdverse
- Freshnessfresh · analysed Nov 4, 2026
- Browser protection
- ResultNo browser threat-list match
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 5, 2026
- Page content
- ResultPage fetched · HTTP 200
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 5, 2026
- Visual evidence
- Result6 visible observations saved with the page capture
- CompletionCompletedFindingNo adverse finding
- Freshnessthis scan · Nov 5, 2026
- Independent research
- Result5 independent findings were saved
- CompletionCompletedFindingAdverse
- Freshnessthis scan · Nov 5, 2026
07 · Safety FAQ
Safety FAQ
Answered from the saved verdict and evidence in this report.
Is getpaymentservices.com a scam or a legit website?
Is getpaymentservices.com safe to use?
I already paid or entered my details on getpaymentservices.com — what should I do?
Can I get my money back from getpaymentservices.com?
Did getpaymentservices.com steal my password or personal information?
How do I report getpaymentservices.com?
getpaymentservices.com looks professional — how can it still be a scam?
Has getpaymentservices.com been flagged by antivirus engines?
Is getpaymentservices.com on any phishing or malware blacklists?
How old is the getpaymentservices.com domain?
Does getpaymentservices.com have a valid SSL certificate?
How often is the getpaymentservices.com report updated?
08 · Final Verdict
Final verdict
Adobe- and PayPal-branded payment page with no named operator, legal terms hosted on an unrelated domain, and four antivirus vendors flagging it
getpaymentservices.com is a marketing page for "Payment Services for Adobe Commerce and Magento Open Source," built on PayPal Complete Payments, carrying an Adobe Commerce wordmark and Adobe/PayPal support labels. Nothing on the page says who runs it: no company name, registration, email, phone or address is visible, and the Privacy Policy and Terms of Use links lead to bridge.partners, a domain with no stated tie to Adobe or PayPal. Four antivirus families flag the host as malicious or phishing, while the browser threat feed shows no warning and the certificate is valid. Brand impersonation plus an undisclosed operator and adverse vendor verdicts put this in the High Risk band.
09 · Community
Community
Are you the owner of getpaymentservices.com?Verify and reply